Si deseas distinguir tus productos, servicios o ambos de los de otra empresa, es posible que necesites una marca o nombre comercial. Descubre qué son, en qué consiste su procedimiento de registro y qué implica.

Información sobre los plazos de presentación de solicitudes de transformación de marcas de la Unión Europea en marca nacional española. Más información


Si tienes un nuevo dispositivo, producto o procedimiento que resuelva un problema técnico o tenga una ventaja práctica, existen distintas formas de protegerlo en España y en otros países. Descubre cómo hacerlo.

¿Tu innovación reside en la estética, la ornamentación o la apariencia de tu producto? Protégela mediante un diseño industrial. Descubre qué derechos confiere el registro y cómo realizar la tramitación.

Las indicaciones geográficas protegen el nombre de un producto originario de una zona geográfica, a la cual le debe una determinada calidad, reputación u otra característica. Descubre qué son, en qué consiste su procedimiento de registro y qué beneficios conceden.

Las patentes publicadas en todo el mundo son una valiosa fuente de información científica, técnica y comercial.

Si eres emprendedor/a o una empresa y quieres potenciar y mejorar la rentabilidad de tu negocio protegiendo de forma adecuada los activos intangibles de tu organización, en este espacio encontrarás lo necesario.


 140
resultados
 Última actualización
16/11/2026 [21:59:00]


 Resultados 25 a 50 de 140

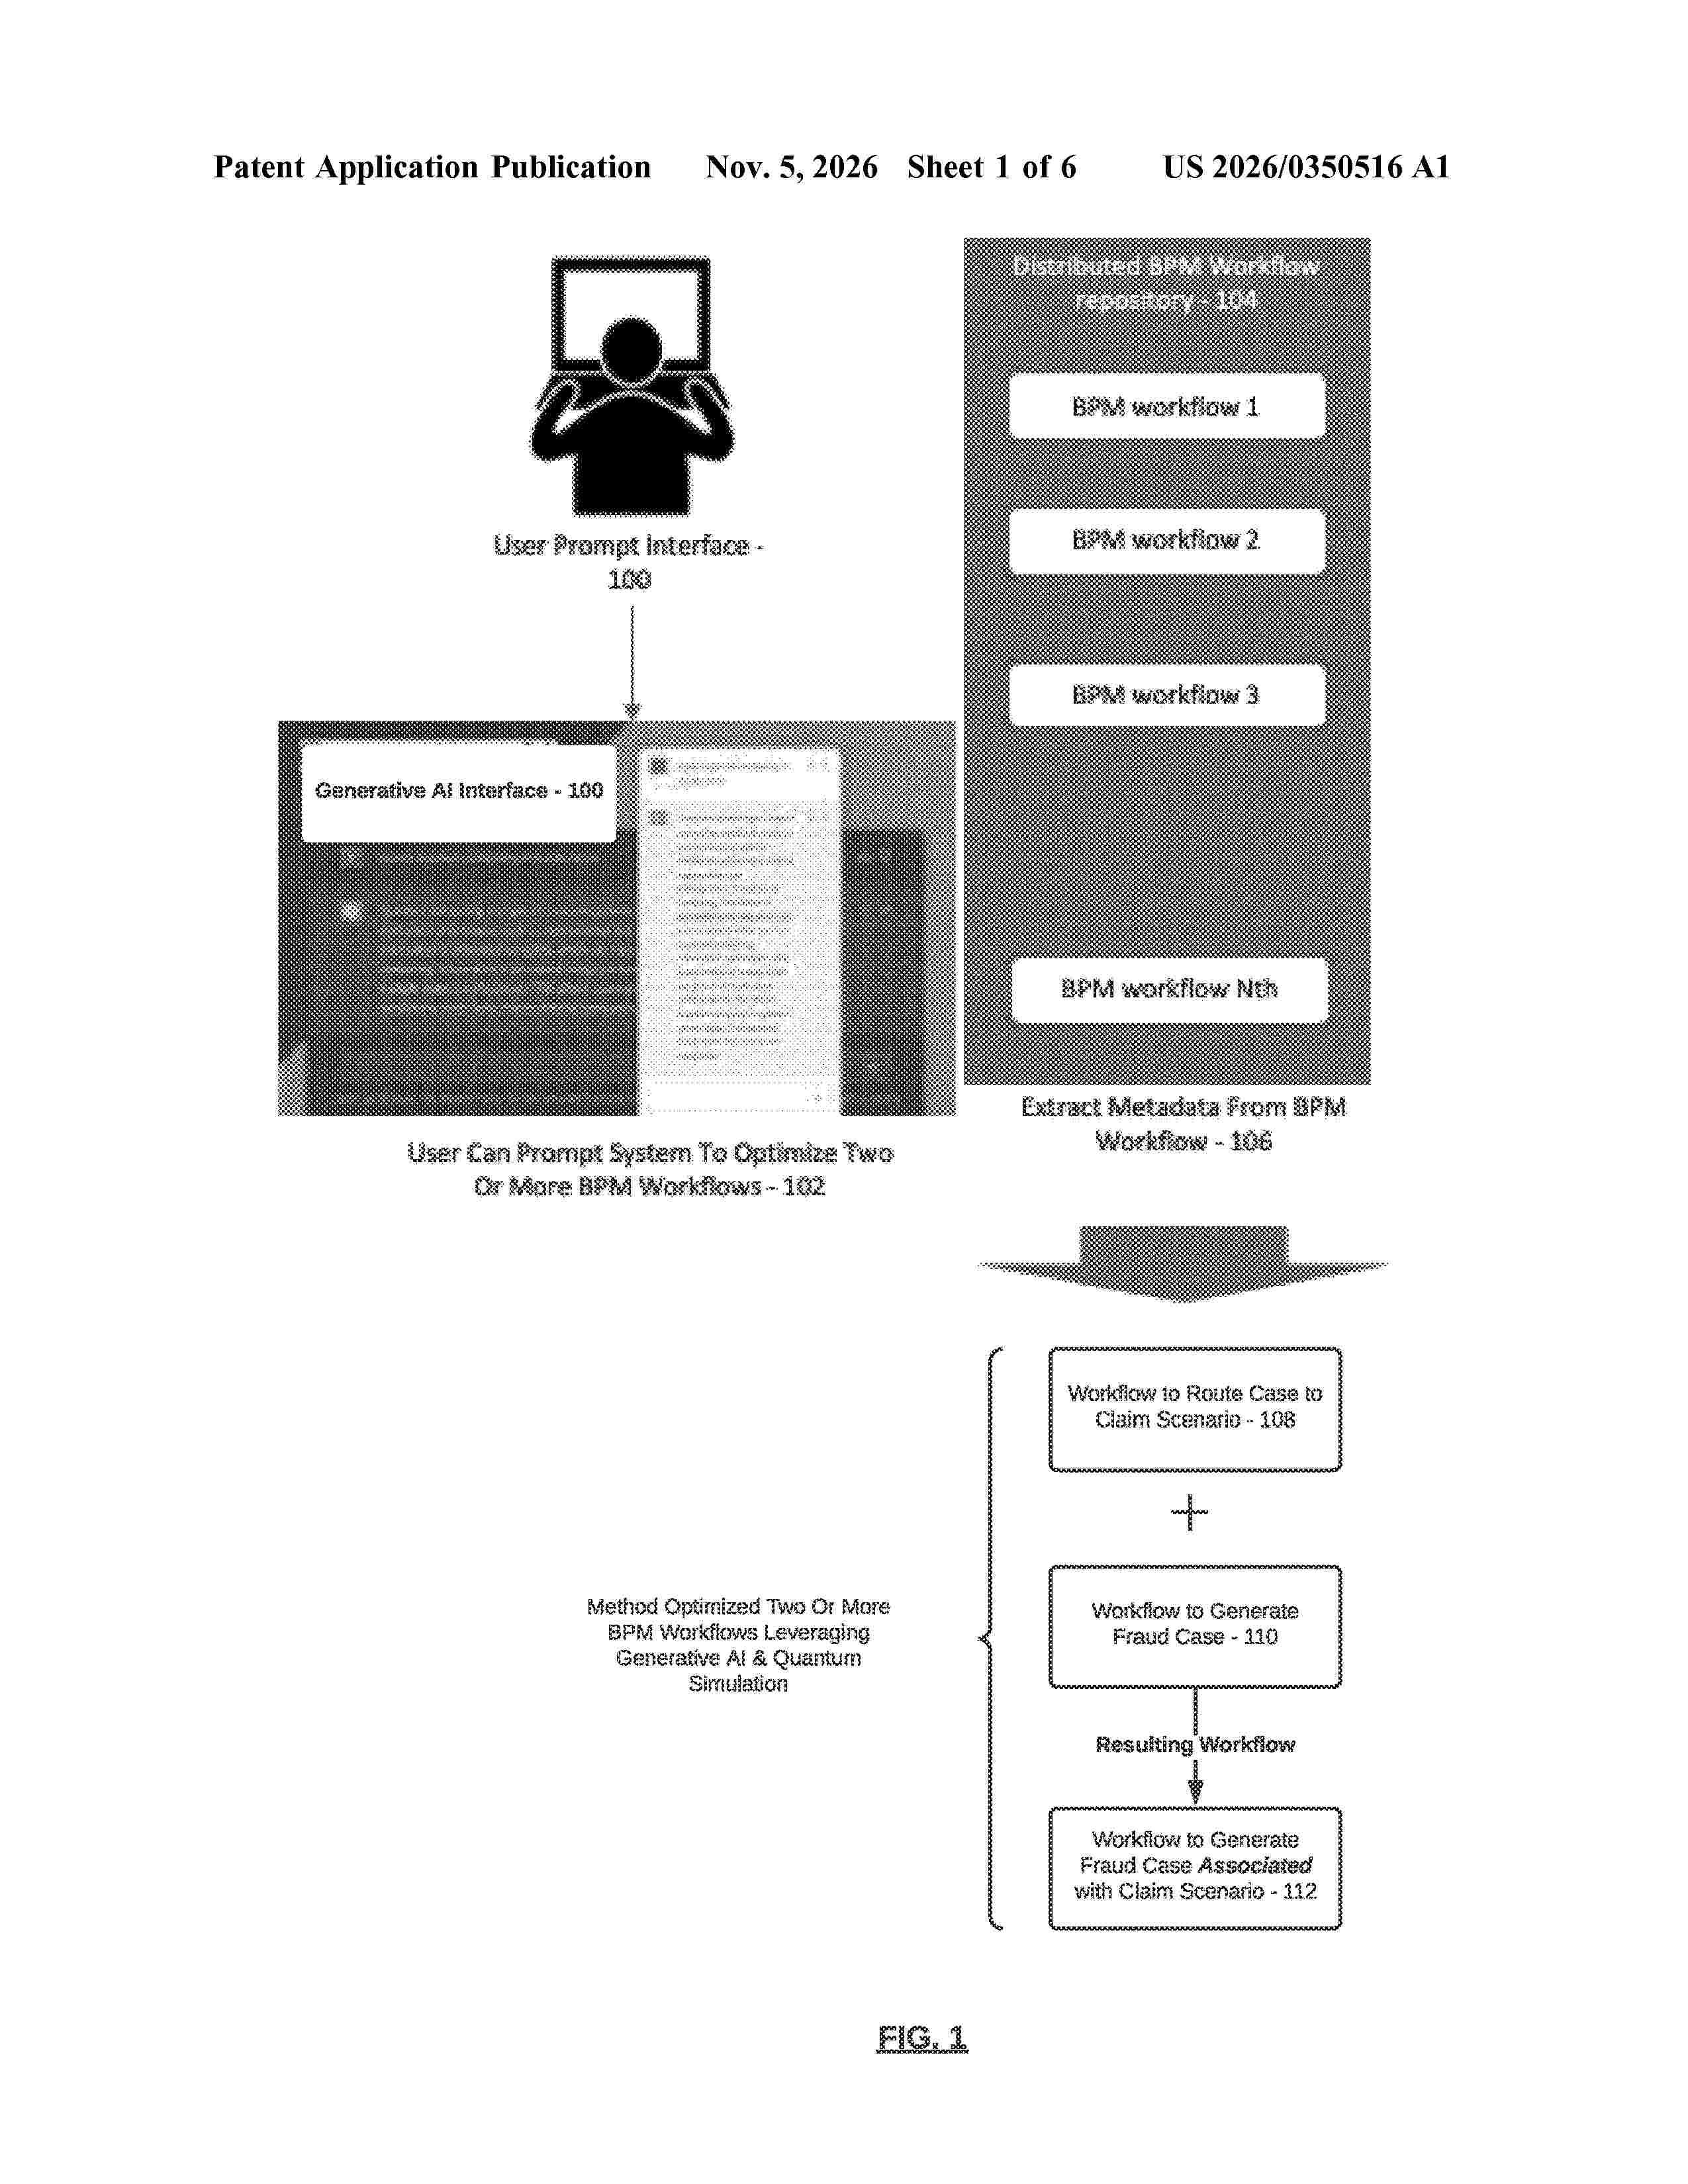
Resumen de: US20260350516A1
Artificial intelligence systems and processing are provided. A generative artificial intelligence model generates workflow templates from a natural language input and from workflow code metadata extracted by an Abstract Syntax Tree. A quantum computing processor performs, in parallel, a quantum simulation of the workflow templates, and a long short-term memory neural network assigns a performance-complexity score to each workflow template based on activity, control flow, dataflow, and resource complexity. The workflow templates are clustered by score, an optimized workflow is selected, and the optimized workflow is deployed to a blockchain network using a smart contract that gates deployment on consent from interconnected applications. The architecture accelerates evaluation of large numbers of workflow combinations and secures deployment, improving the operation of distributed workflow-deployment computing systems.

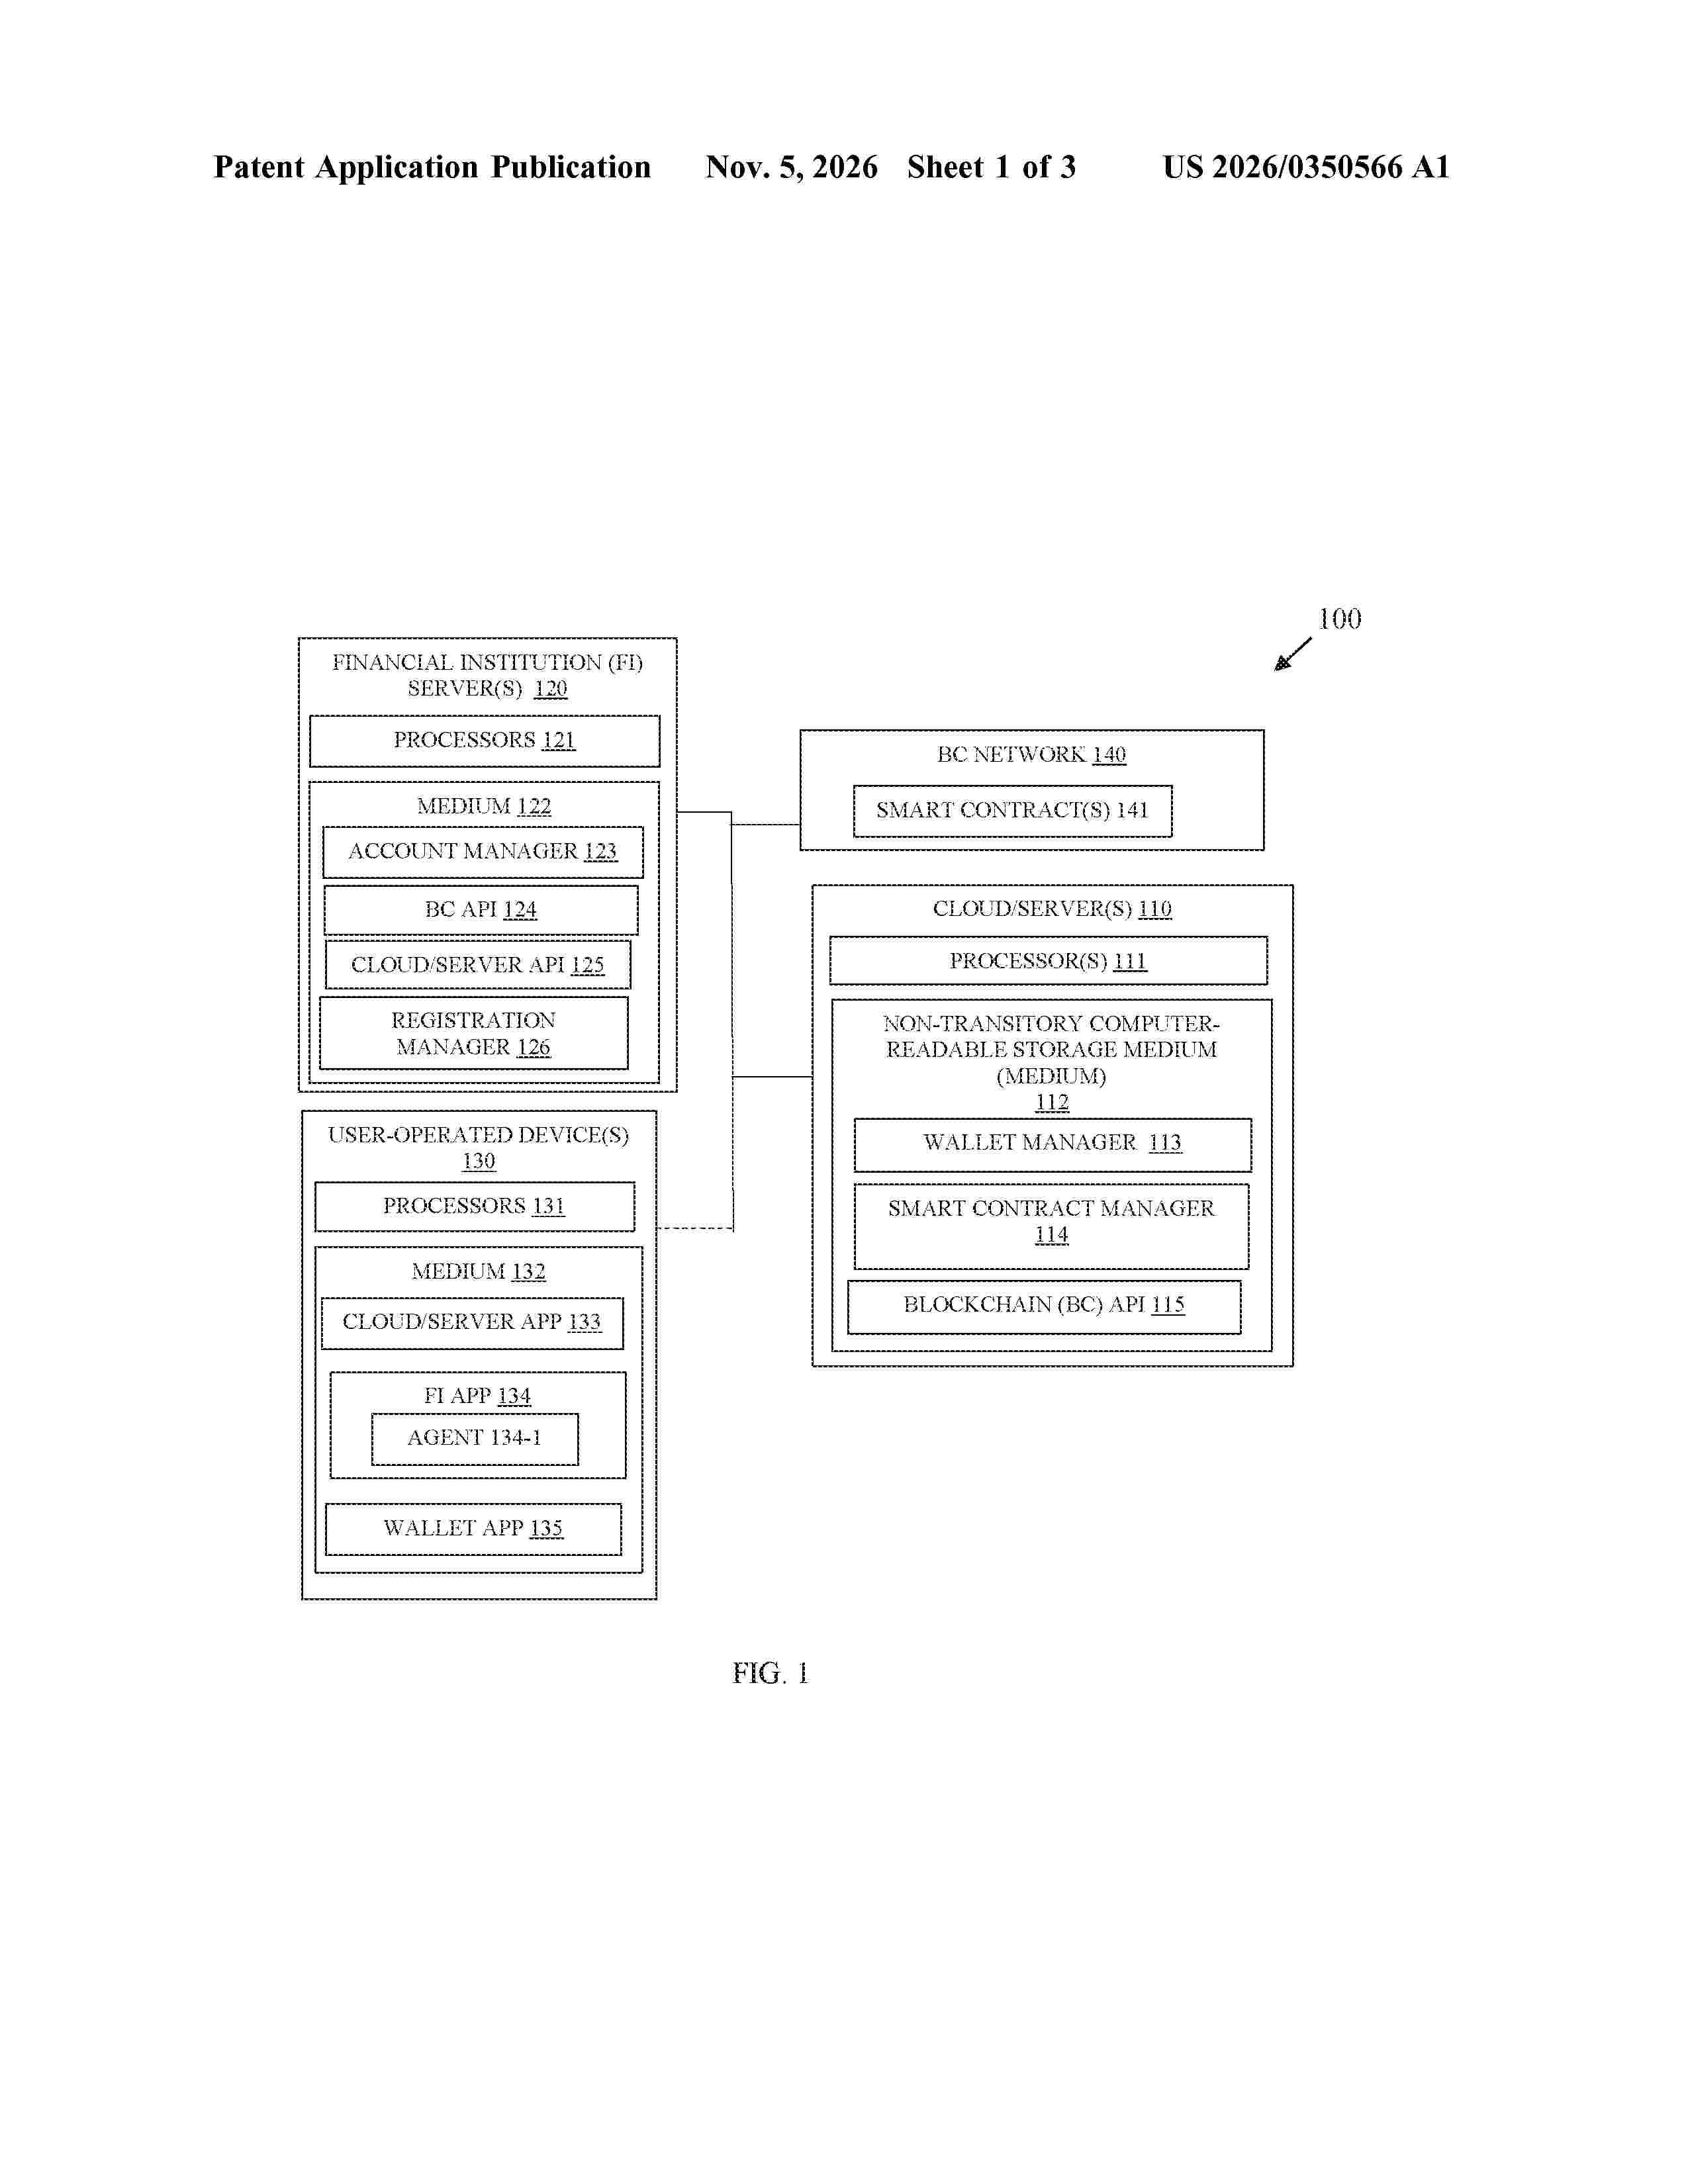
Resumen de: US20260350566A1
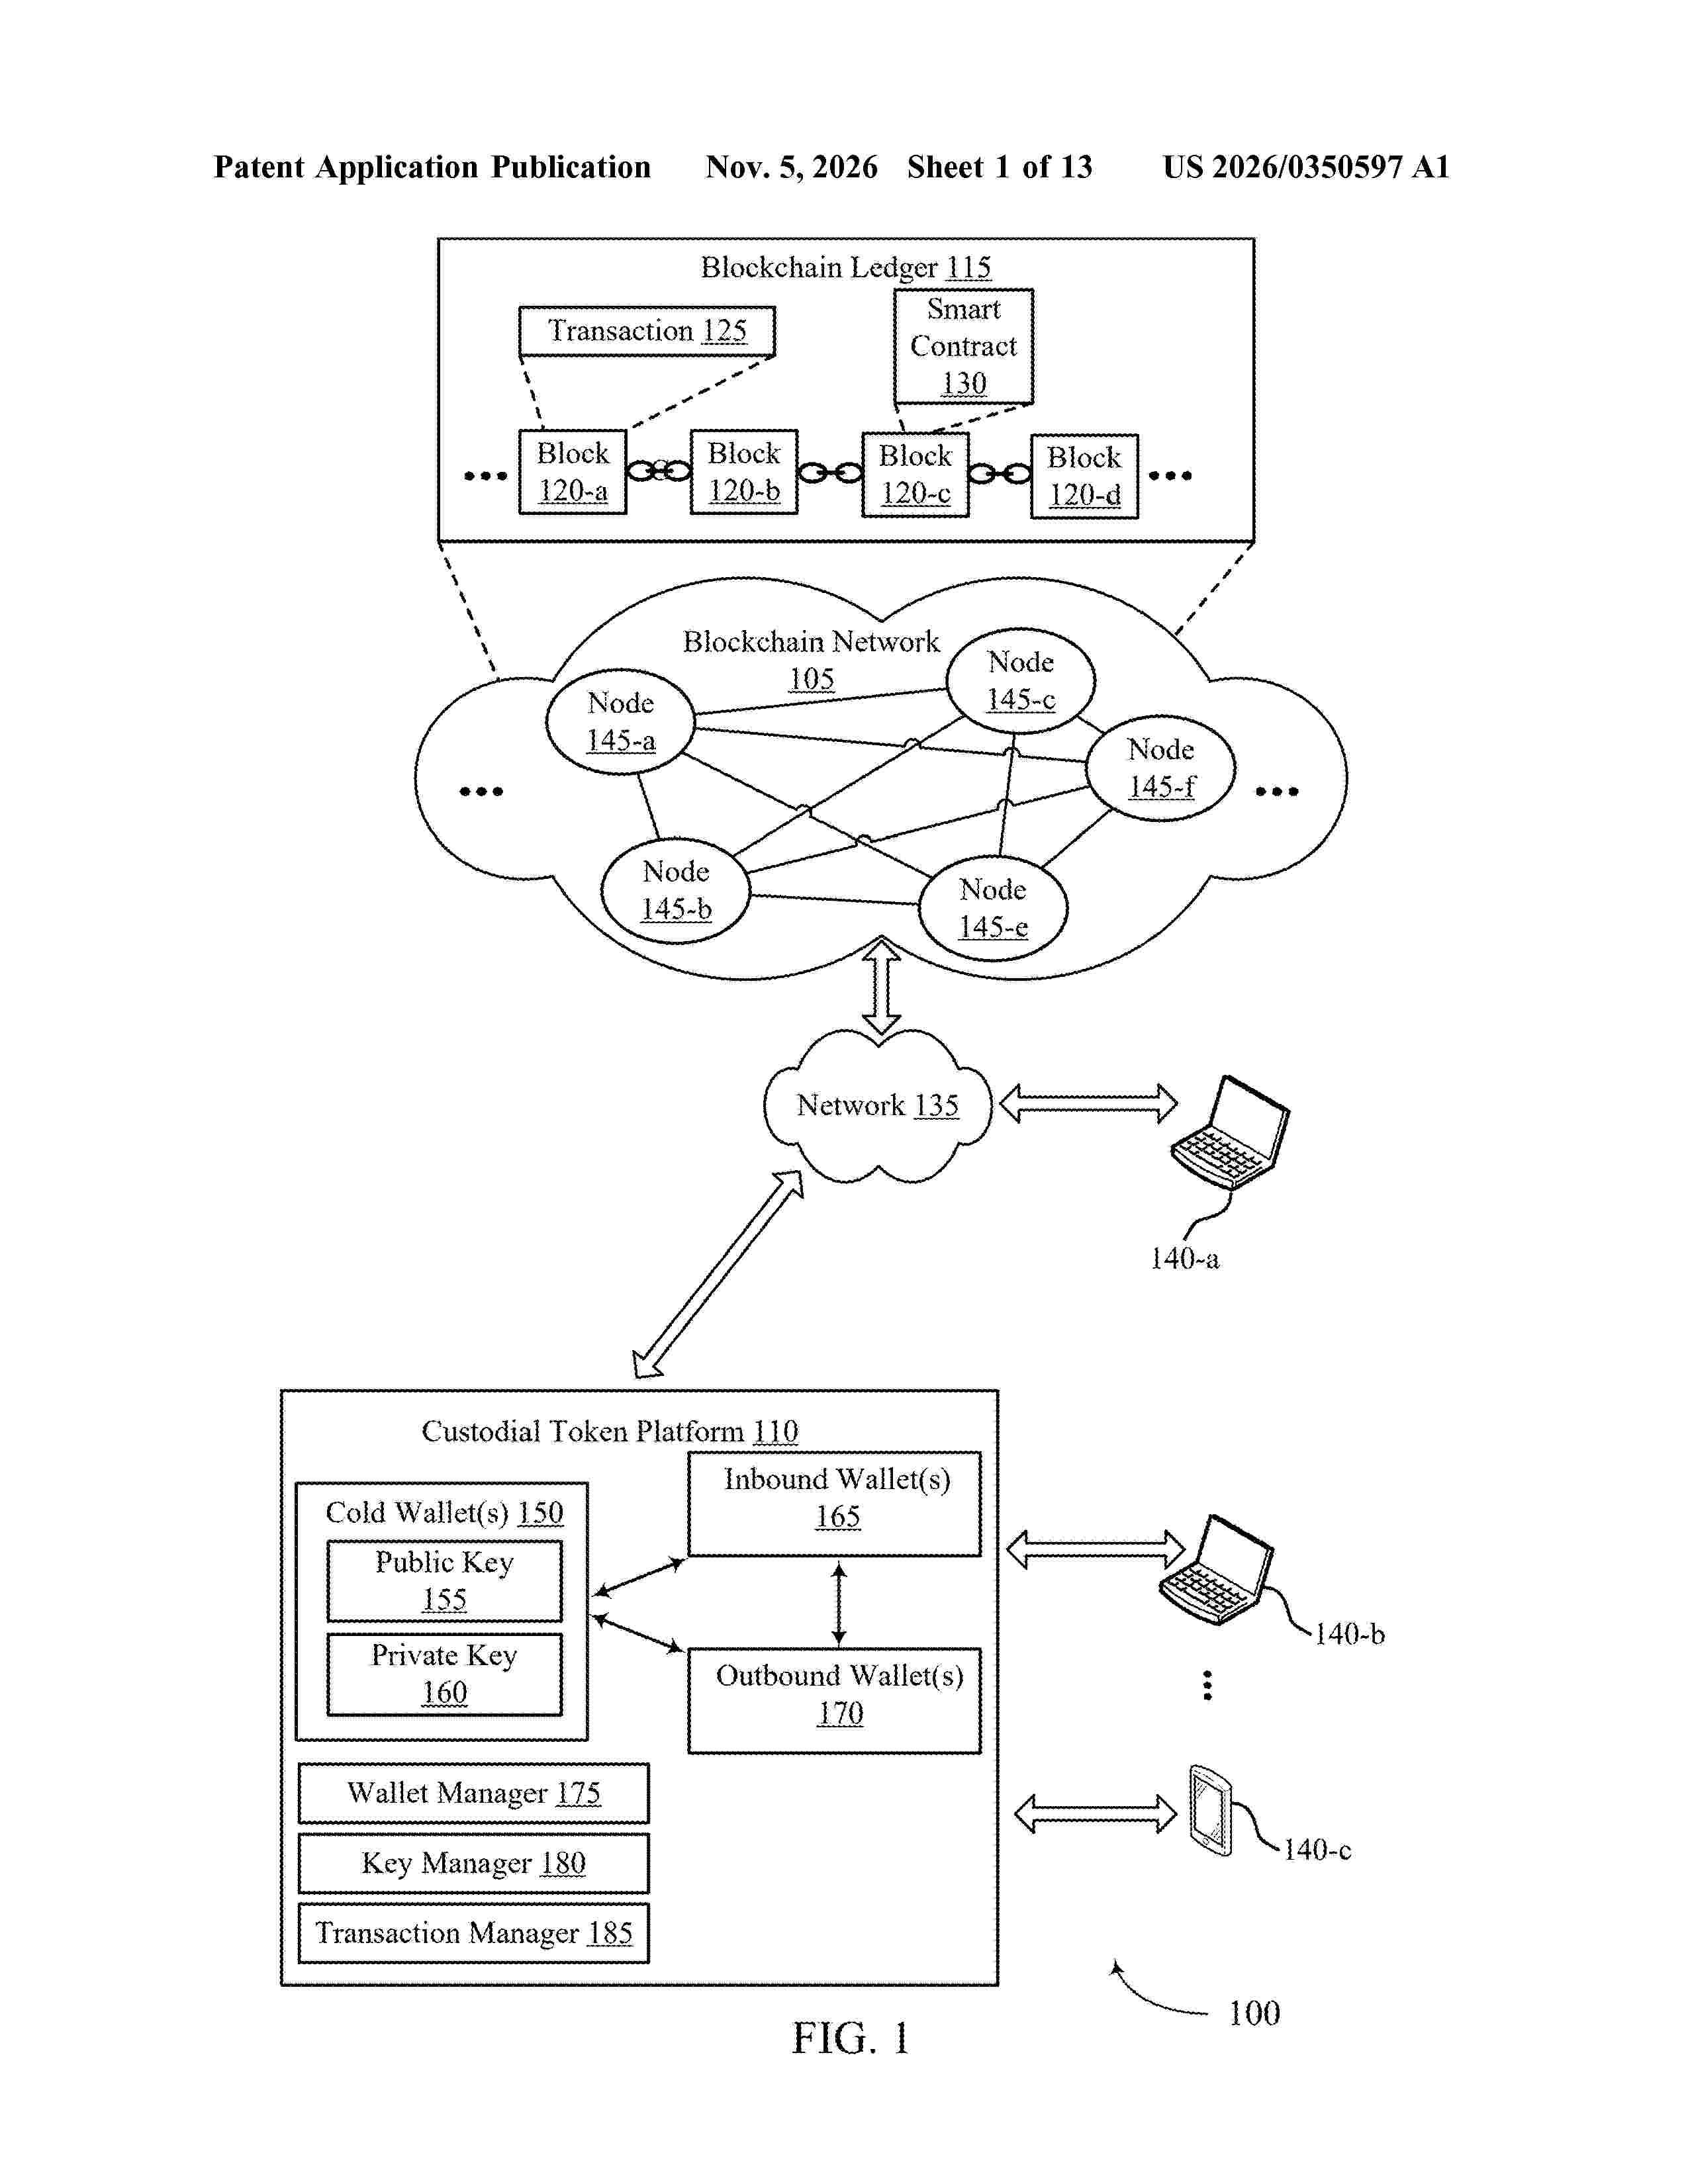
0000 Financial Institution (FI) applications (apps) are enhanced to permit customers to transfer cryptocurrency over a private blockchain (BC) to recipients. The recipients can maintain the amount of cryptocurrency received in their wallets or directly transfer the cryptocurrency in equivalent amounts of fiat currency into their FI accounts. Smart contracts on the private BC ensure that senders and receivers of the value transfers are registered and effectuate the wallet-to-wallet value transfers.
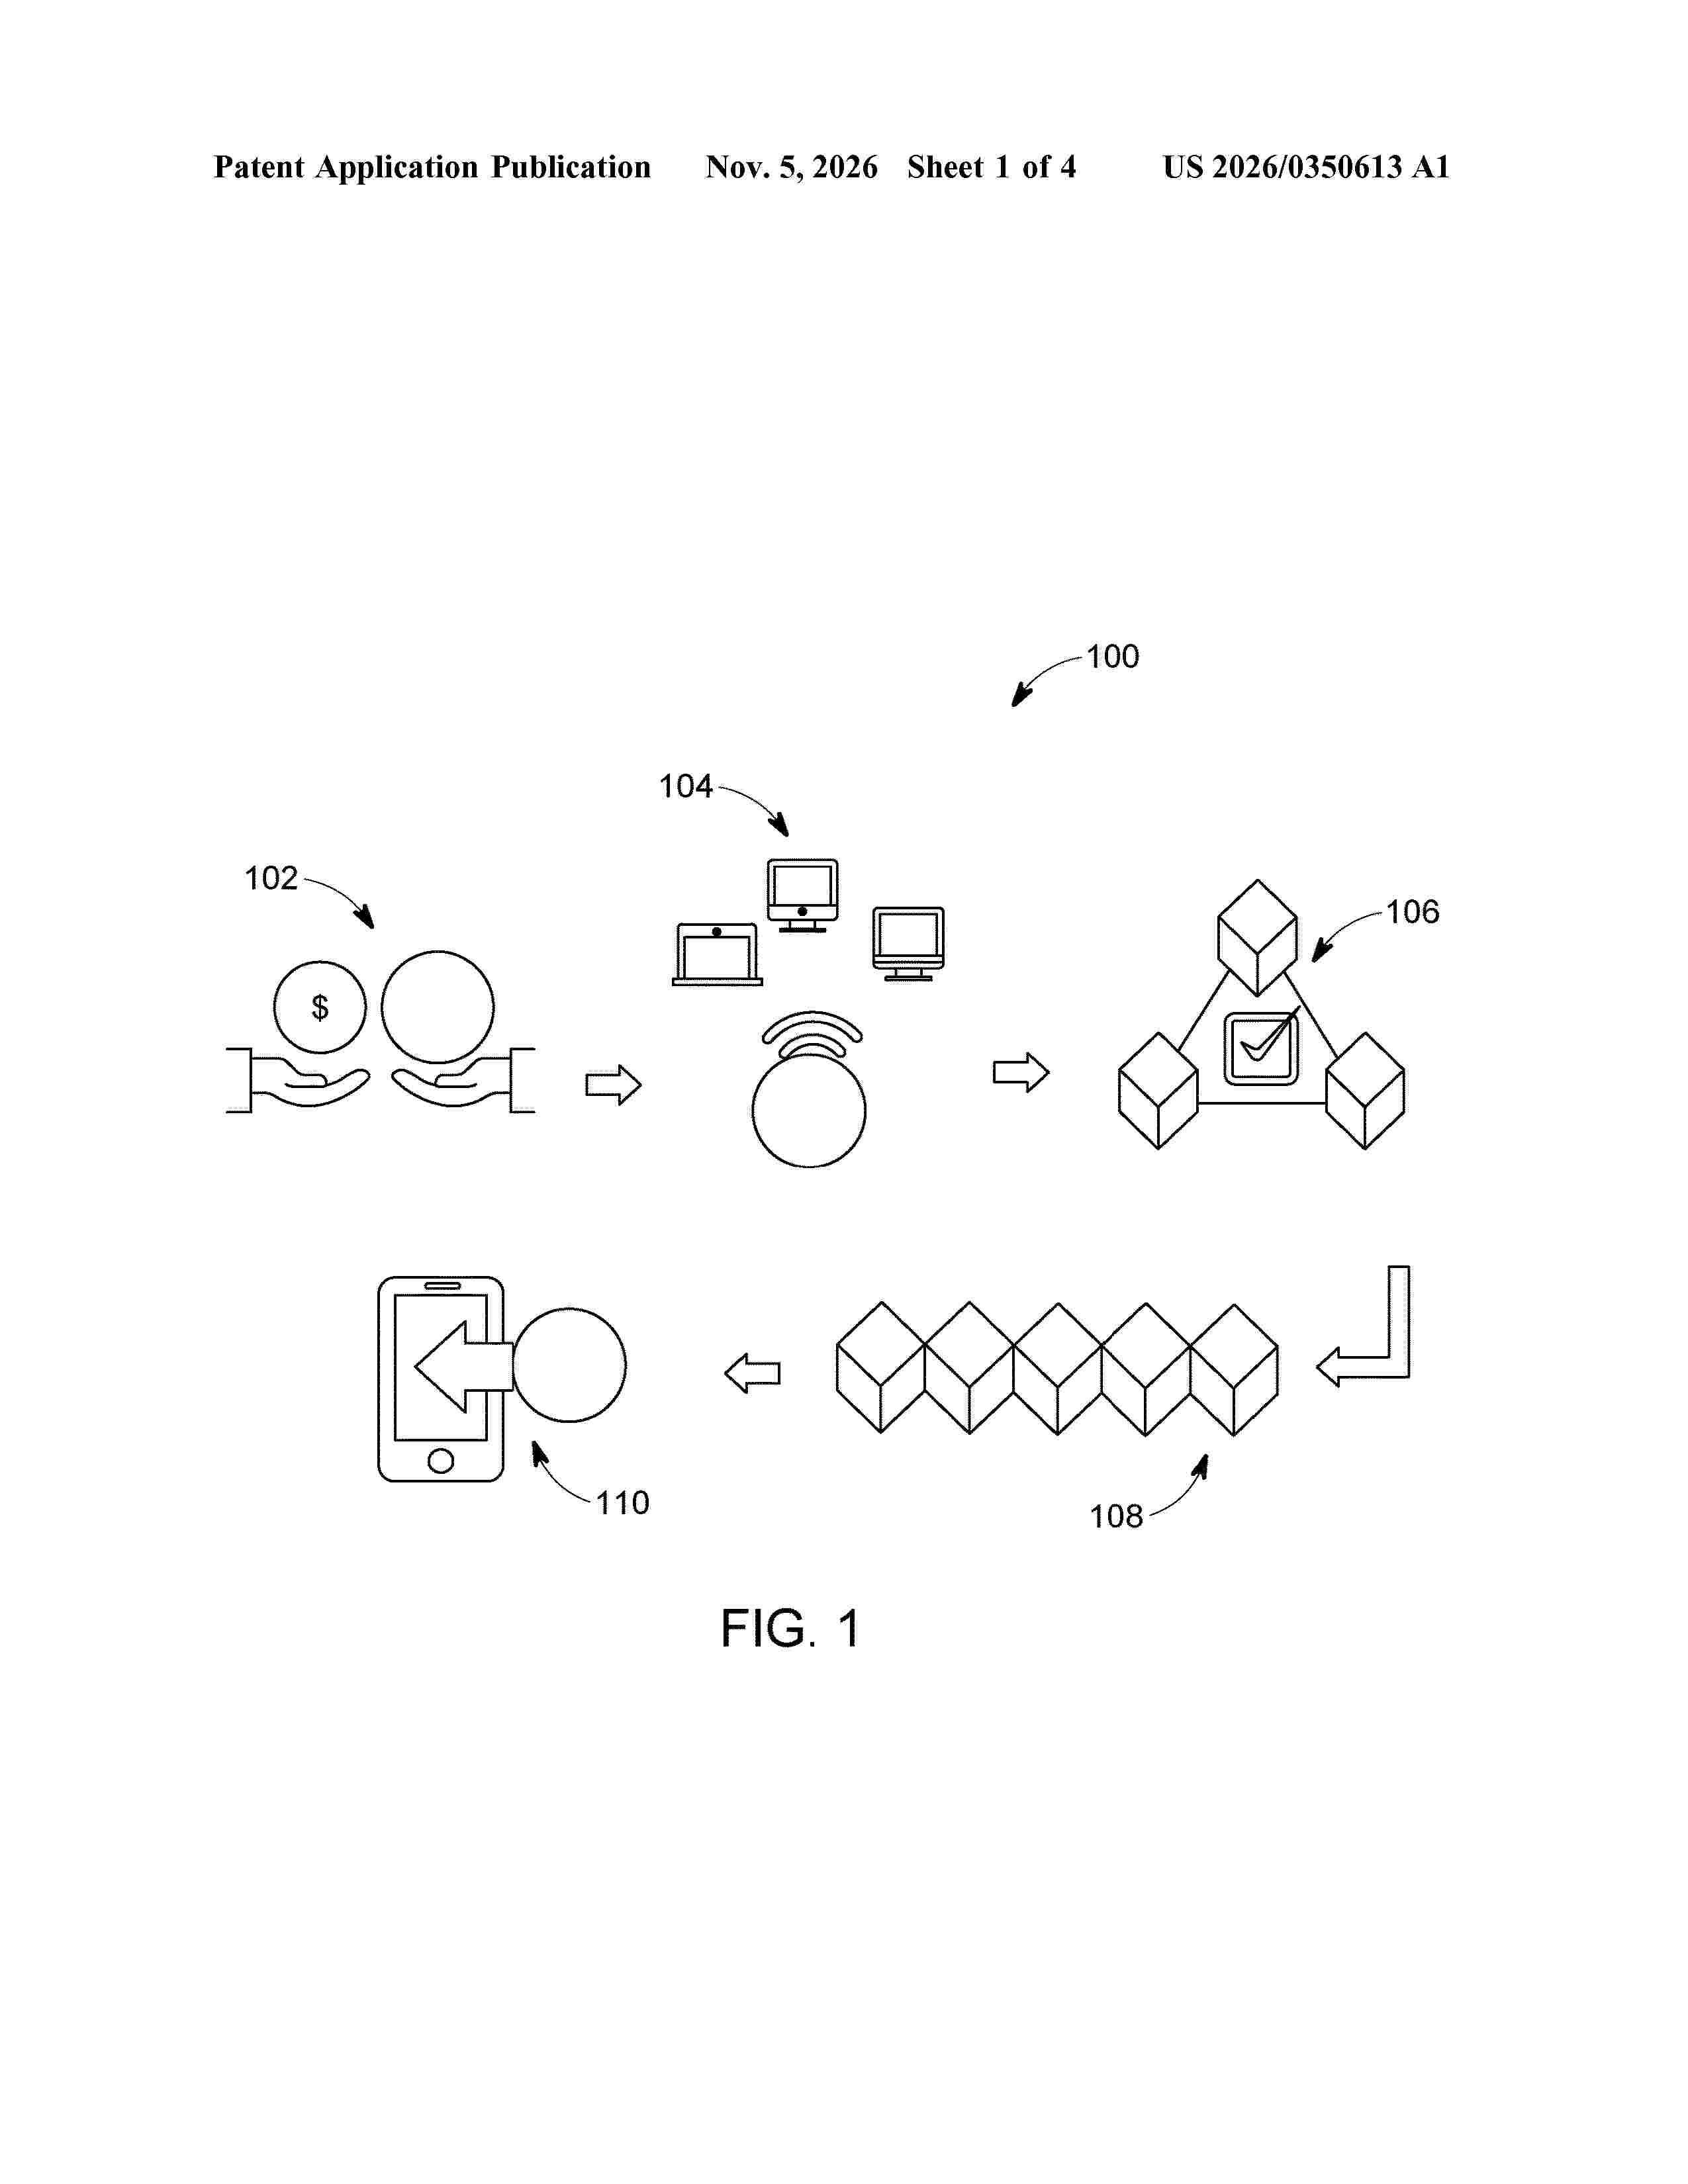
Resumen de: US20260350613A1
A system and method of transferring digital assets is disclosed. The method can comprises effecting a transaction comprising a user authorizing a transfer of a digital asset from a consumer wallet to an account, updating the blockchain ledger of the first digital asset to reflect the transfer, and characterizing the digital asset as compliant or non-compliant based on evaluating the digital asset for suspicious blocks in the blockchain ledger. Compliant digital assets can be exchanged for fiat currency and deposited in the target account. Non-compliant digital assets can be held in a managed wallet of a custody provider.
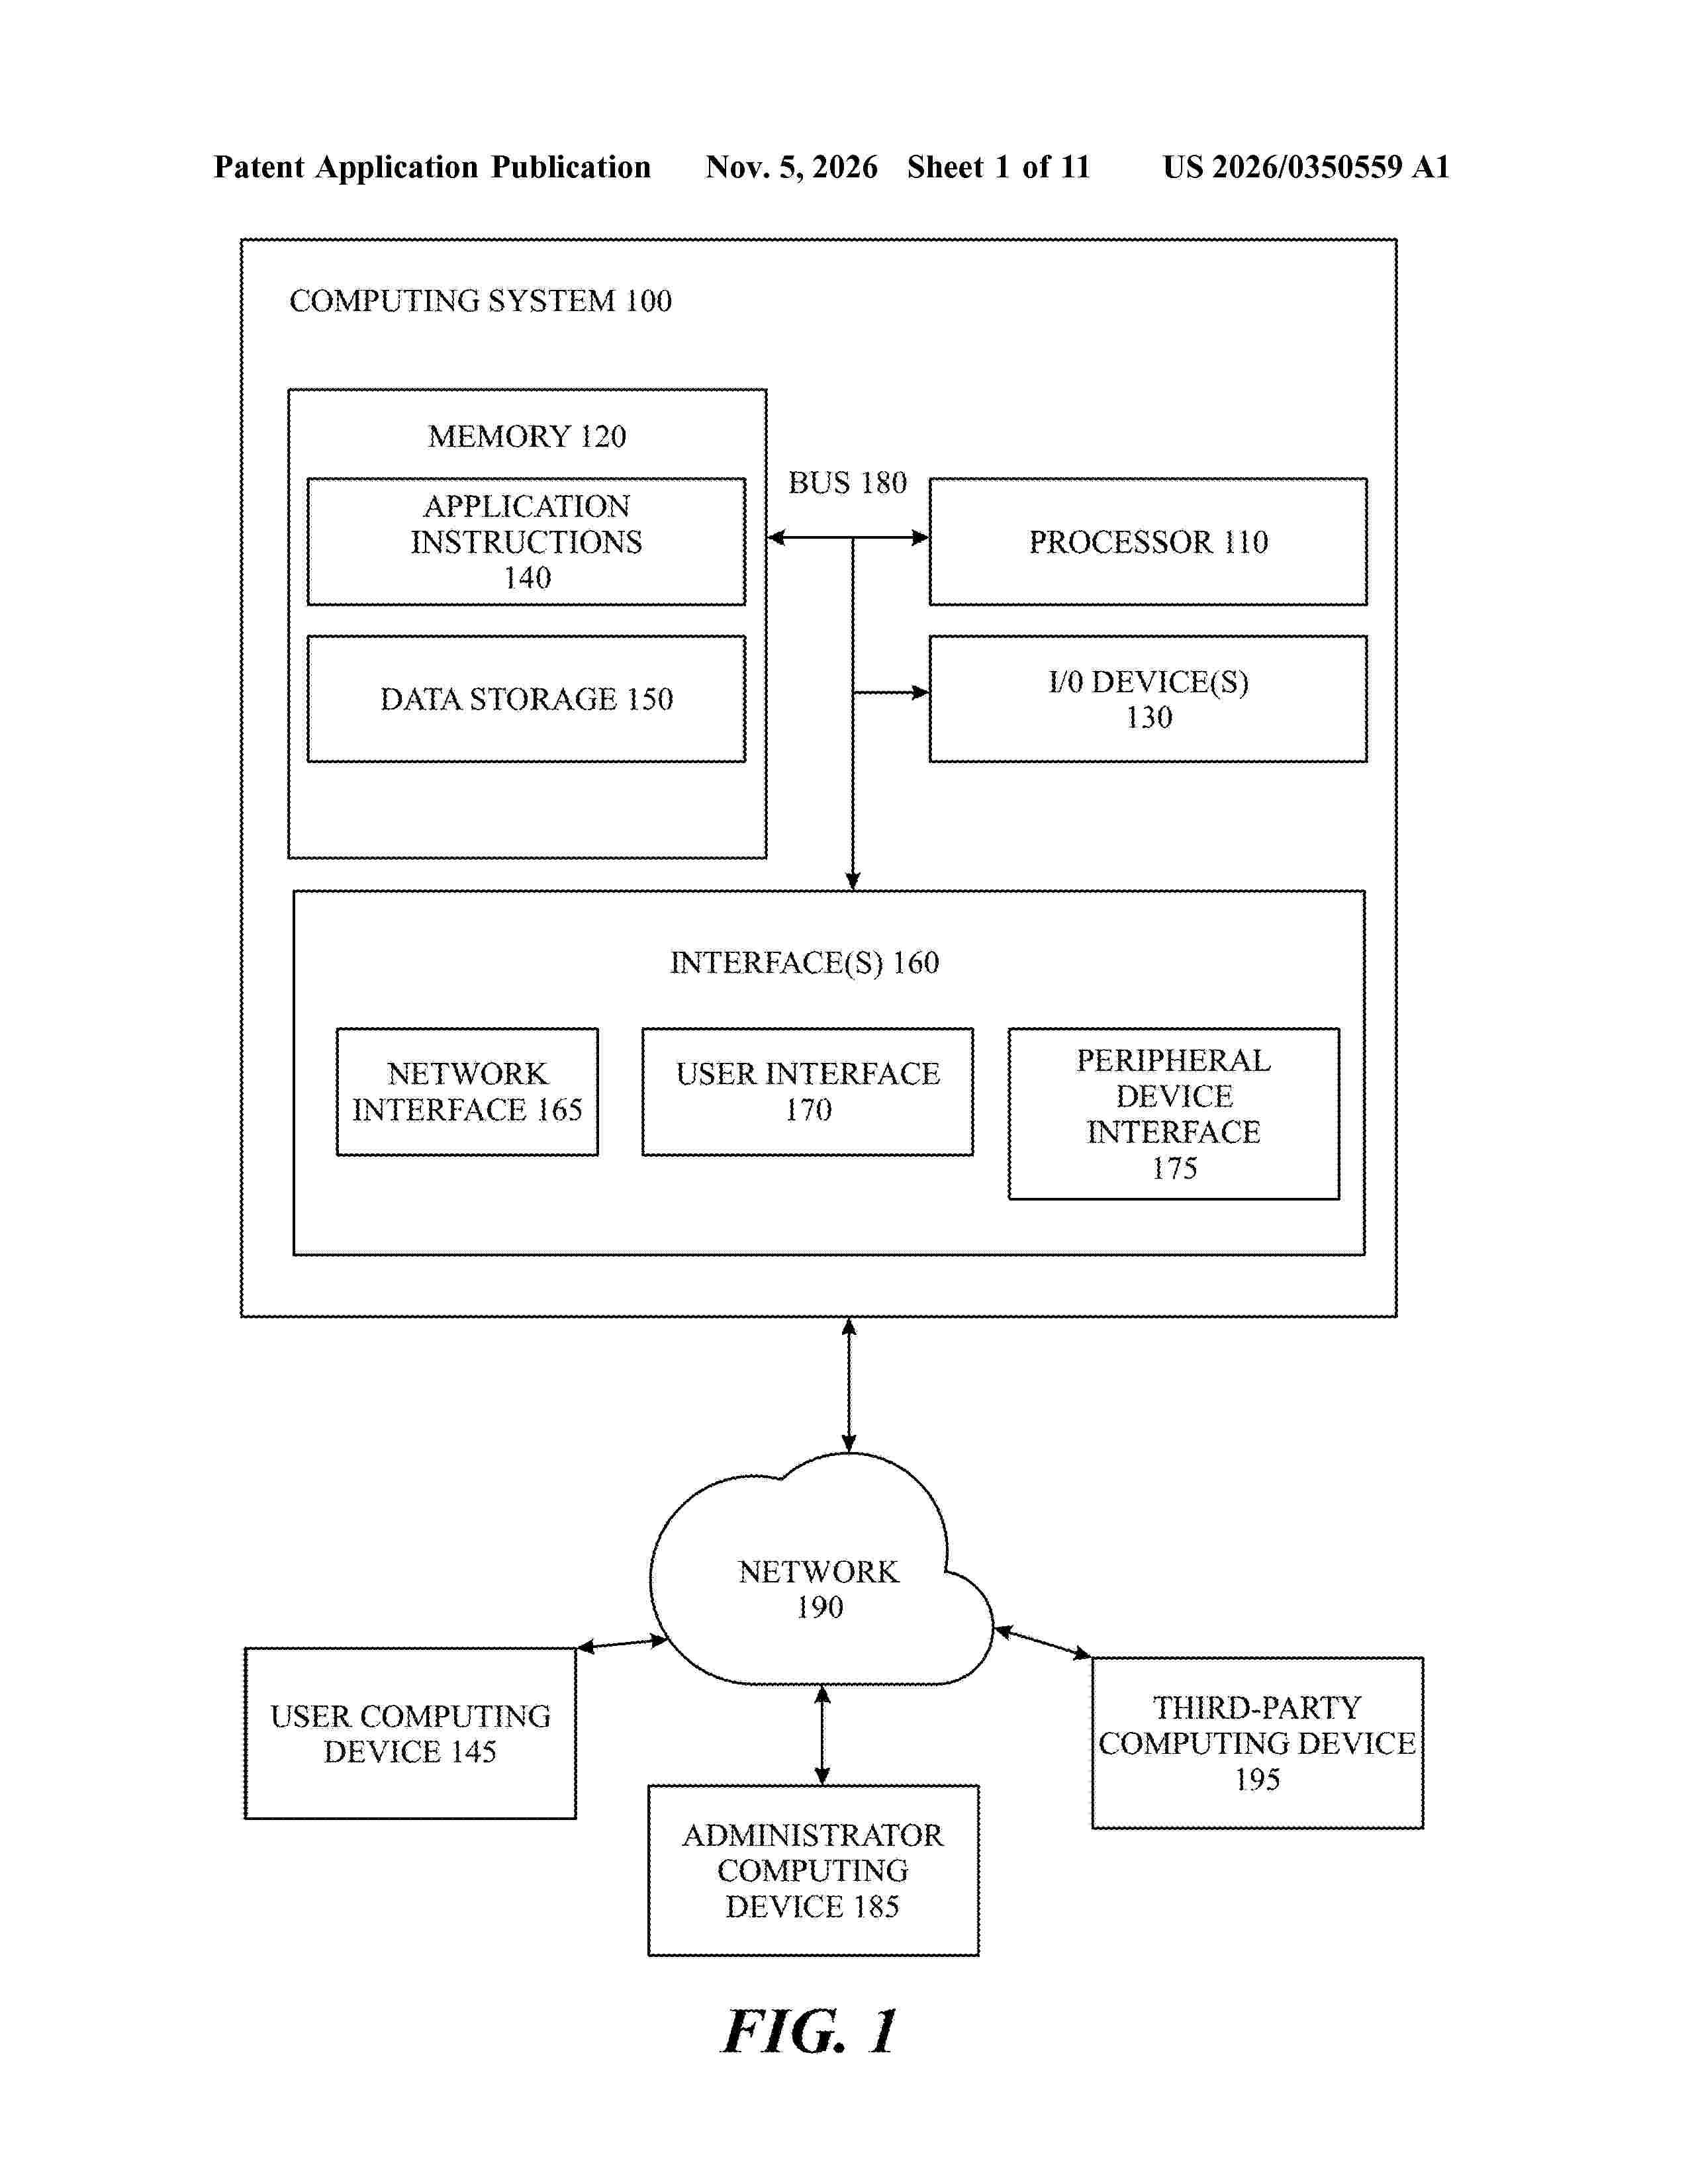
Resumen de: US20260350559A1
0000 A computer-implemented method for managing decentralized business funding may include receiving, via a decentralized application (dApp), a funding proposal from a business entity, the funding proposal including a requested funding amount, funding terms, and intended use of funds; verifying, using a smart contract stored on a blockchain network, that the business entity possesses a verified non-fungible token (NFT) identity including on-chain compliance and performance data; publishing the funding proposal to an investor-facing interface, wherein the proposal is accessible to users based on tiered NFT membership levels; receiving investment commitments from one or more investors via the decentralized application; storing each investment commitment immutably on the blockchain network; executing a smart contract to enforce a binding agreement between the business entity and the investors upon reaching a predetermined funding threshold; and distributing, upon fulfillment of proposal milestones, return payments to the investors using a blockchain-native token.
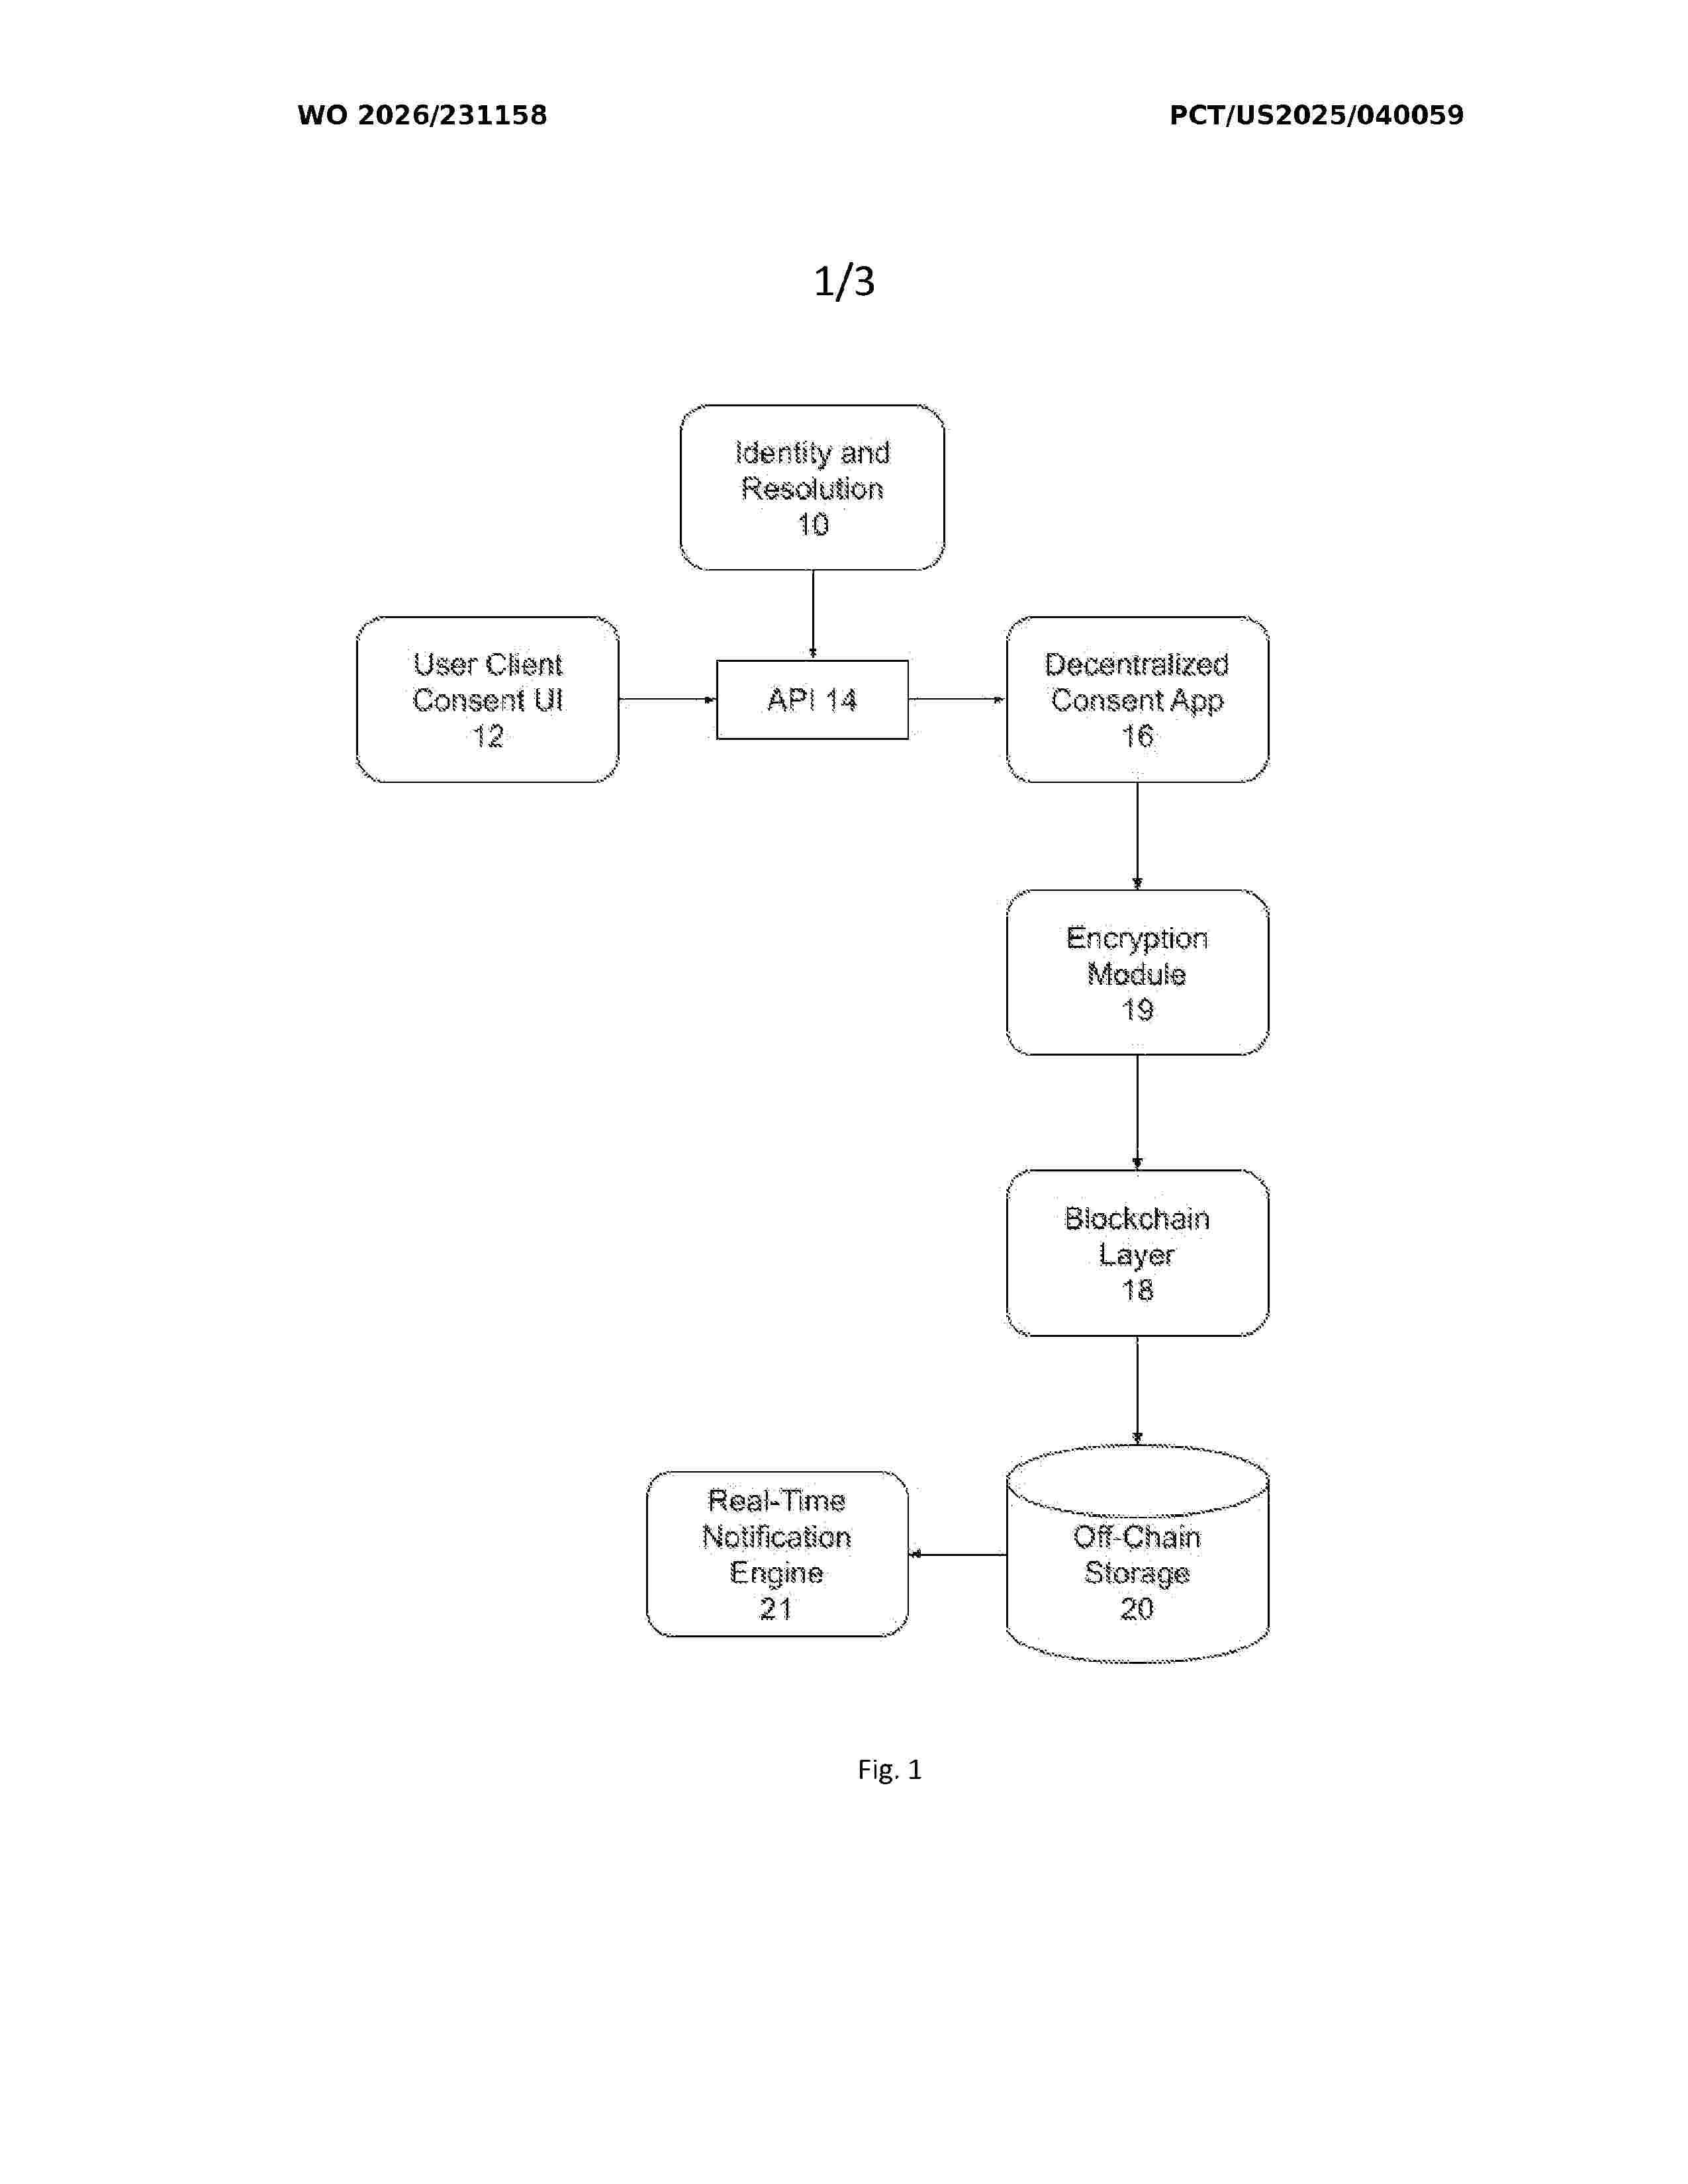
Resumen de: WO2026231158A1
A hybrid blockchain-based system for real-time, privacy-preserving consent management in a distributed node infrastructure creates immutable consent hashes that are stored on-chain for tamper-proof tracking, while encrypted sensitive data is stored off-chain. Smart contracts are used for dynamic consent control and automated enforcement; zero-knowledge proofs (ZKPs) to verify consent status without revealing personal information; decentralized identifiers (DIDs) for decentralized identity authentication; immutable blockchain records to create a tamper-proof, auditable consent history; and real-time propagation of consent changes across data partners. Unlike centralized systems, the invention in certain embodiments uses a distributed ledger to store immutable consent records. The decentralized nature of the ledger ensures that there is no single point of failure for the system, and enhances trust and transparency.
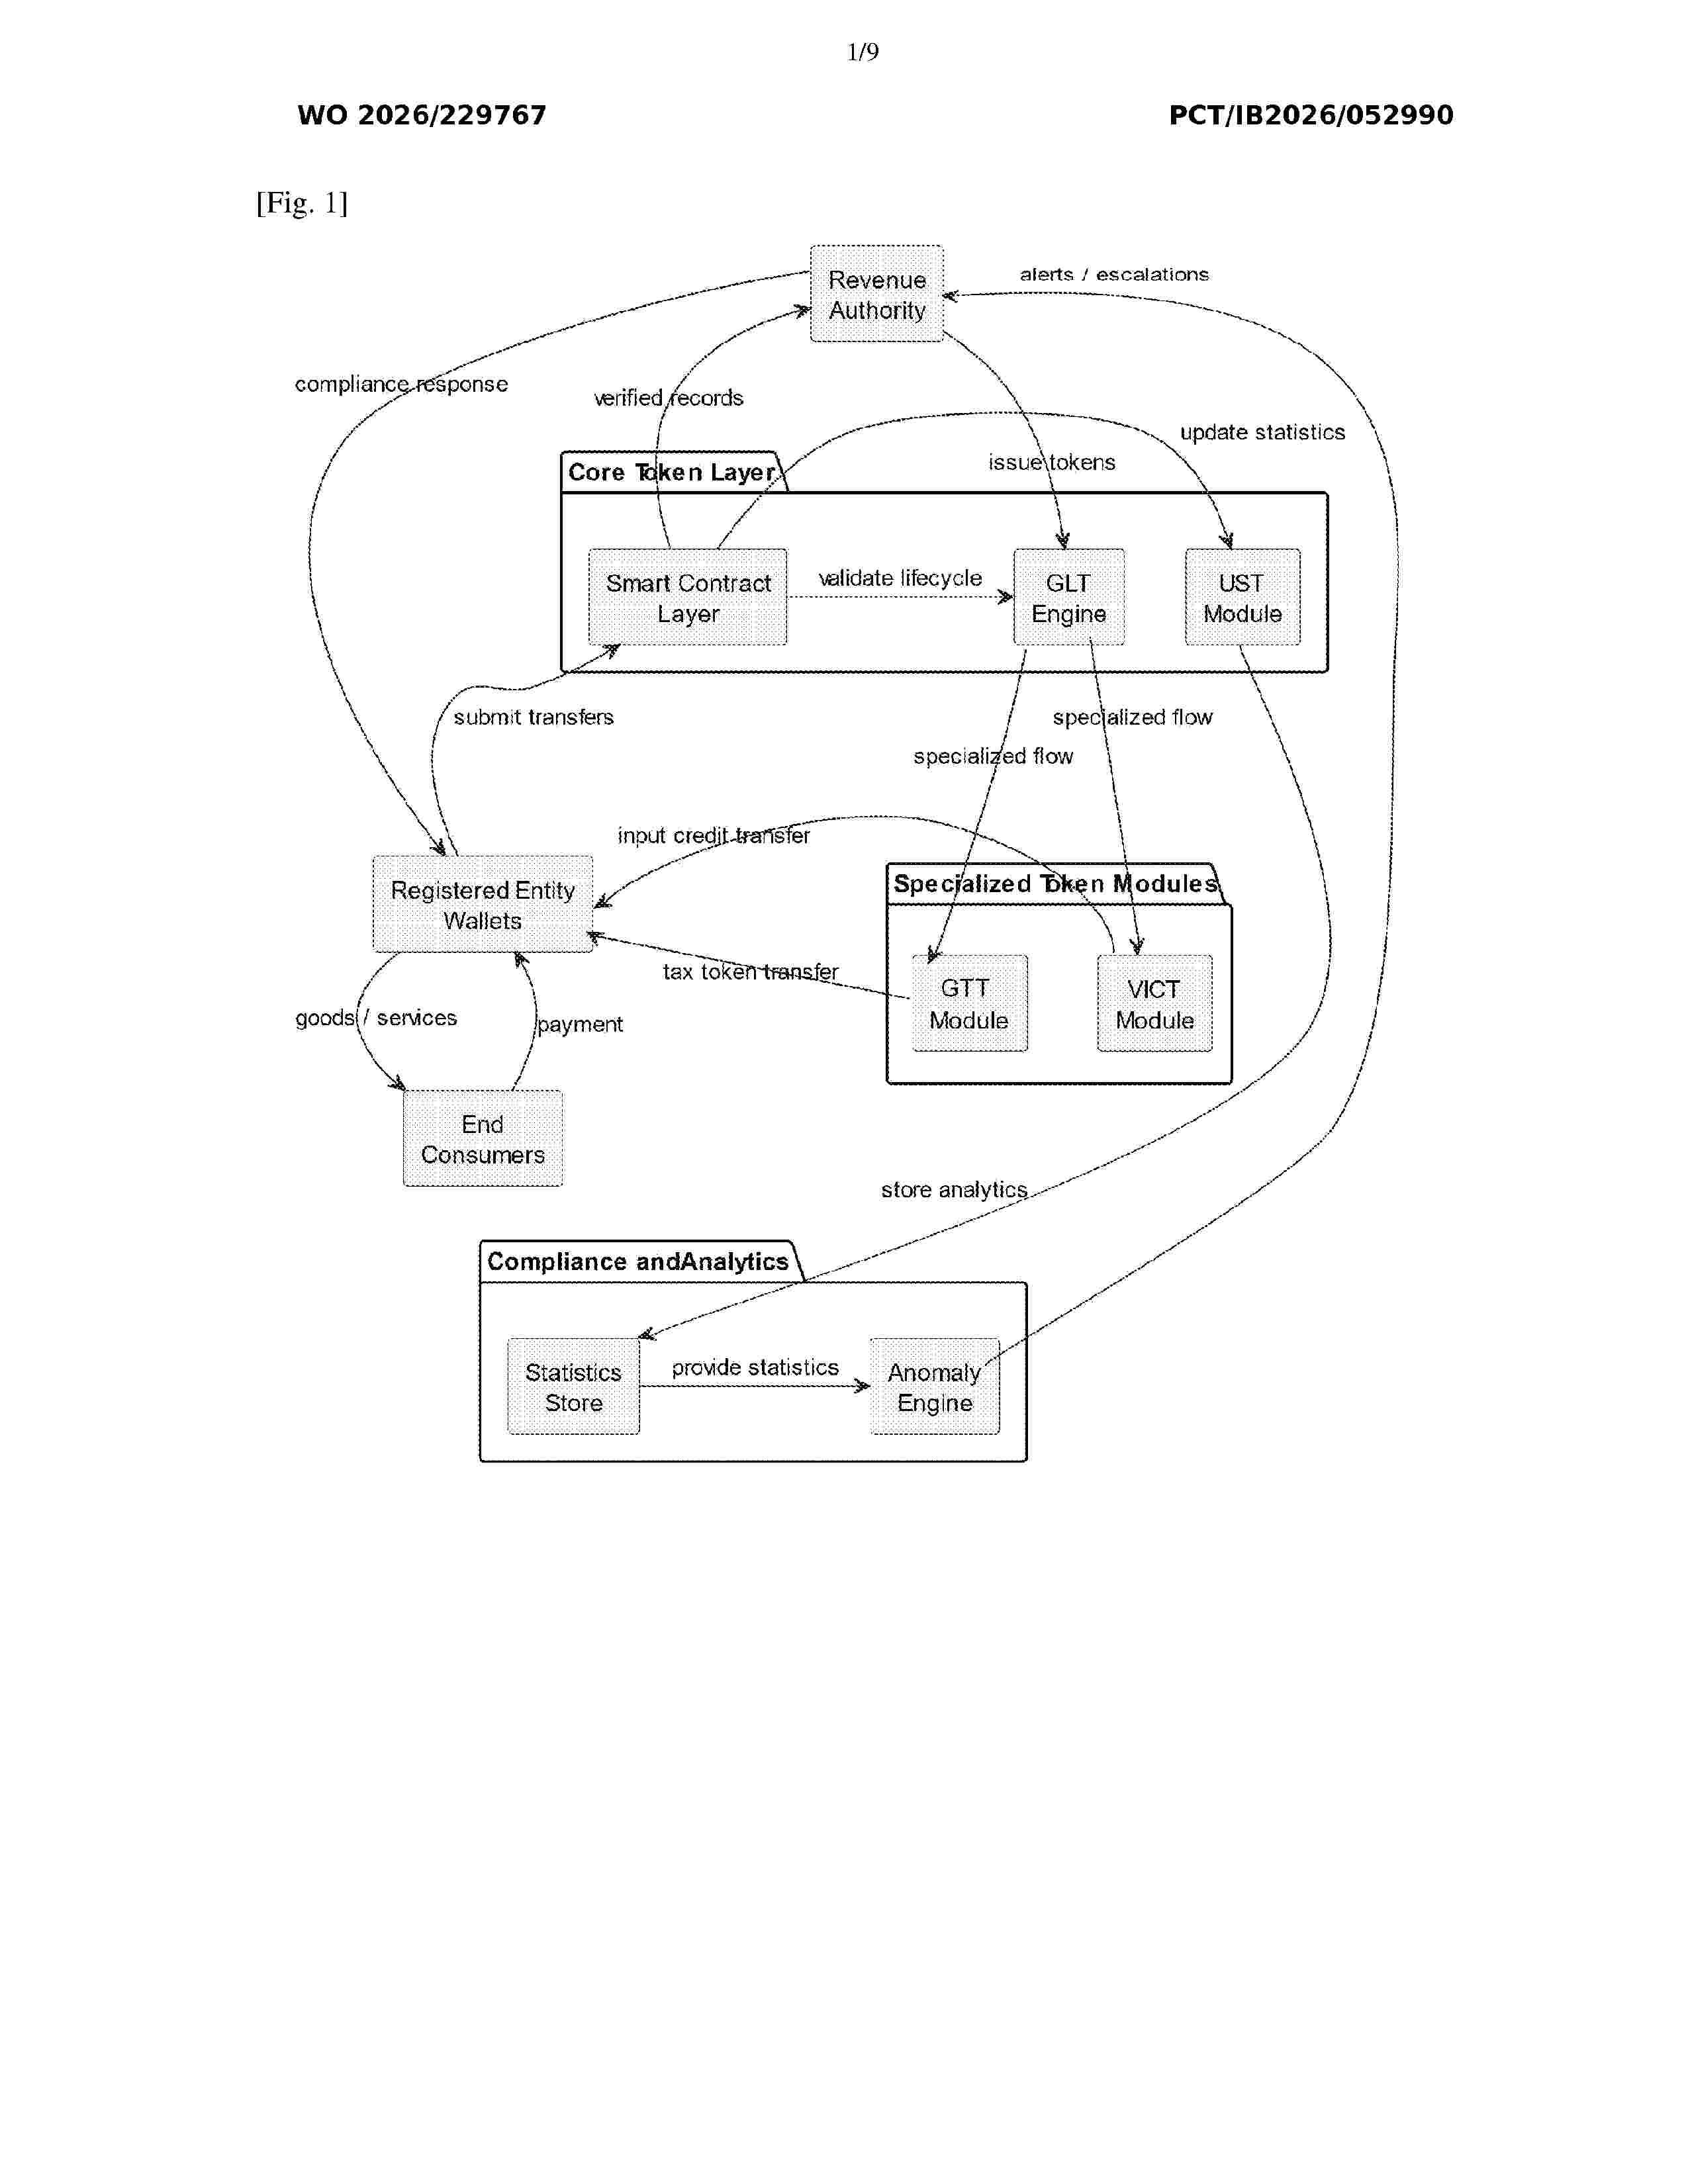
Resumen de: WO2026229767A1
A blockchain-based framework for managing transferable obligations via digitally-encoded negative-value tokens. The system introduces the General Liability Token (GLT), whose balances are mutable, divisible, and aggregable within wallets to settle multiple obligations along upstream/downstream flows. Each wallet also maintains a non-transferable Unspendable Statistical Token (UST) updated per transaction; smart contracts read UST to recalibrate GLT balances and enforce dormancy and recovery (recursive liability tracing). An optional AI layer flags anomalous patterns for escalation. The framework supports implementations including VAT Input Credit Tokens (VICT) and Government Tax Tokens (GTT), enabling tokenized input-credit transfer and consumption-tax flows without reliance on cash refunds or centralized reconciliation. All lifecycle operations (issuance, split/merge, transfer, burning, dormancy, recovery) are executed on a permissioned blockchain, providing auditable, scalable, and fraud-resistant compliance infrastructure applicable beyond taxation to other obligation-management domains.
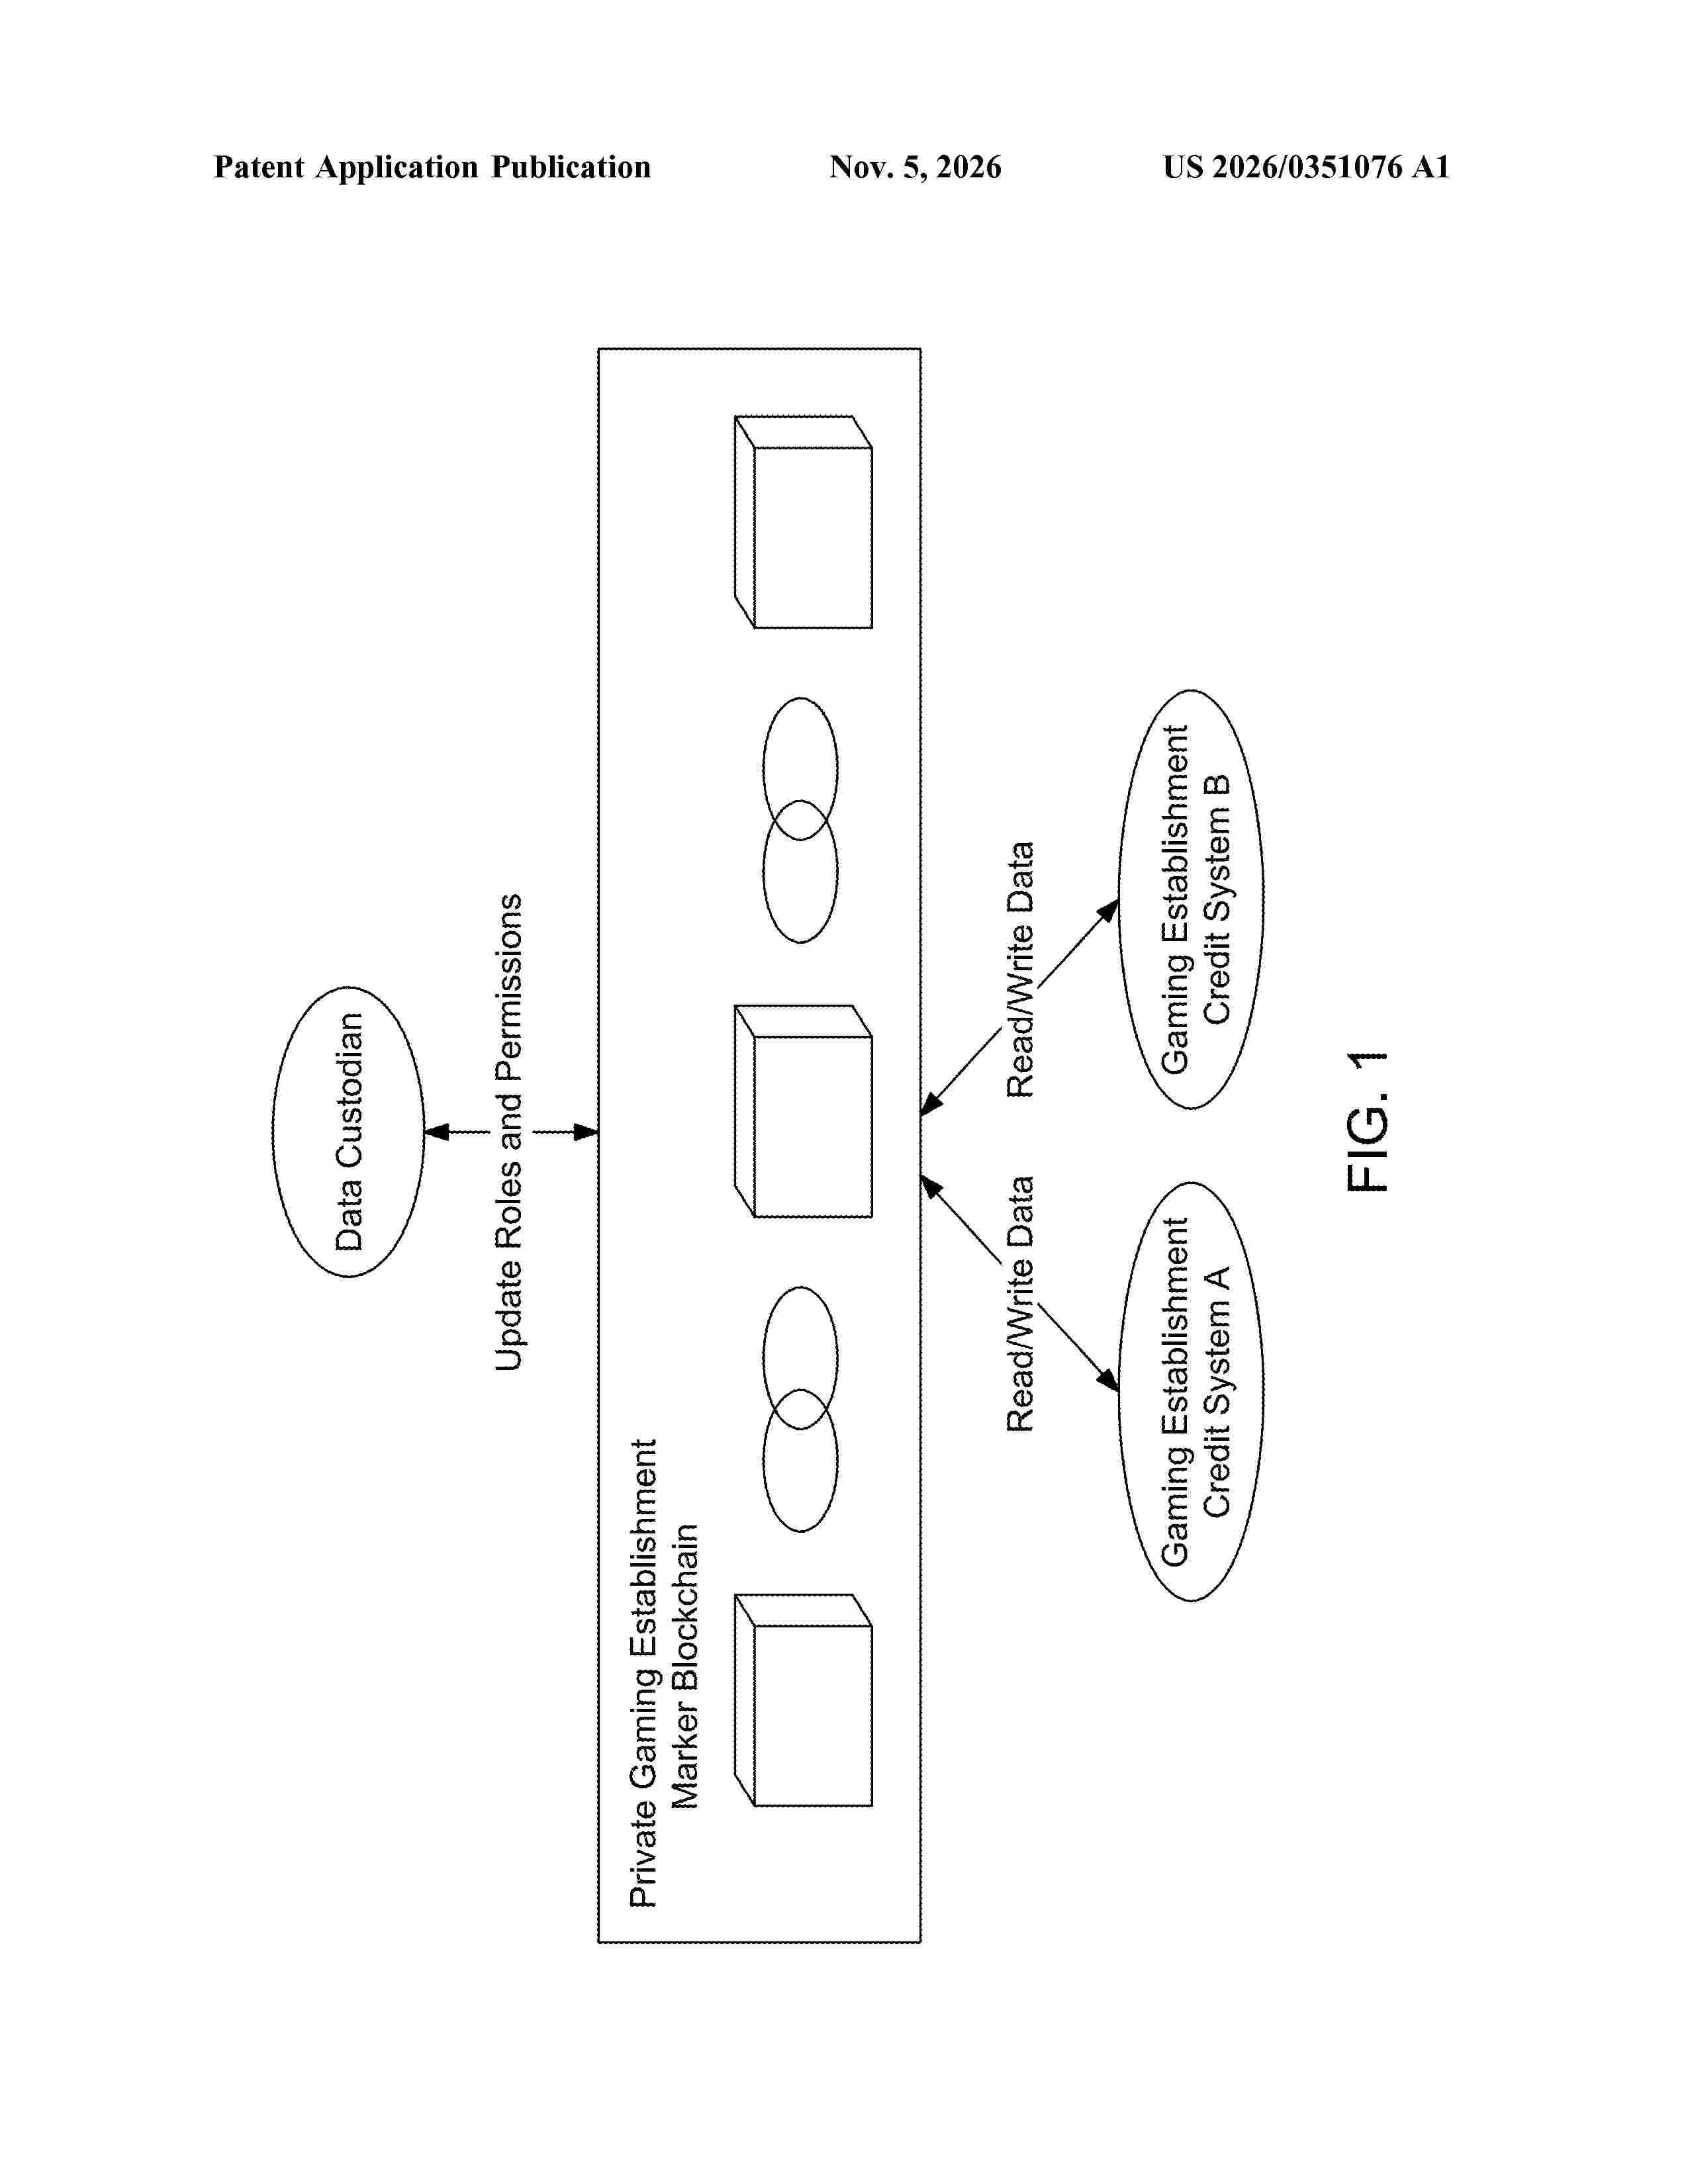
Resumen de: US20260351076A1
Systems and methods that determine if an activity of a user in association with a first gaming establishment qualifies as a potential fraudulent financial transaction. Responsive to the determination being that the activity of the user qualifies as the potential fraudulent financial transaction, the systems and methods cause data associated with the activity to be written in a block of a permissioned blockchain.
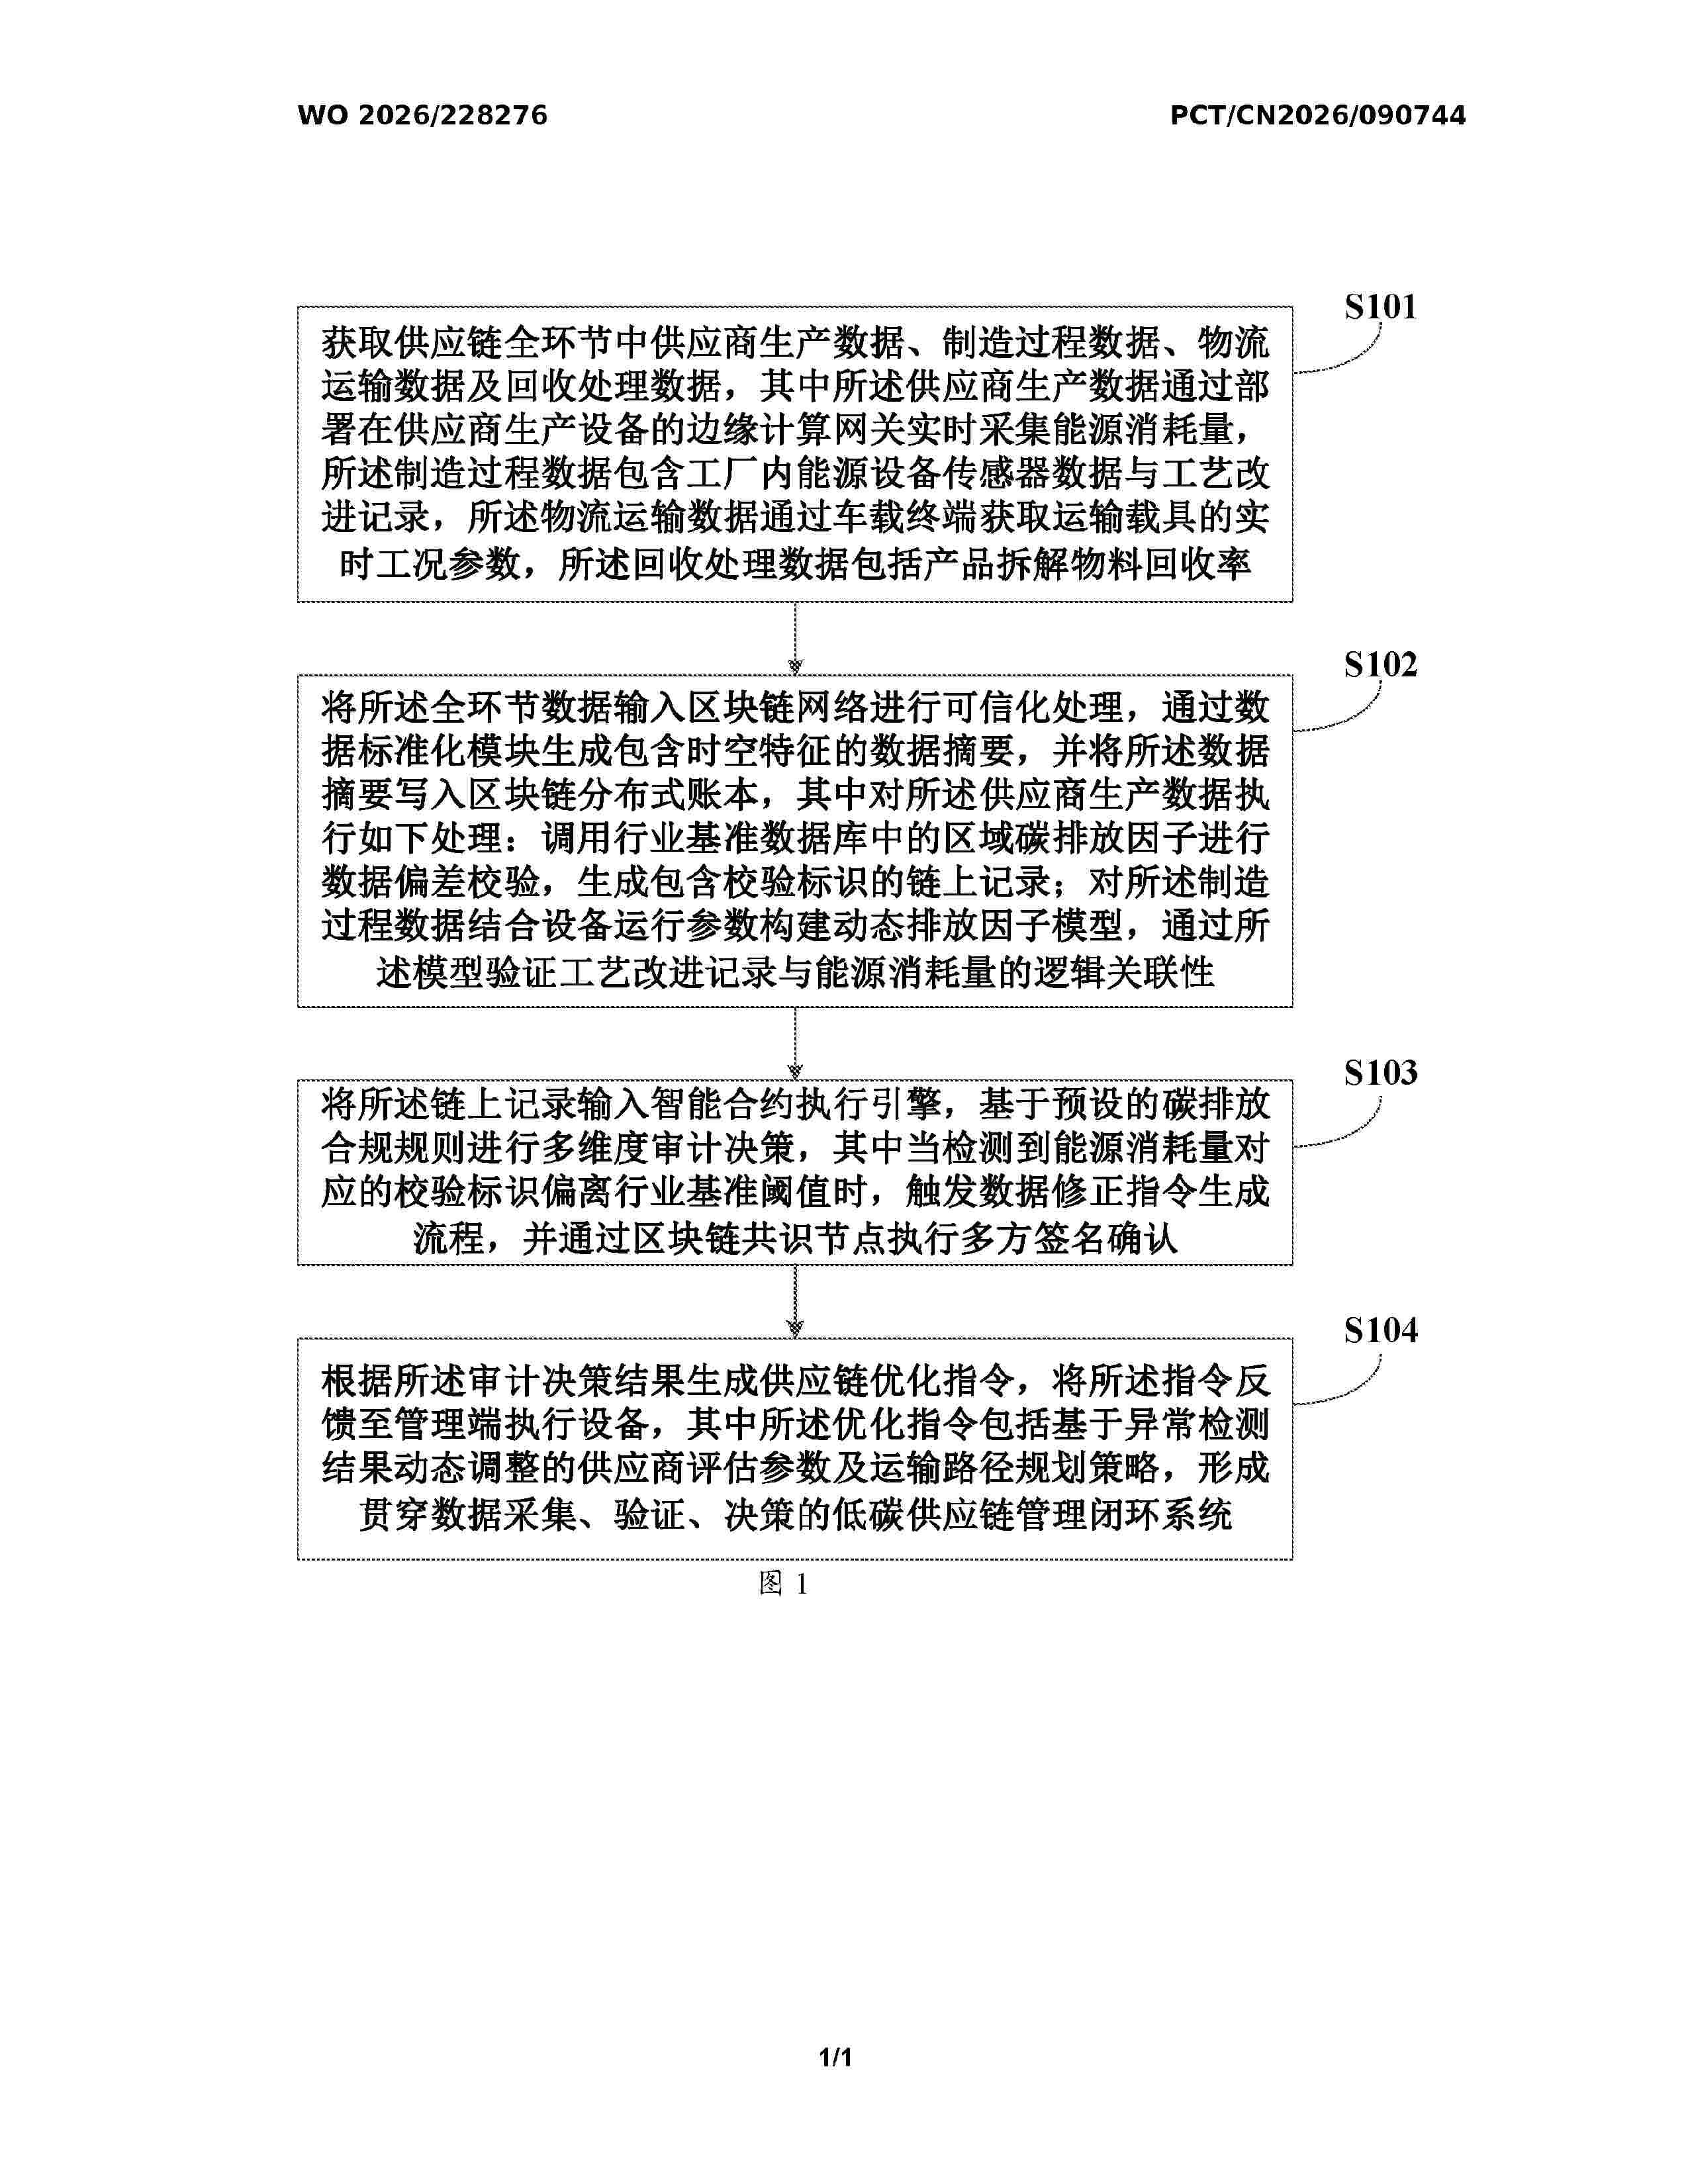
Resumen de: WO2026228276A1
Disclosed is a blockchain-based trusted management method for supply chain carbon data. Energy consumption of a supplier production device is collected in real time by means of a deployed edge computing gateway, real-time working condition parameters of a logistics transport vehicle are acquired by means of a vehicle-mounted terminal, material disassembly data from a recycling treatment stage is integrated, and a multi-source data collection system covering all stages of a supply chain is established. A blockchain network performs trusted processing on the data; a regional carbon emission factor in an industry benchmark database is retrieved for deviation verification; a smart contract engine executes a multi-dimensional audit decision according to preset compliance rules; and when it is detected that the energy consumption deviates from a benchmark threshold, a data correction process requiring multi-party signature confirmation is triggered.
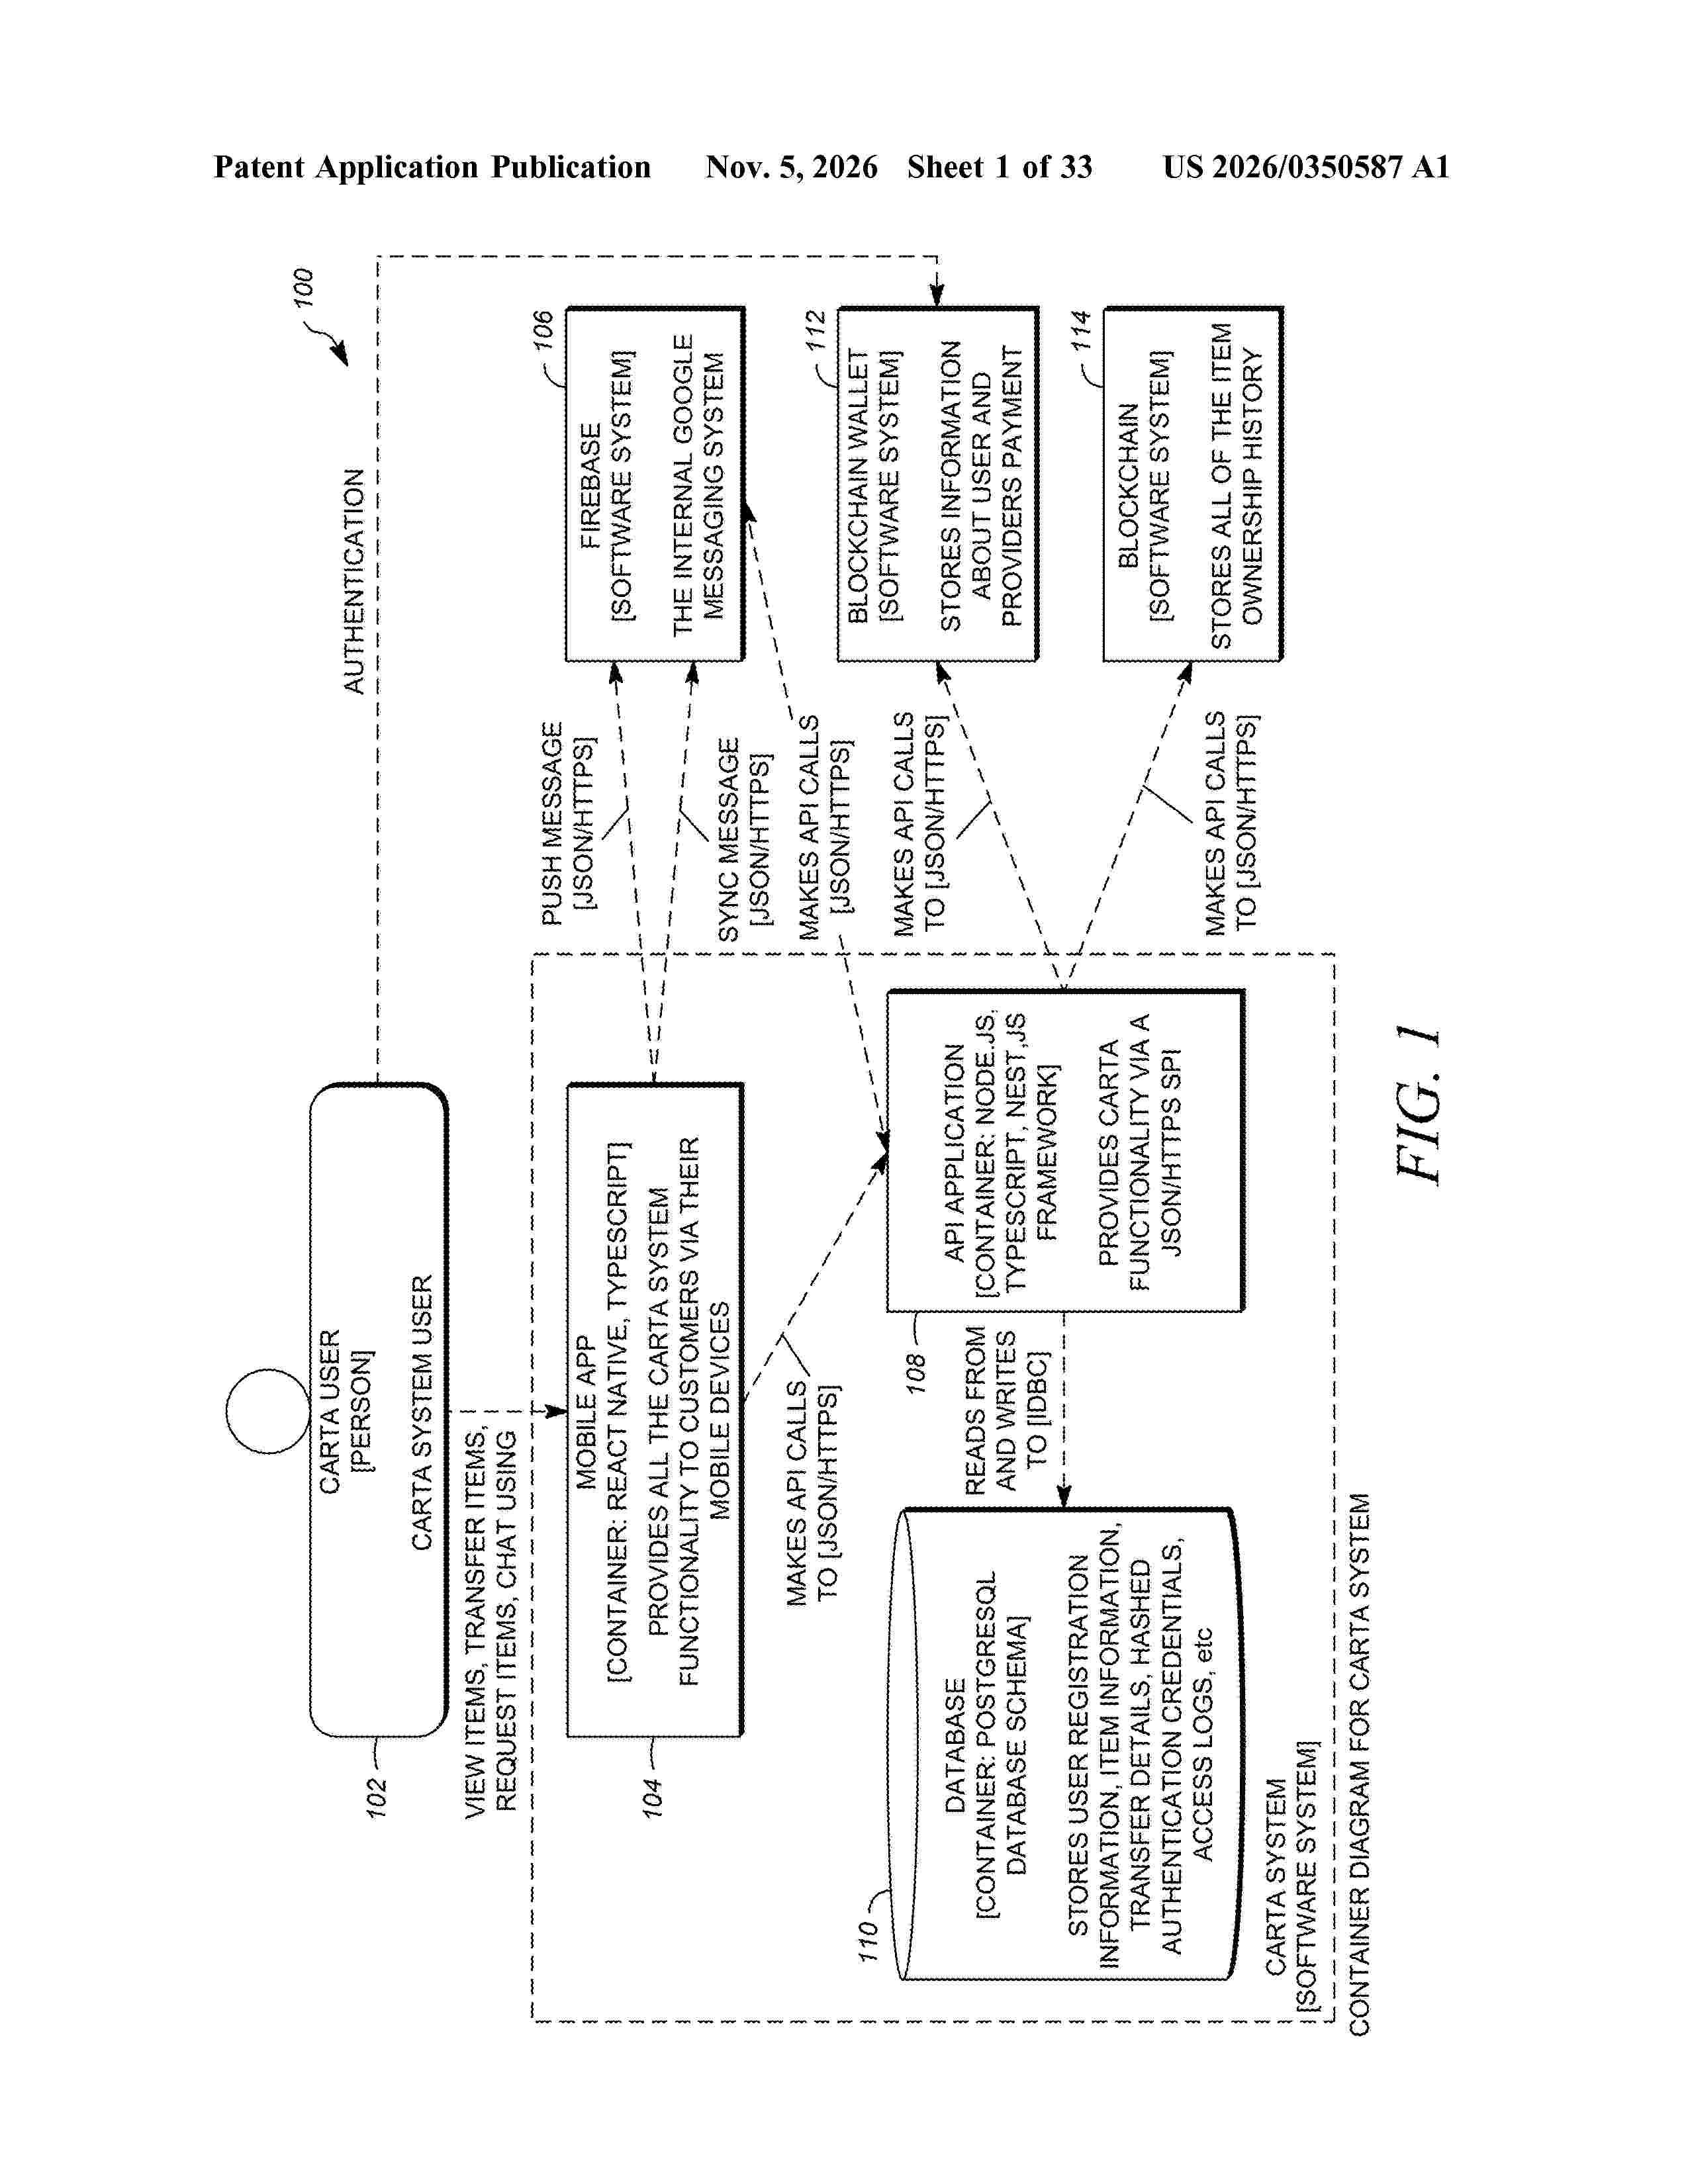
Resumen de: US20260350587A1
0000 A computerized method for non-fungible token authentication includes creating an asset non-fungible token (NFT) associated with a physical asset, storing, in a partner wallet, a link between the asset NFT and a tag attached to the physical asset, wherein the tag includes at least one of a radio-frequency identification (RFID) tag or a near-field communication tag, initiating a transfer of the asset NFT to a user, receiving confirmation of wireless communication between a mobile computing device of the user and the tag attached to the physical asset, and transferring the asset NFT into a user wallet in response to confirmation of wireless communication between a mobile computing device of the user and the tag attached to the physical asset.
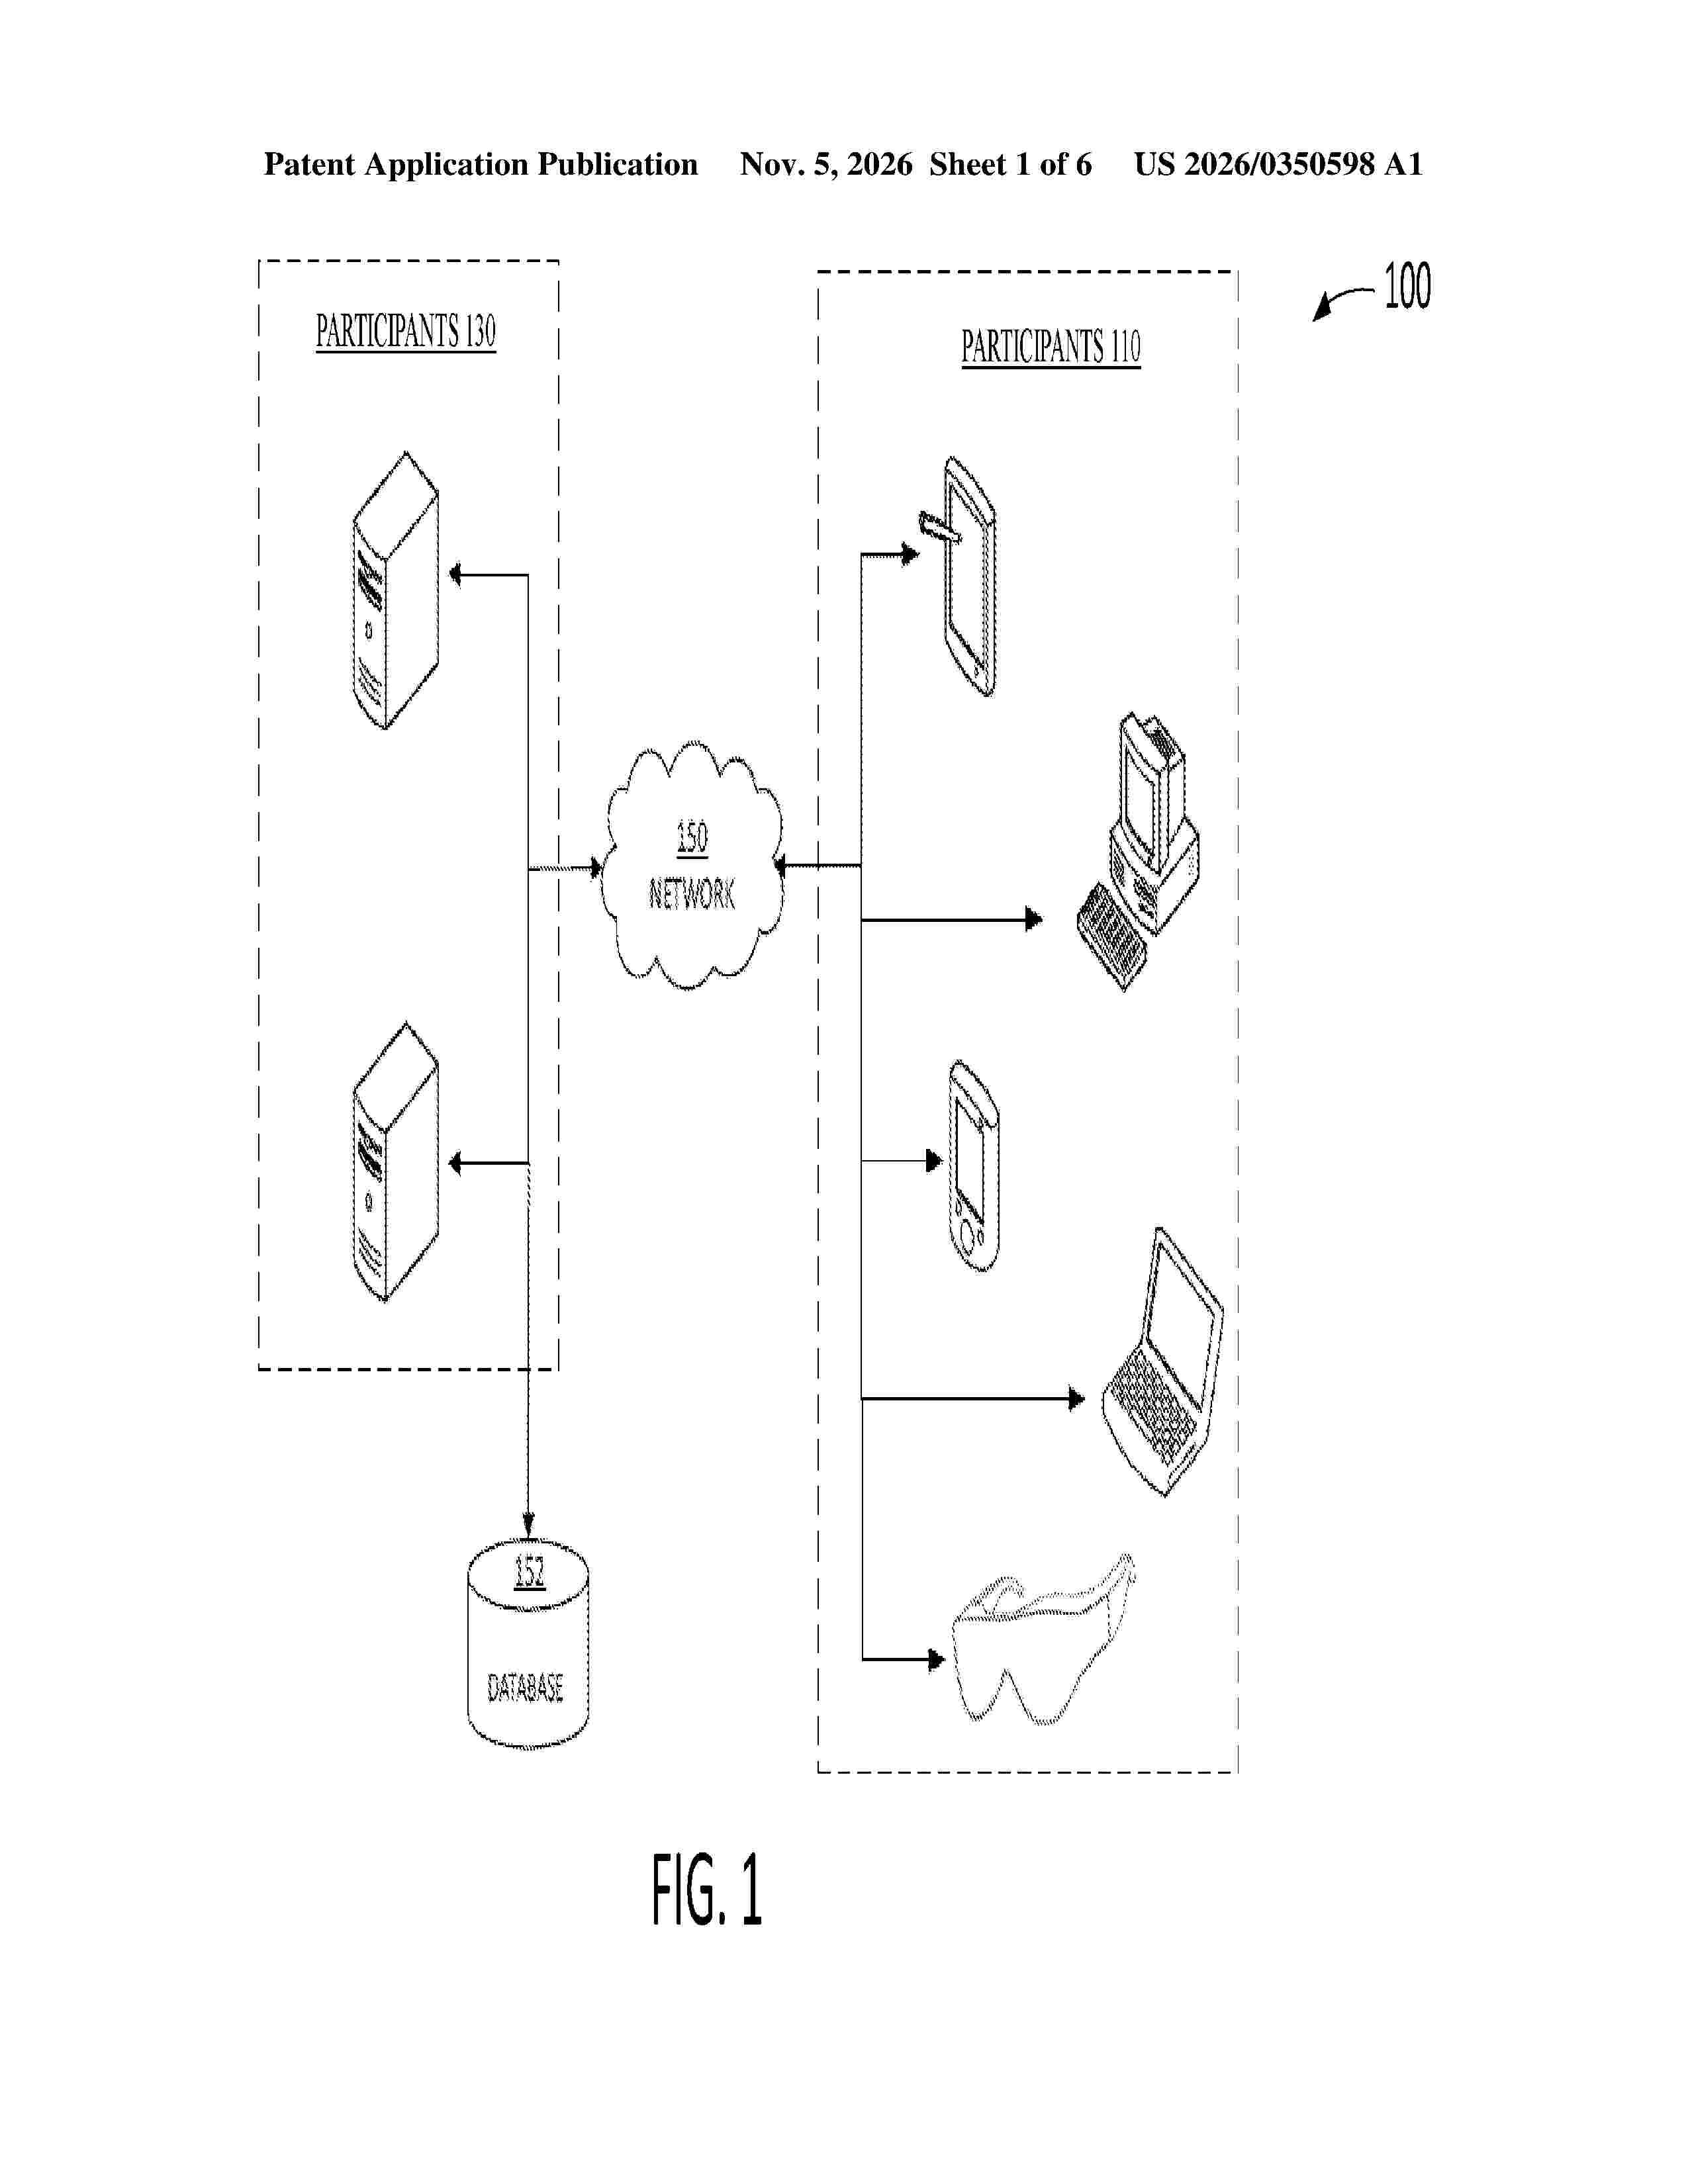
Resumen de: US20260350598A1
Various aspects of the subject technology relate to systems, methods, and machine-readable media for cross-chain communication in a blockchain platform. Various aspects may include accepting, at a first blockchain, a first transaction including a message and a message payload. Aspects may also include validating, at the first blockchain, the message by signing the message using signature keys of one or more validators in a first set of validators of the first blockchain. Aspects may also include generating an aggregate signature based on the signature keys of the one or more validators in a first set of validators. Aspects may also include submitting a second transaction on to a second blockchain, the second transaction including the message and the aggregate signature. Aspects may include validating, at the second blockchain, the second transaction based on a shared registry.
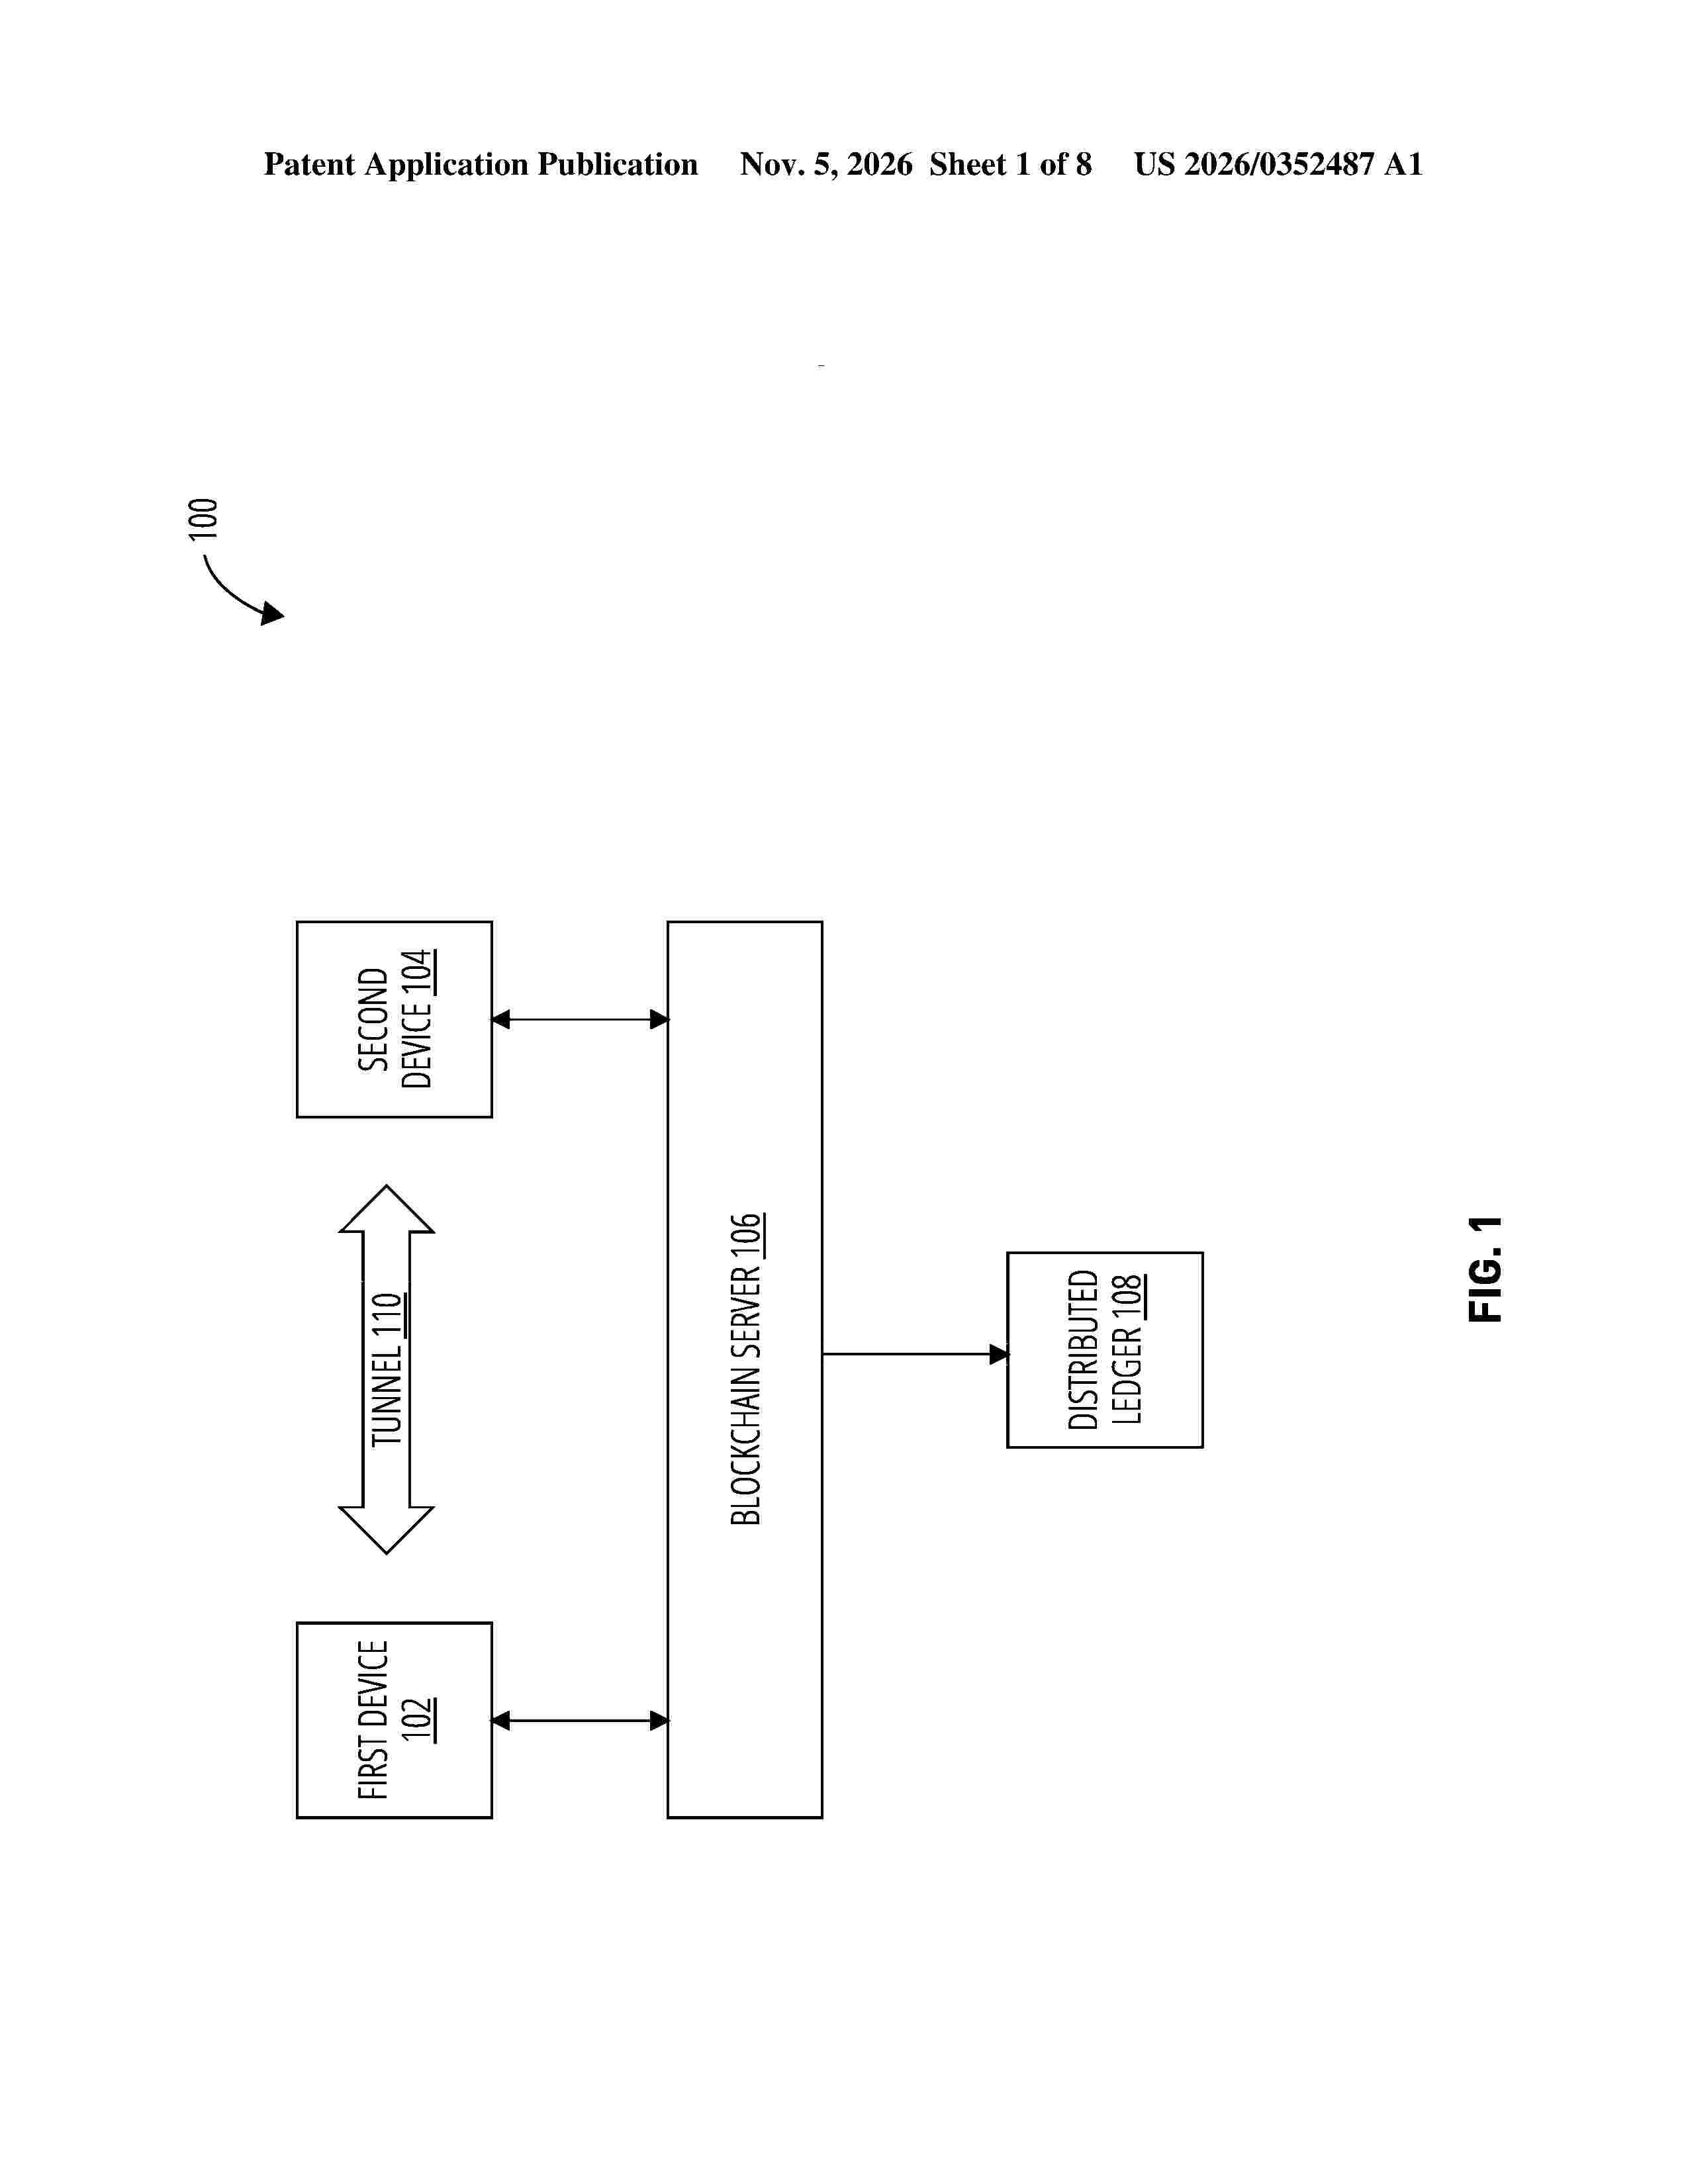
Resumen de: US20260352487A1
The present technology includes systems and methods for low-latency, stateful interactions between two parties in a blockchain environment by shifting execution of application logic off-chain while preserving security and verifiability. An off-chain communication channel is established in association with an on-chain smart contract, allowing the parties to exchange a sequence of cryptographically authenticated state updates that collectively represent a current interaction state. A respective update is validated through coordinated cryptographic operations between the parties, forming a verifiable chain of state transitions. The disclosed approach reduces on-chain transaction overhead while maintaining trust, enabling applications such as interactive gaming, streaming services, and incremental payment systems.
Resumen de: US20260350597A1
Methods, systems, and devices for data management are described. A first user device for a blockchain network may communicate first signaling to initiate an import session for a blockchain wallet associated with a device-based passkey associated with a second user device, where the first signaling may include a random secret. The first user device may receive an indication that the import session is associated with the second user device and may generate a new passkey associated with the first user device. The first user device may transmit second signaling including an encrypted credential identifier associated with the new passkey, where the encrypted credential identifier may be encrypted based on the random secret. The second user device may sign a blockchain transaction authorizing access to the blockchain wallet using the new passkey, and the first user device may access the blockchain wallet using the new passkey.
Resumen de: US20260350229A1
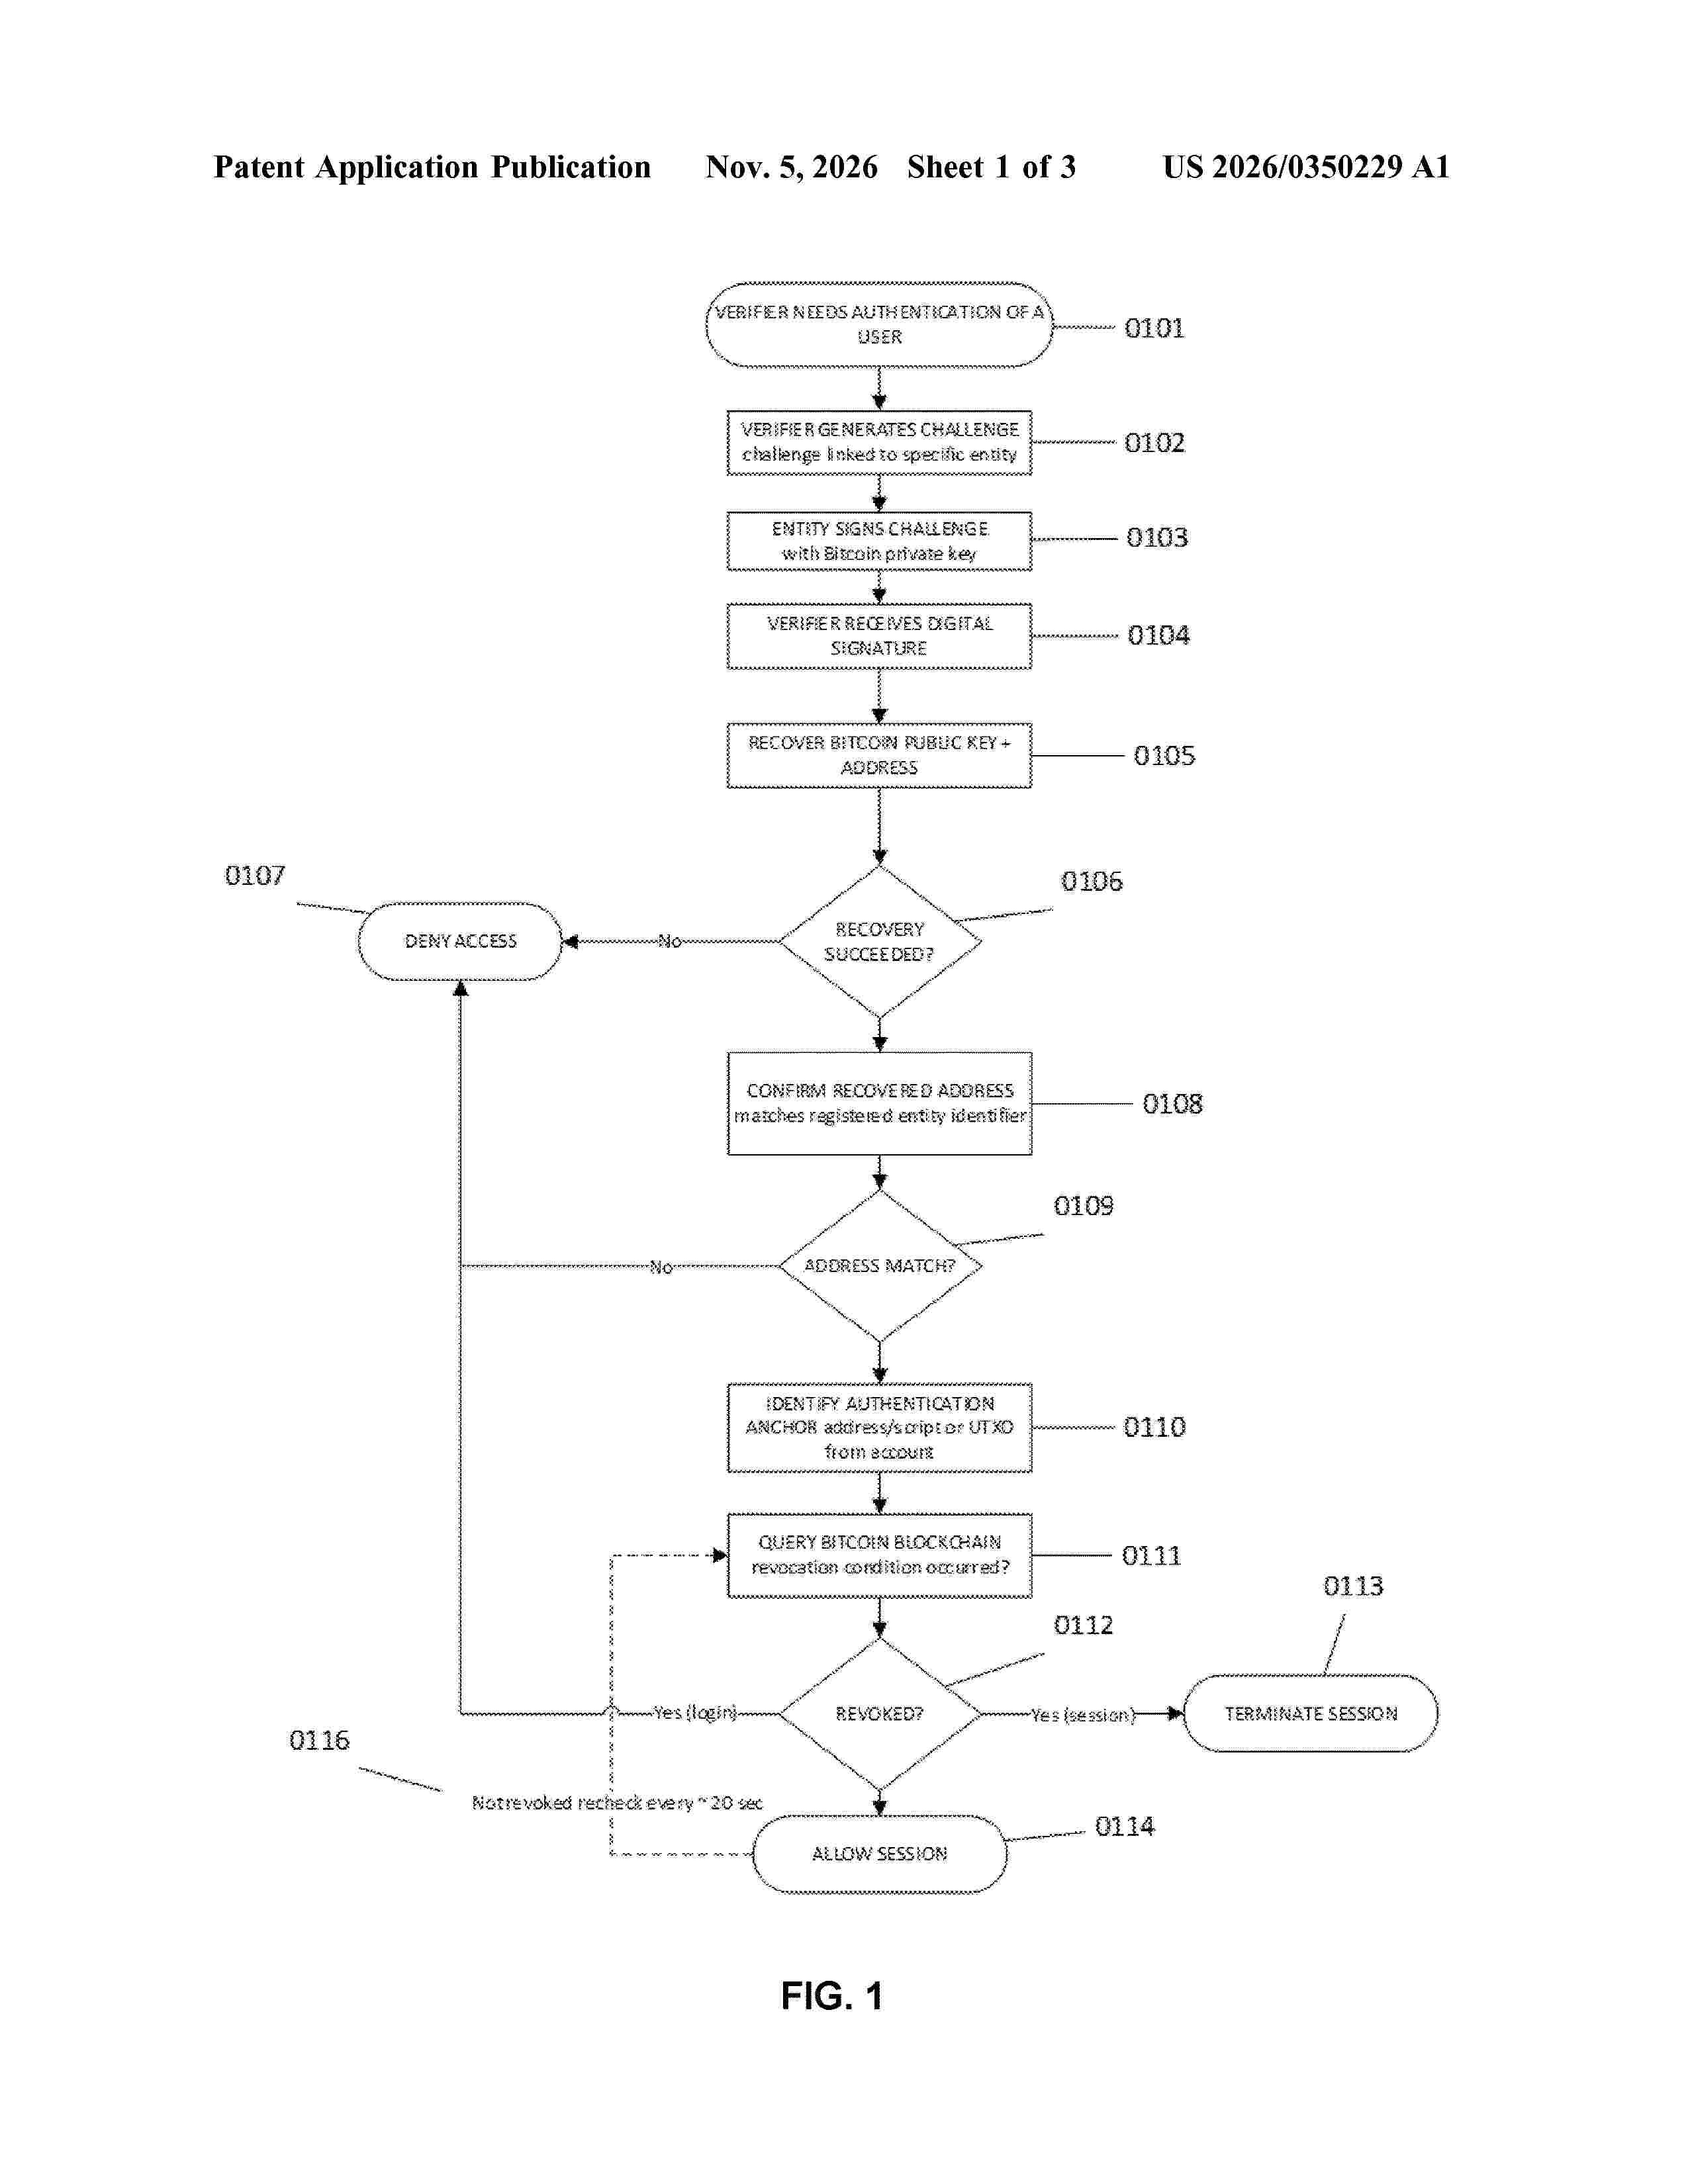
A computer-implemented method, system, and non-transitory computer-readable medium for authentication and access control. A verifier generates a challenge message and receives a digital signature over the challenge message from an entity. The verifier recovers a Bitcoin public key and a corresponding Bitcoin address mathematically from the digital signature without the Bitcoin public key having been transmitted by the entity. The verifier determines an authentication anchor associated with the entity, the authentication anchor comprising a Bitcoin address or locking script or a designated unspent transaction output, and queries Bitcoin blockchain data to determine whether a revocation condition associated with the authentication anchor has occurred. Access is authorized only when the digital signature is valid and the authentication anchor is unrevoked. Embodiments include hierarchical delegation, multi-signature anchors, continuous session monitoring, and registry-based identification.
Resumen de: US20260350632A1
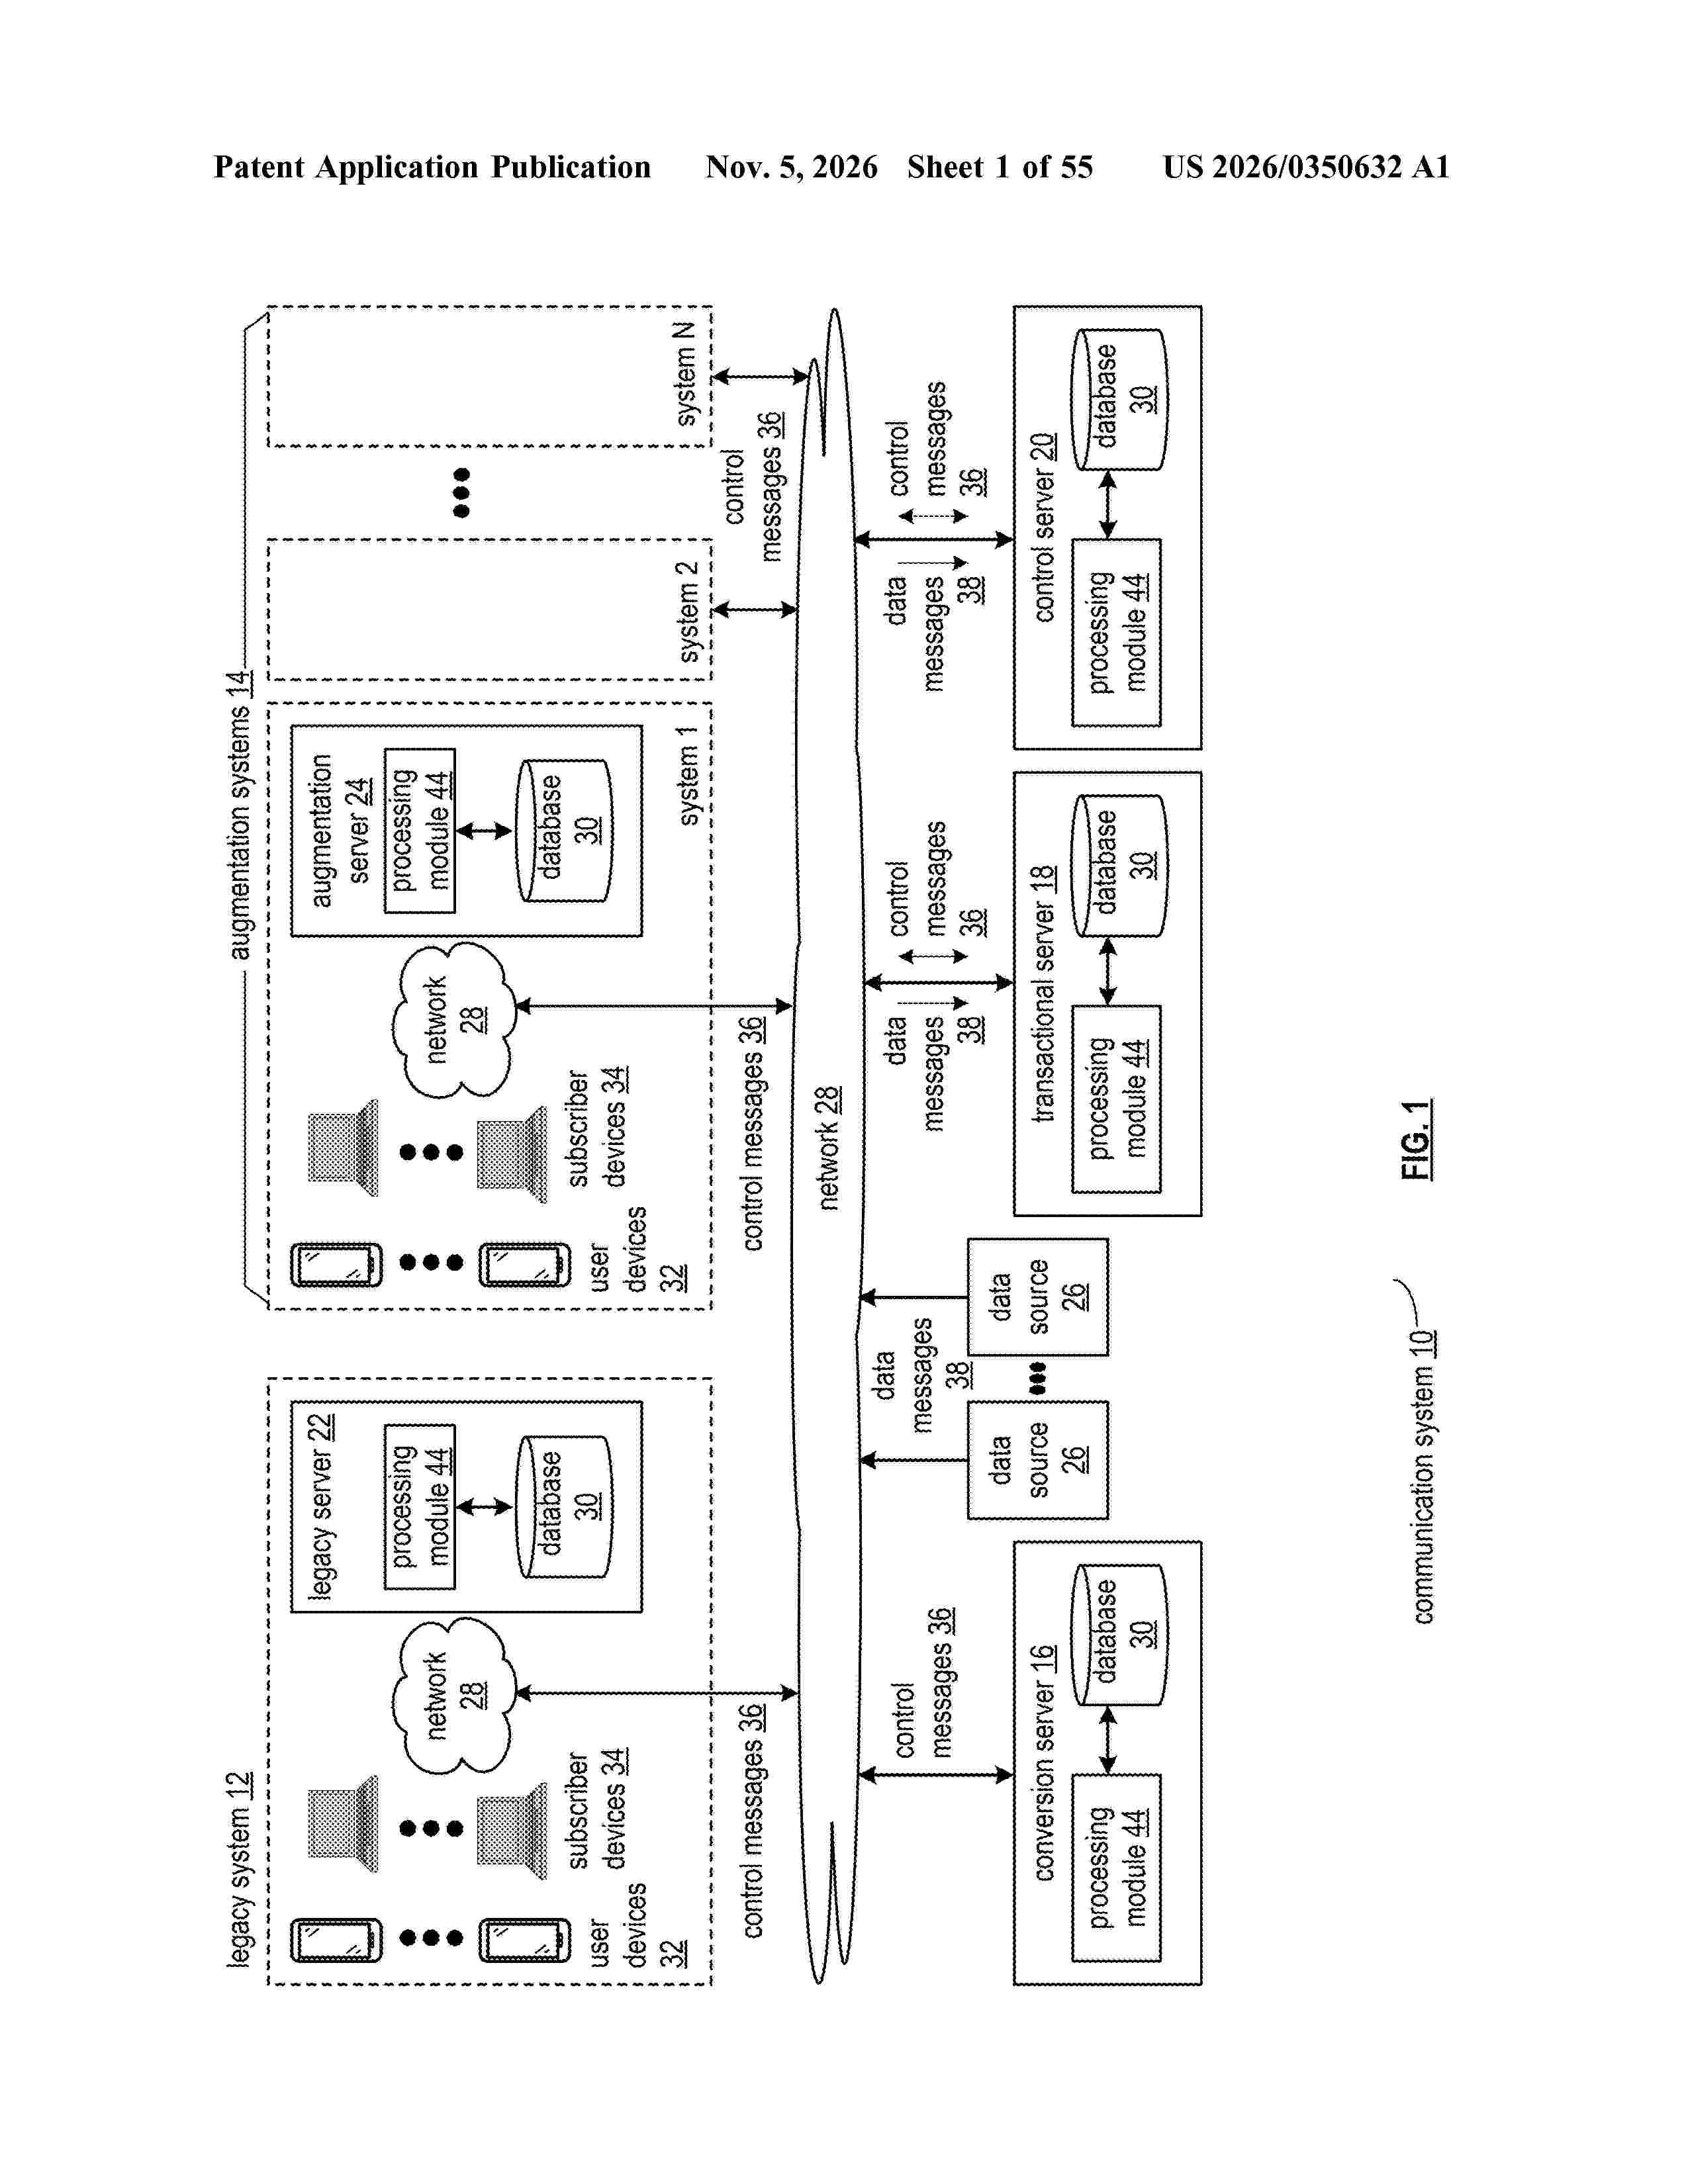
A method executed by a computing device includes determining specific terms associated with a trademark contingent instrument for a contingency-action token (CAT) for an object distributed ledger. The method further includes establishing CAT content to include the specific terms and further CAT content to produce the CAT. The method further includes using a securely passing process to generate a new block affiliated with the CAT via a blockchain of the object distributed ledger, where the new block includes the CAT content.
Resumen de: US20260350588A1
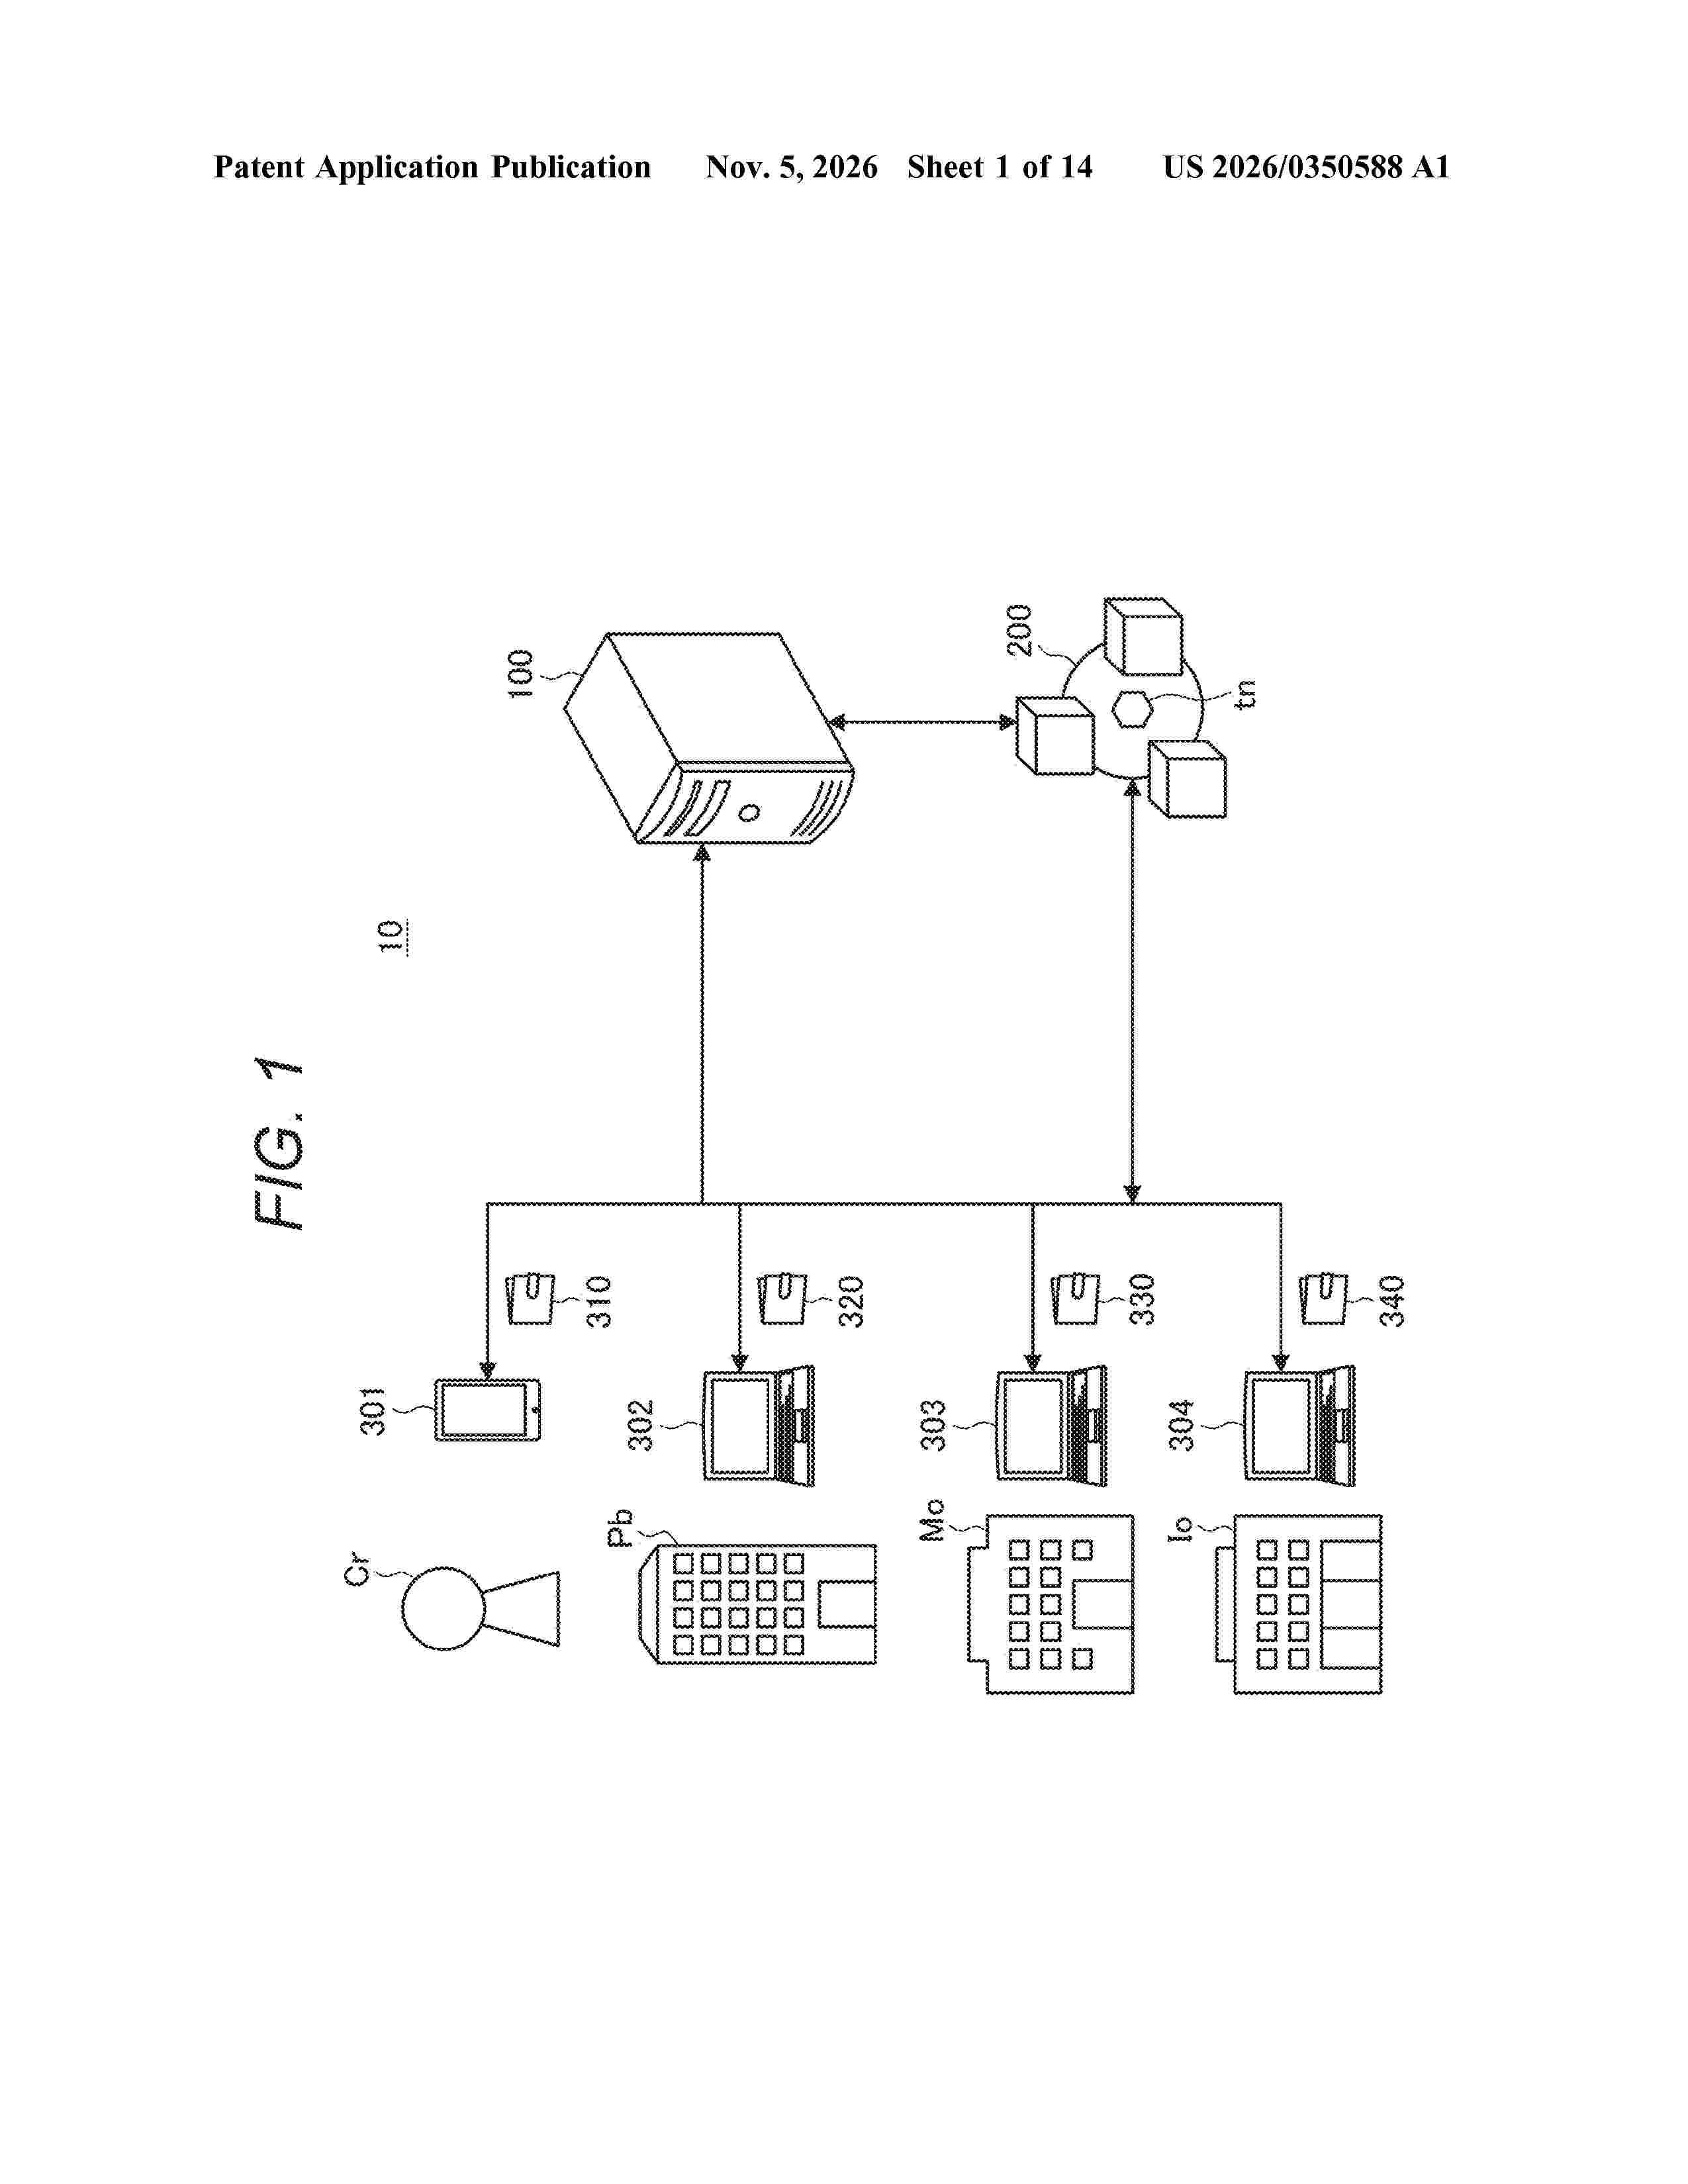
To manage information regarding a beneficiary of a consideration for rights on a blockchain. A program for causing a computer to function as: an issuance information generation unit that generates information for issuing a divisible token that includes information regarding a benefit ratio of a consideration and operates on a blockchain; and a division information generation unit that generates information for issuing the token divided on the basis of distribution information of the consideration based on an agreement to a beneficiary of the consideration.
Resumen de: US20260350172A1
0000 A computer-implemented method for booting a device using a portable boot loader device, wherein the portable boot loader device comprises a boot loader and operating system files, wherein a blockchain comprises a boot loader transaction, wherein the boot loader transaction comprises an output locked to a master public key, and wherein the boot loader transaction comprises a first signature signing the boot loader and a second signature signing the operating system files, and wherein the method comprises: obtaining the boot loader transaction; verifying the first signature using the master public key; verifying the second signature using the master public key; and loading the operating system files using the boot loader.
Resumen de: US20260350595A1
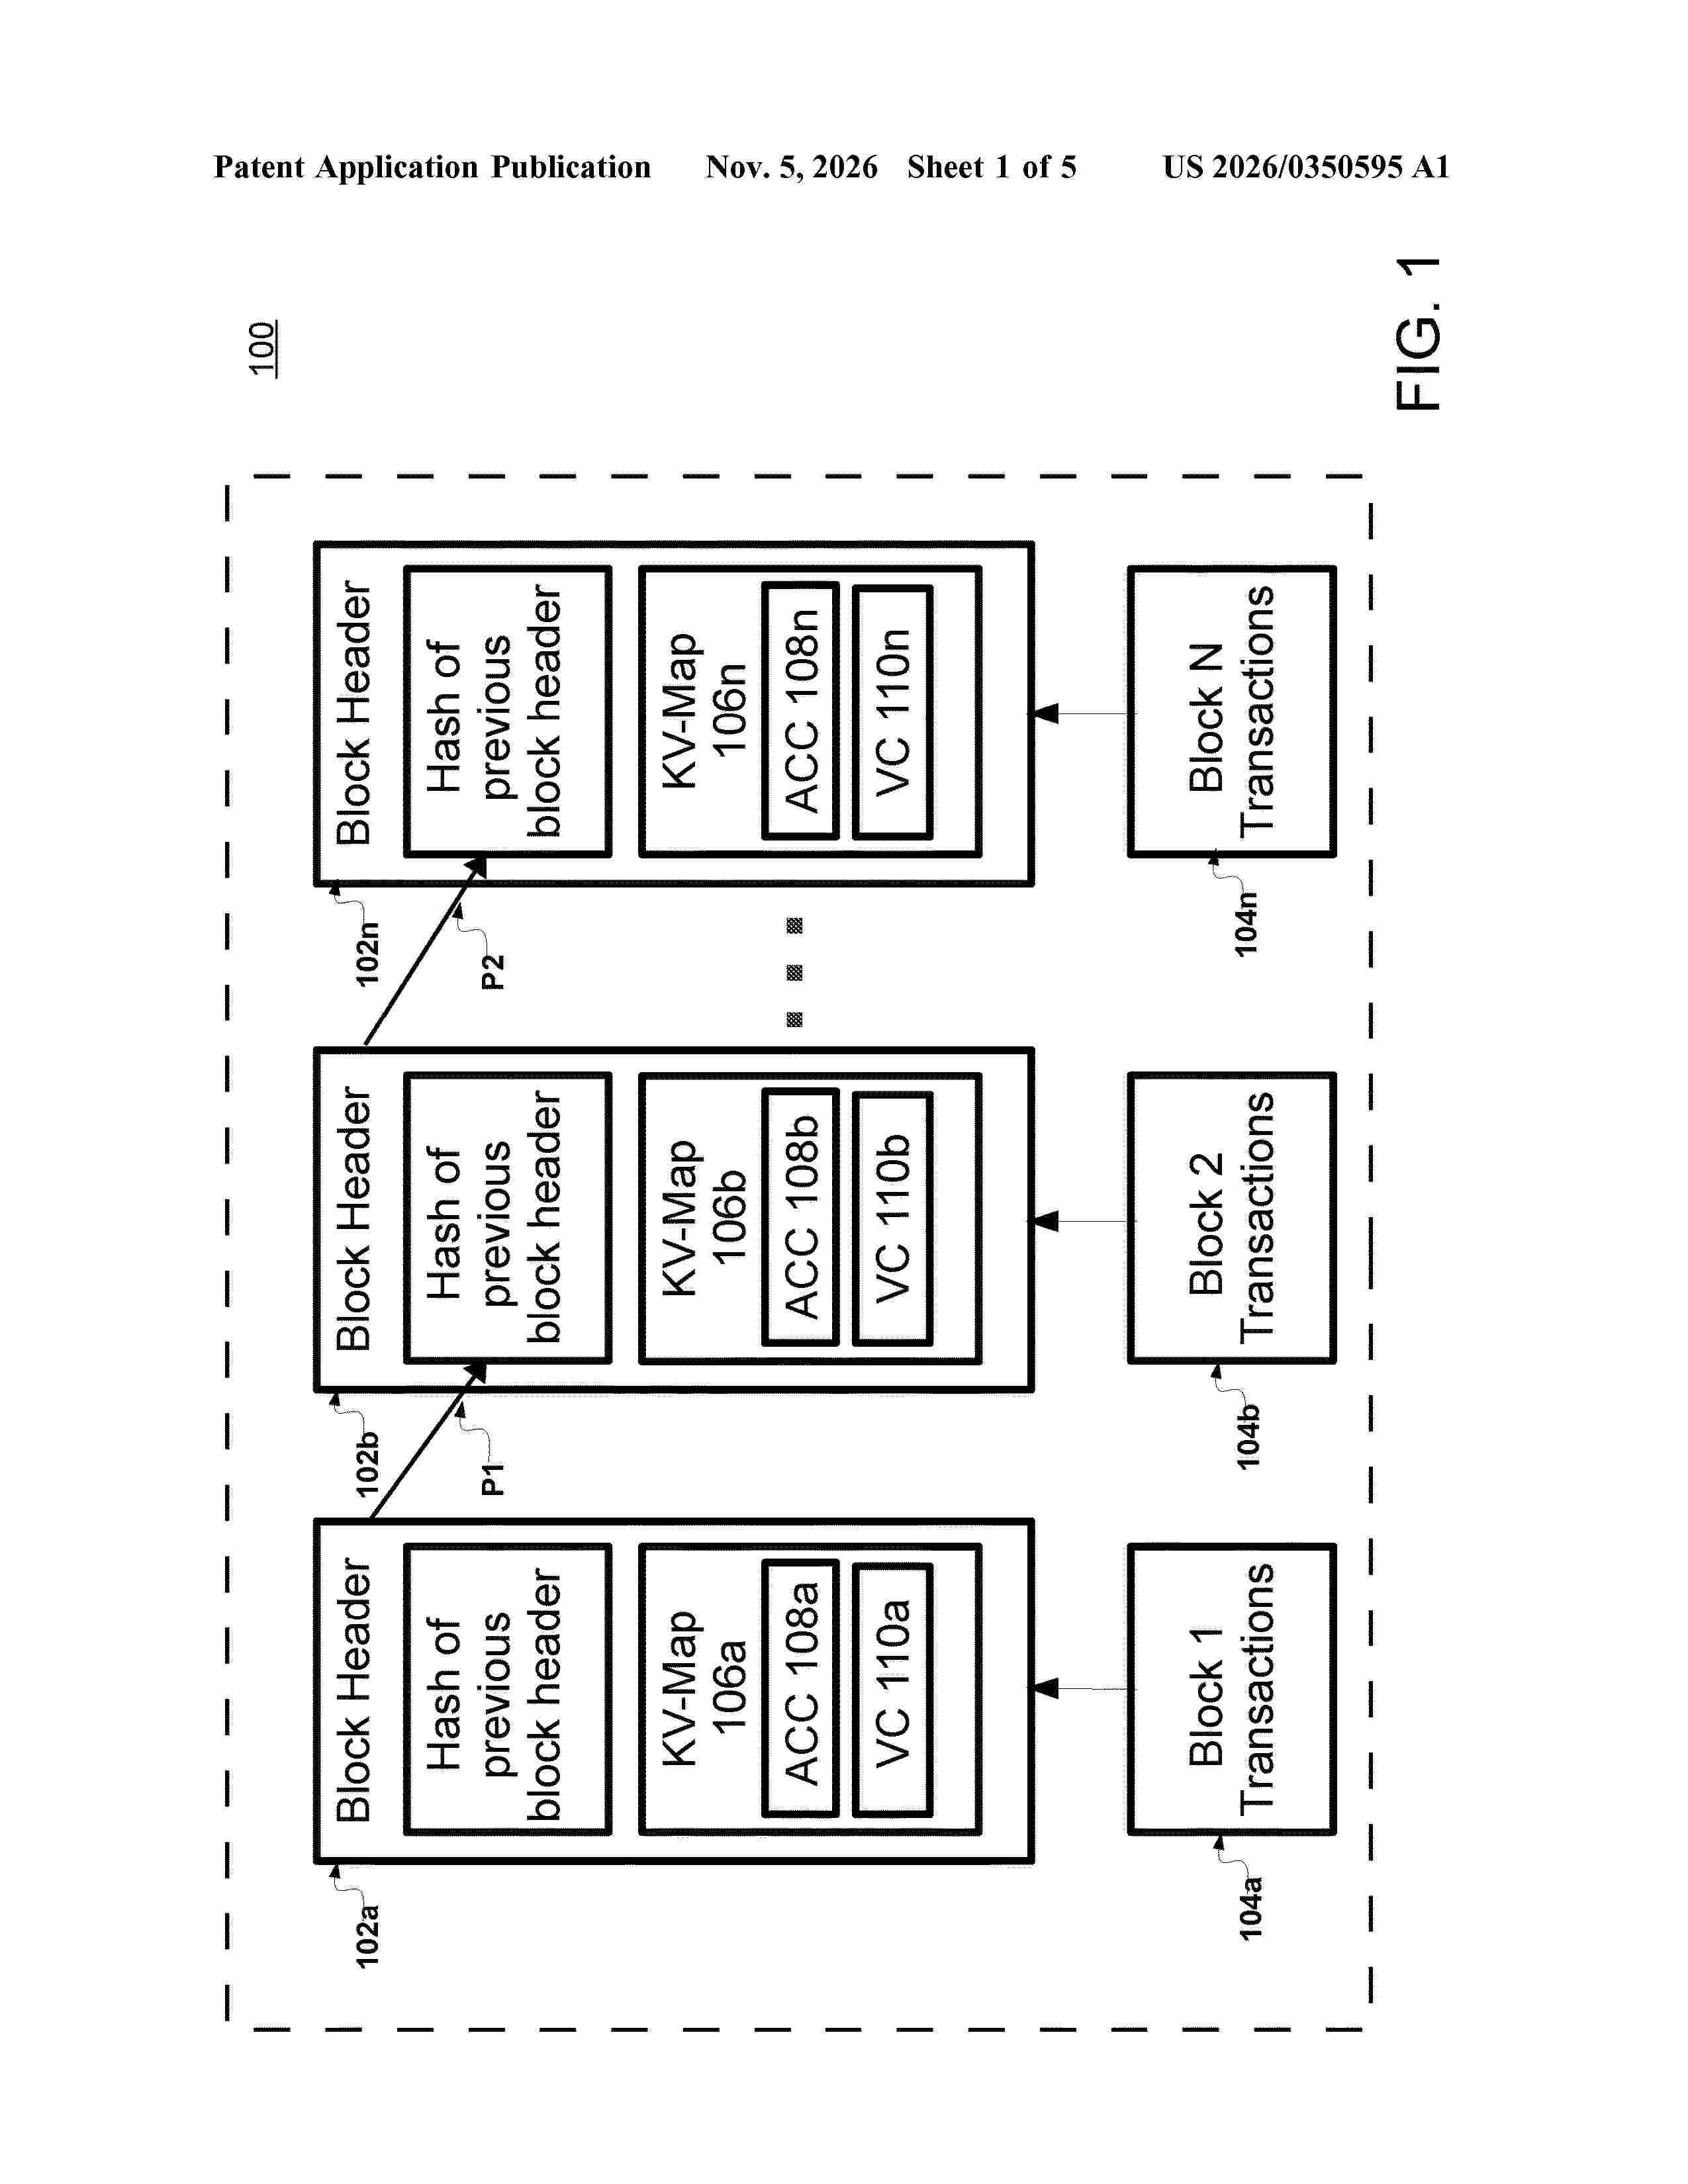
System, method, and computer program products are provided for key-value commitments from accumulators and vector commitments. The system includes at least one processor, configured to generate an accumulator commitment for a plurality of key-value pairs of a block in a blockchain network, the accumulator commitment cryptographically adding each key-value commitment of the block; obtain a new transaction for the block; determine a membership proof or non-membership proof to verify at least one accumulated value from one or more previous transactions; and authenticate the new transaction based on at least one proof to verify membership or non-membership based on the at least one accumulated value.
Resumen de: US20260350627A1
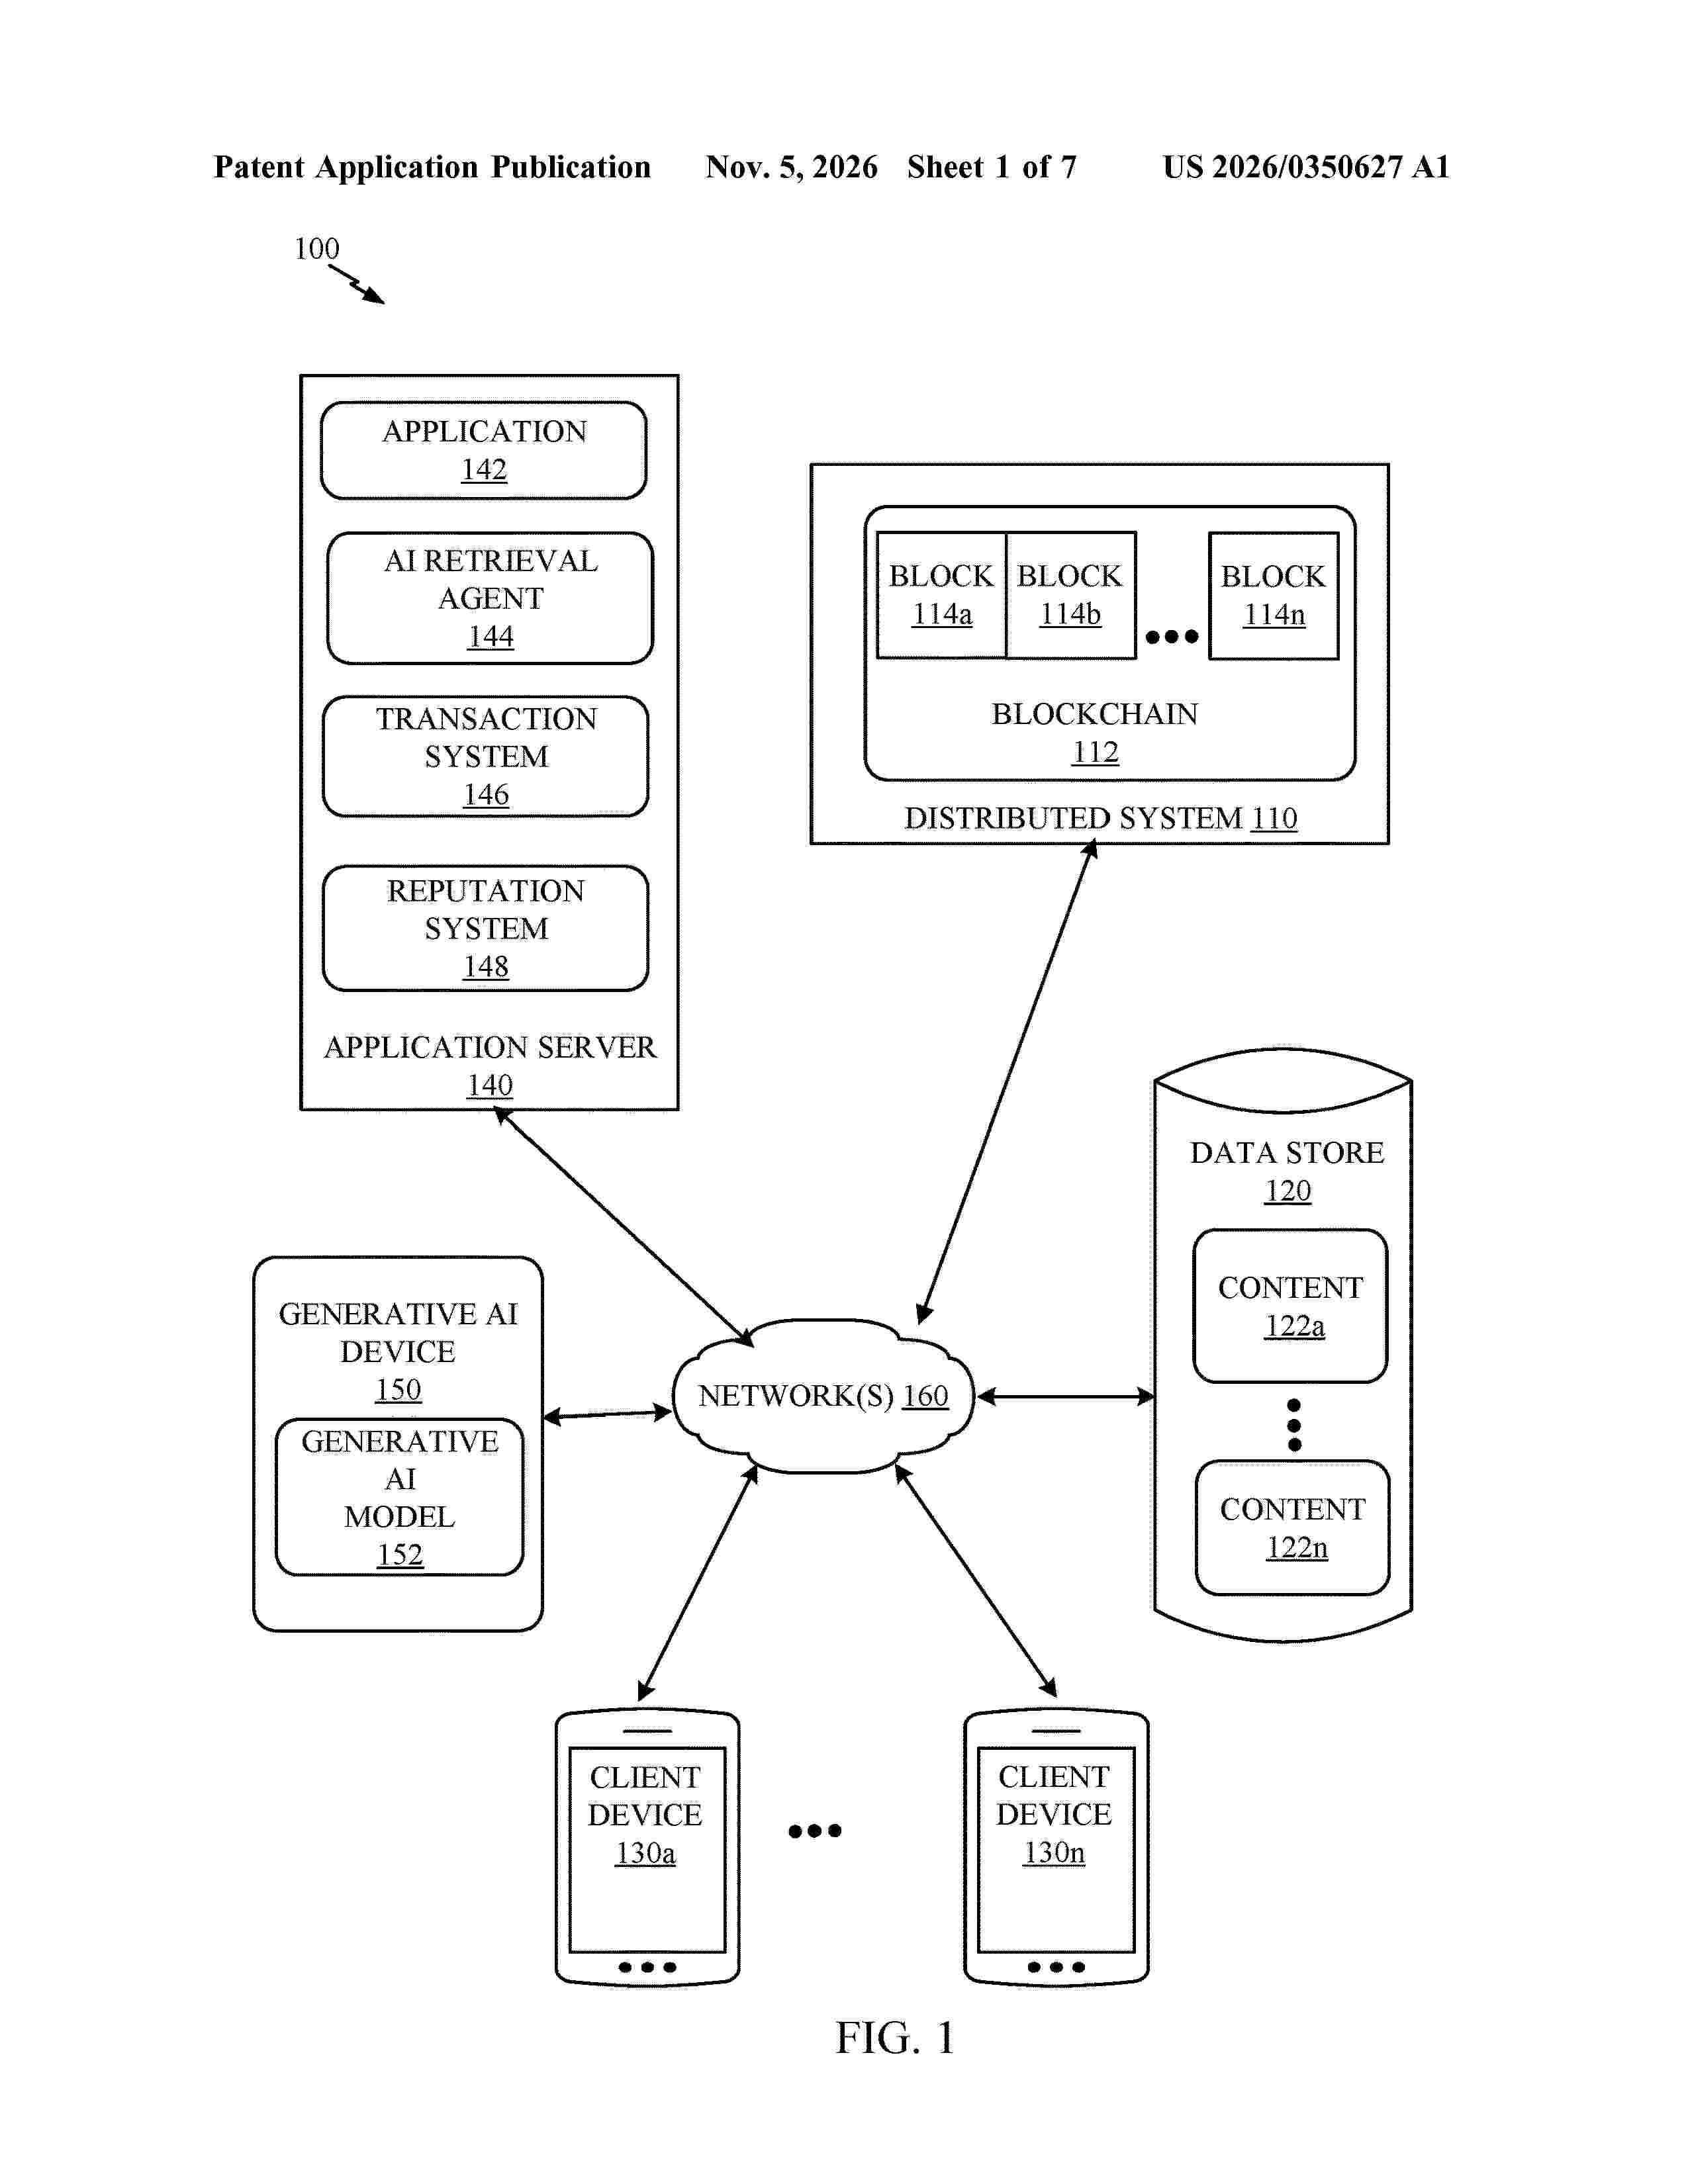
0000 Embodiments of the present disclosure are directed to a method for sharing relevant content on a blockchain. The method includes determining, using an artificial intelligence retrieval technique, whether encrypted content recorded on the blockchain includes information that is relevant to a query generated based on data that is descriptive of the encrypted content. In response to determining the encrypted content includes information that is relevant to the query, the method includes providing the information and the query as inputs to a generative artificial intelligence model configured to determine whether the information satisfies criteria generated based on the data that is descriptive of the encrypted content. In response to determining the encrypted content does not include information that is relevant to the query, the method includes cancelling a blockchain transaction involving a first user that generated the query and a second user that authored the encrypted content.
Resumen de: US20260352451A1
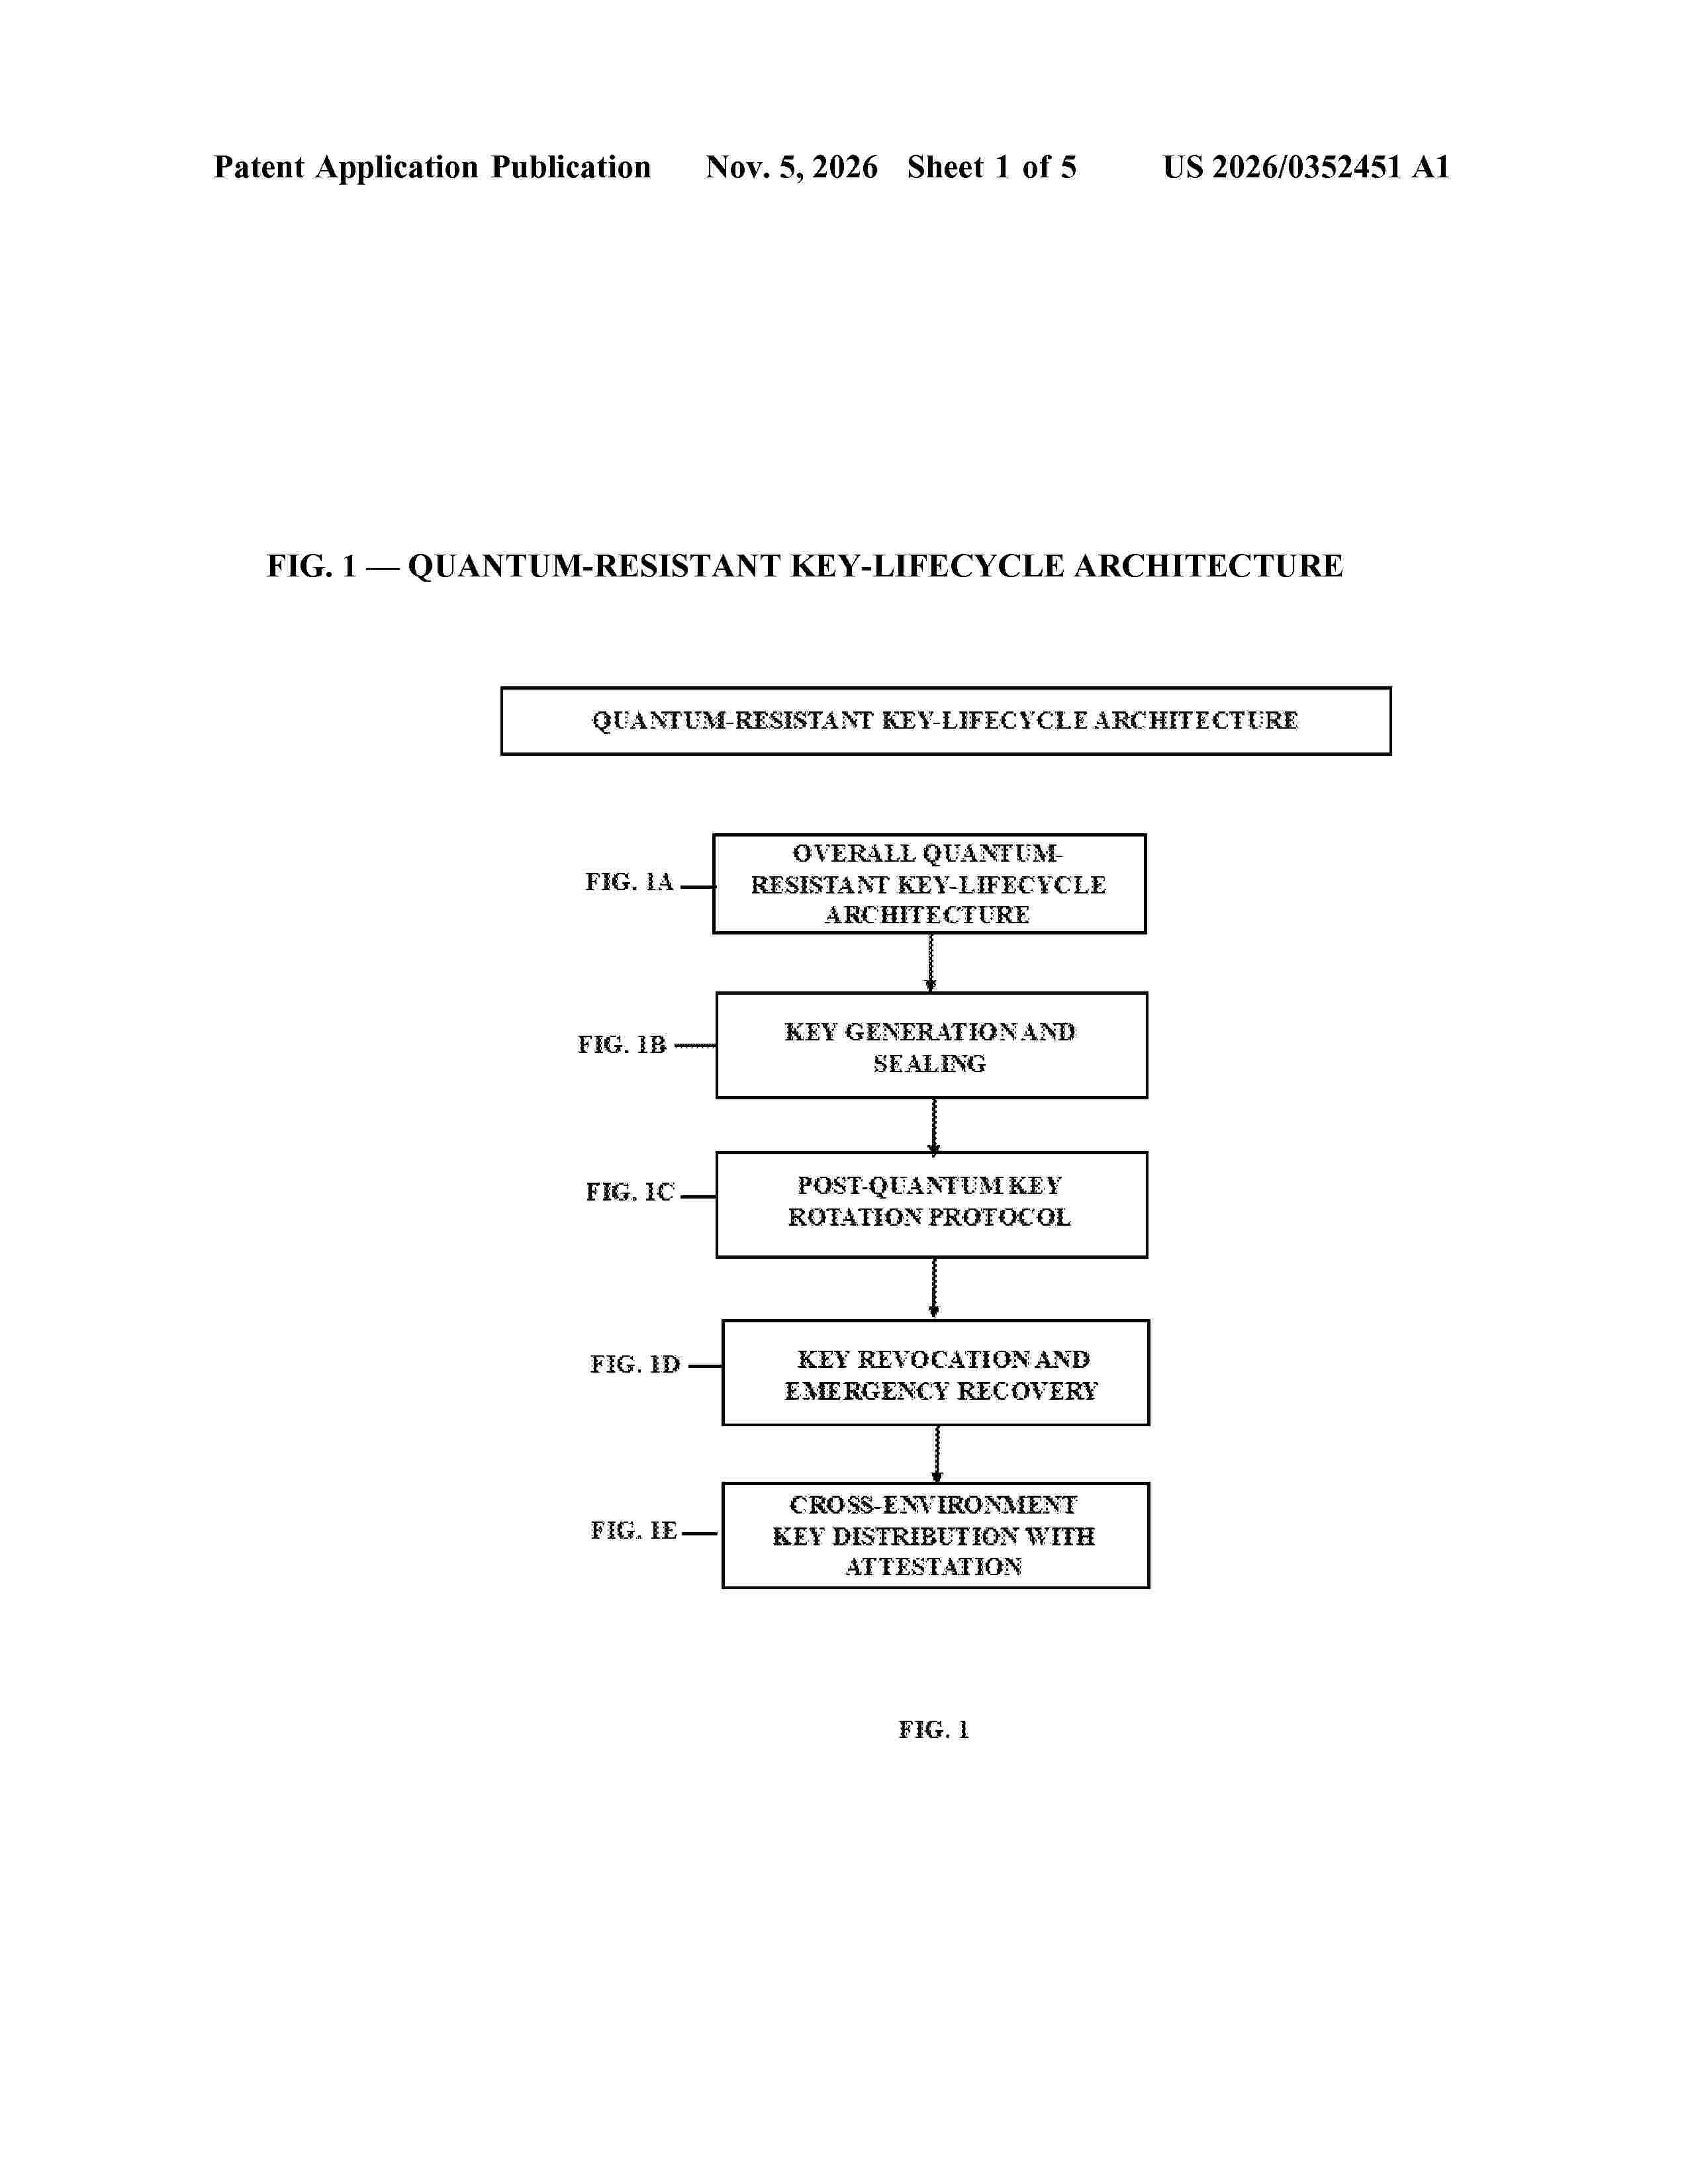
0000 A quantum-resistant system manages the key and model lifecycle of an artificial intelligence model within a trusted execution environment (TEE). A key management engine generates, seals, rotates, and revokes post-quantum keys bound to a hardware-rooted measurement. A secure model update module applies attested changes linking a prior state to a new state. A verifiable fine-tuning module binds, as a single signed unit, digests of training data, gradients, and resulting weights to the measurement. A tamper-evident provenance ledger records the operations and may anchor digests to a public blockchain. The system may mint a self-sovereign agent identity for consumption by a separate orchestration subsystem. Keys, updates, and evidence exist unencrypted only within the TEE and are tamper-evidently bound to the measurement, so an operator cannot alter or suppress them without invalidating the attestation.
Resumen de: WO2026229339A1
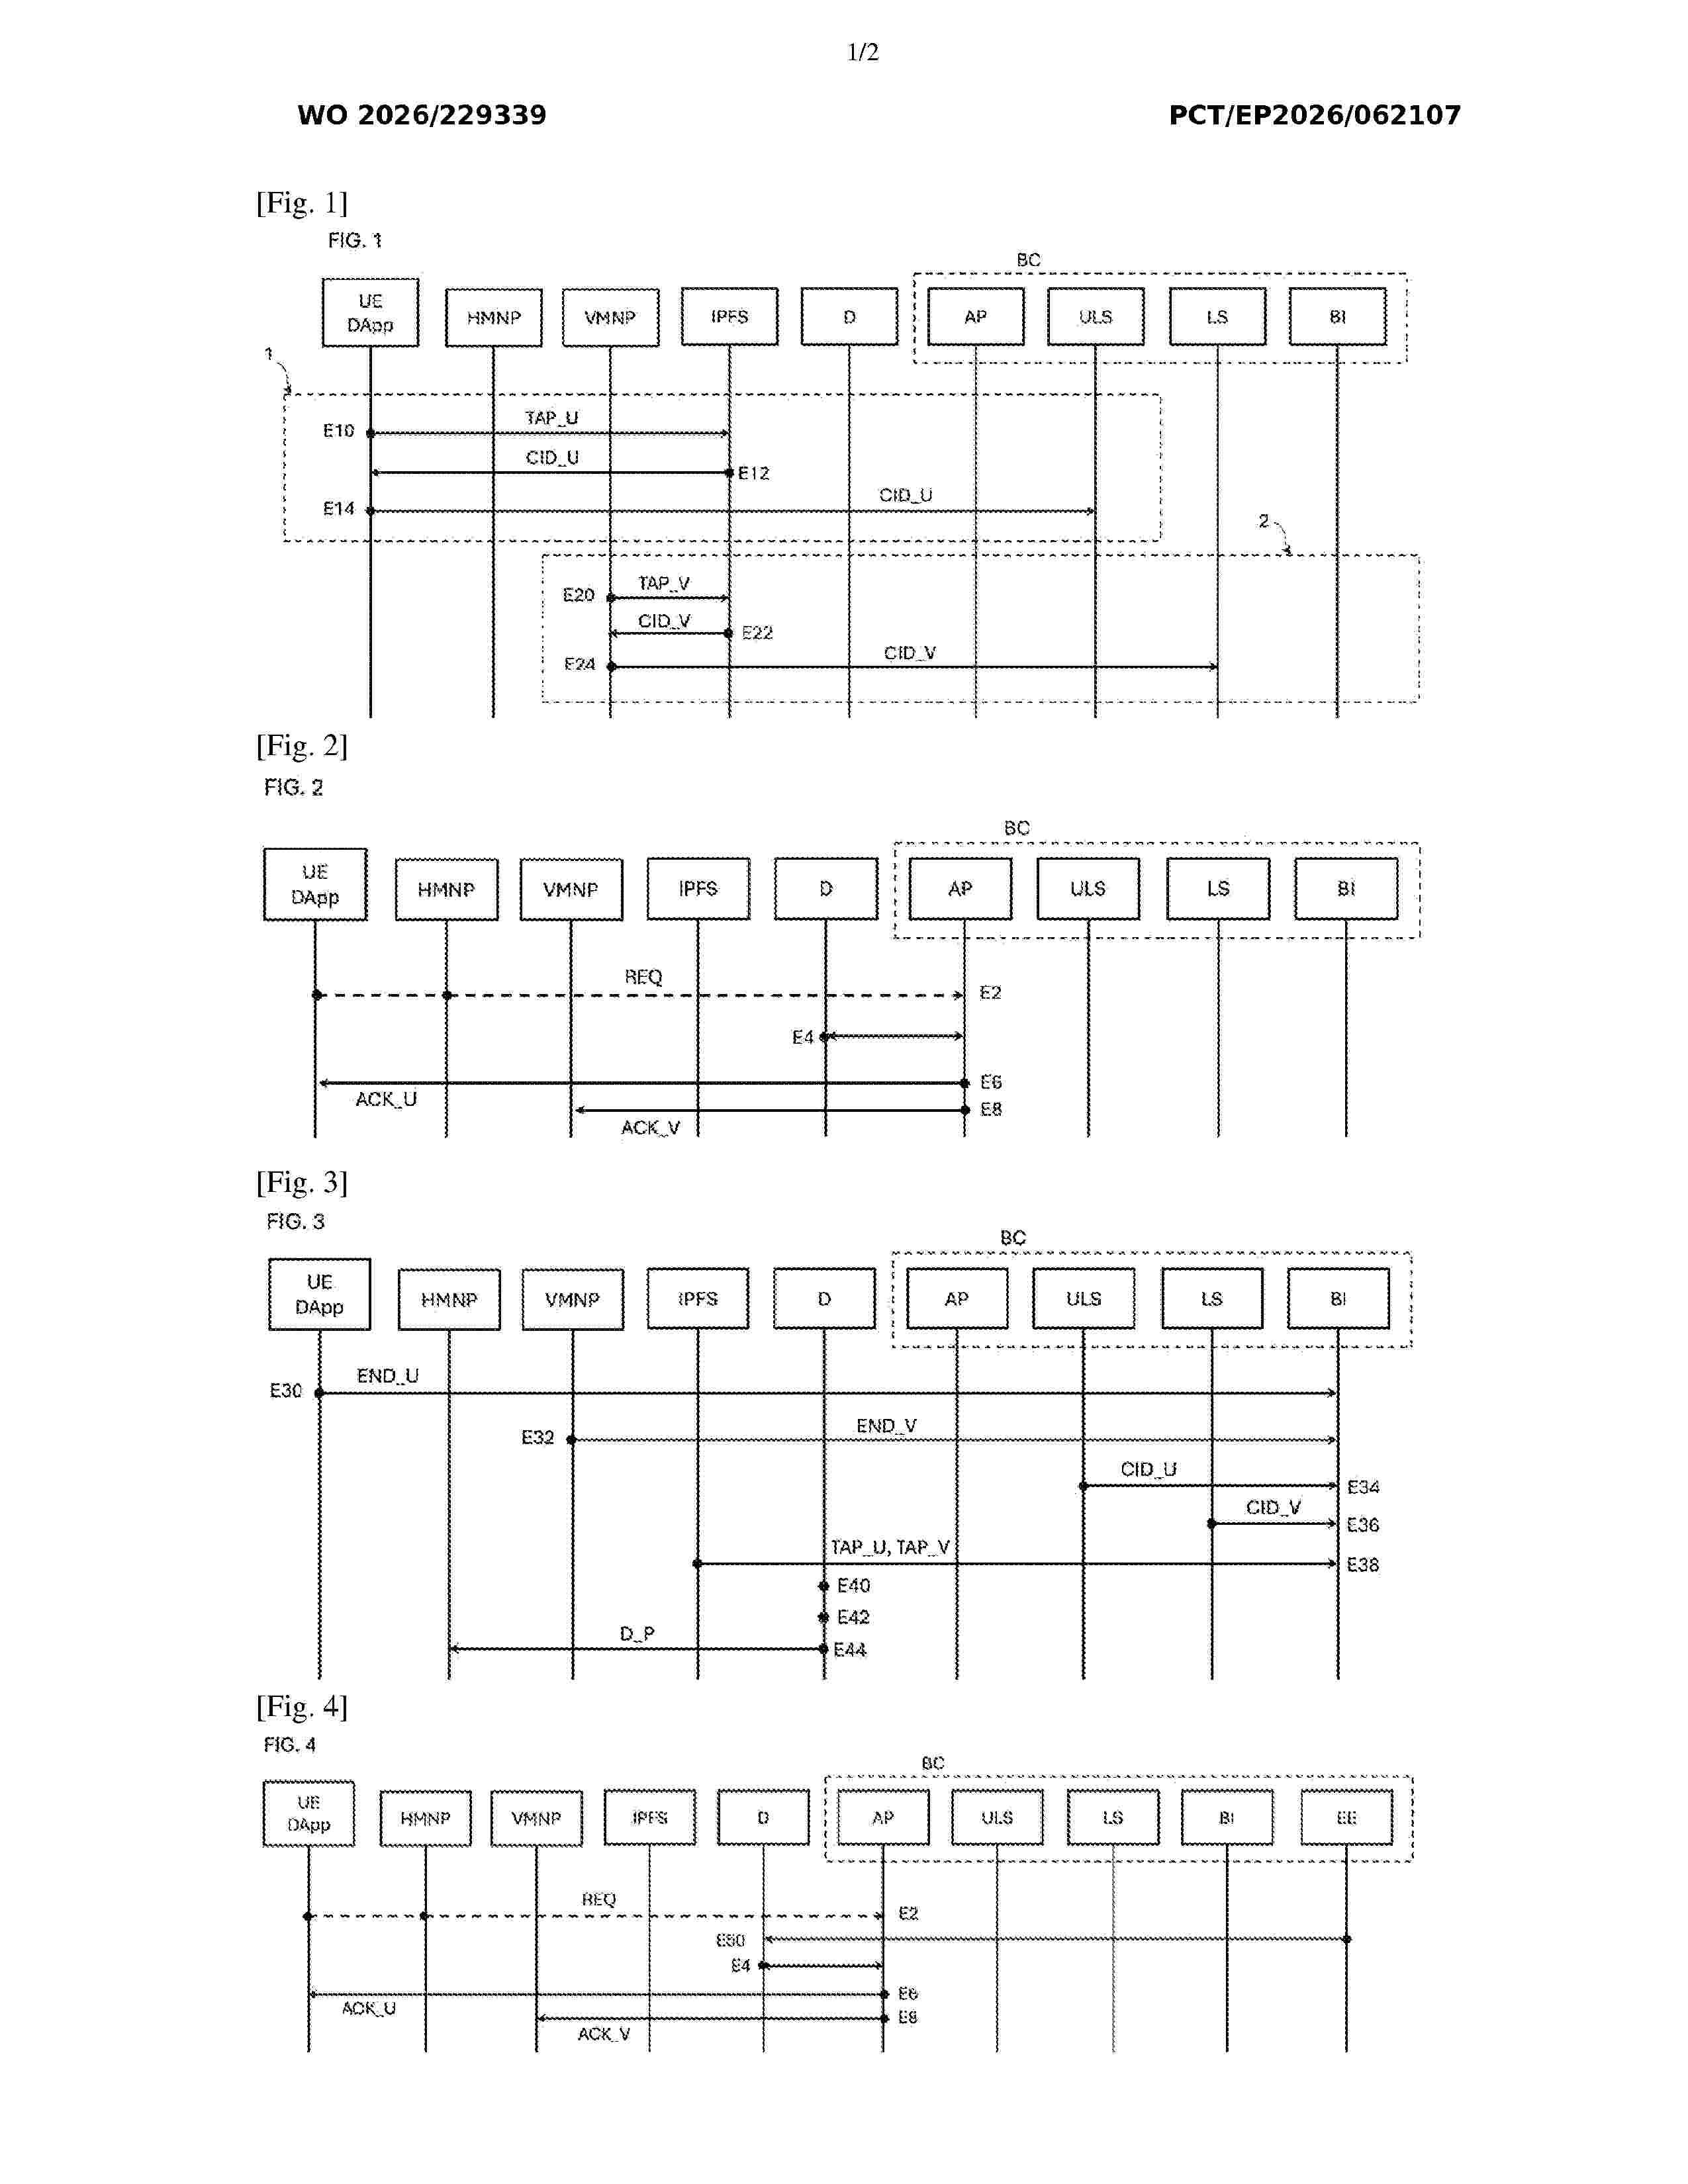
A roaming technique is implemented in a communication system comprising a home network (HPMN) and a visited network (VPMN). The UE terminal implements a decentralised application (DApp) and belongs to the home network and is attached to the visited network. The communication system comprises a blockchain (BC) with several smart contracts. The decentralized application and the visited network each implement, after accepting a roaming request made to a first smart contract (AP), at least one iteration of: - sending (E10), to an interplanetary file system (IPFS), a datum (TAP_U) representative of a use of the visited network by the terminal, - receiving (E12), from the IPFS, a content identifier (CID_U) subsequent to storage of the datum (TAP_U) in the IPFS. - upon receiving (E12) said content identifier, sending (E14), in a second smart contract (ULS), a message comprising said content identifier (CID_U).
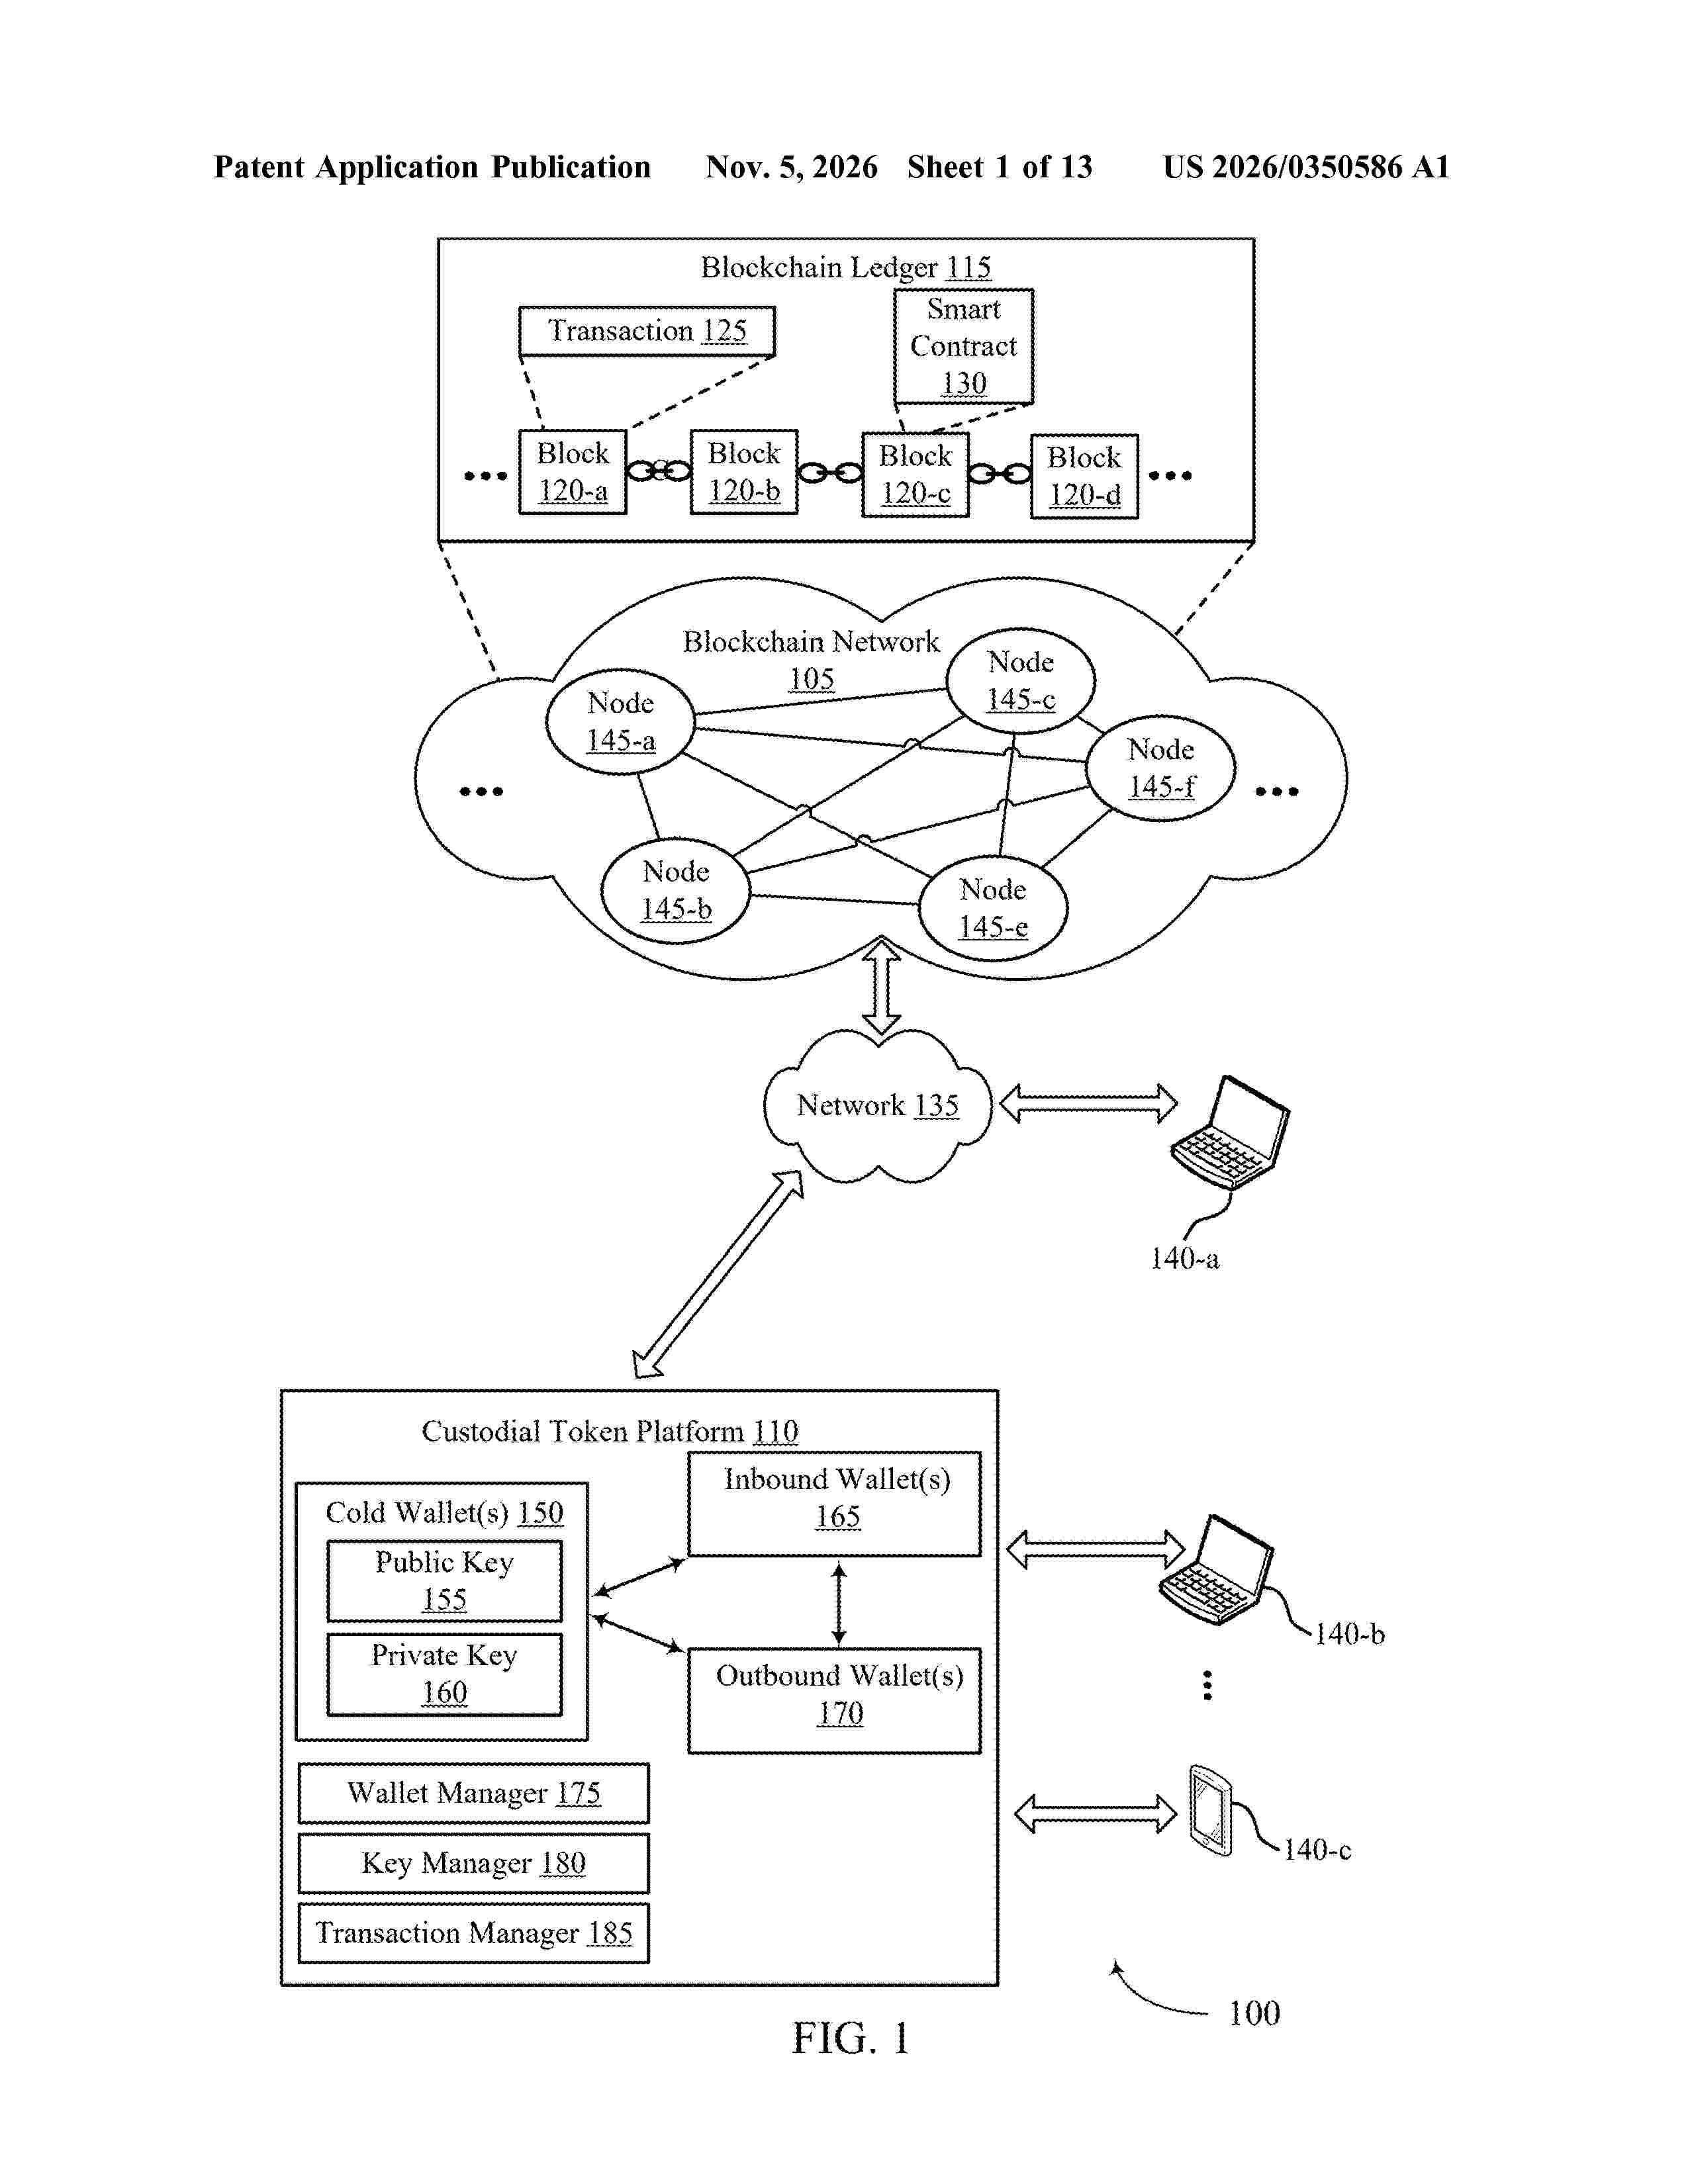
Resumen de: US20260350586A1
0000 Methods, systems, and devices for data management are described. A first user device for a blockchain network may communicate first signaling to initiate an import session for a blockchain wallet associated with a device-based passkey associated with a second user device, where the first signaling may include a random secret. The first user device may receive an indication that the import session is associated with the second user device and may generate a new passkey associated with the first user device. The first user device may transmit second signaling including an encrypted credential identifier associated with the new passkey, where the encrypted credential identifier may be encrypted based on the random secret. The second user device may sign a blockchain transaction authorizing access to the blockchain wallet using the new passkey, and the first user device may access the blockchain wallet using the new passkey.
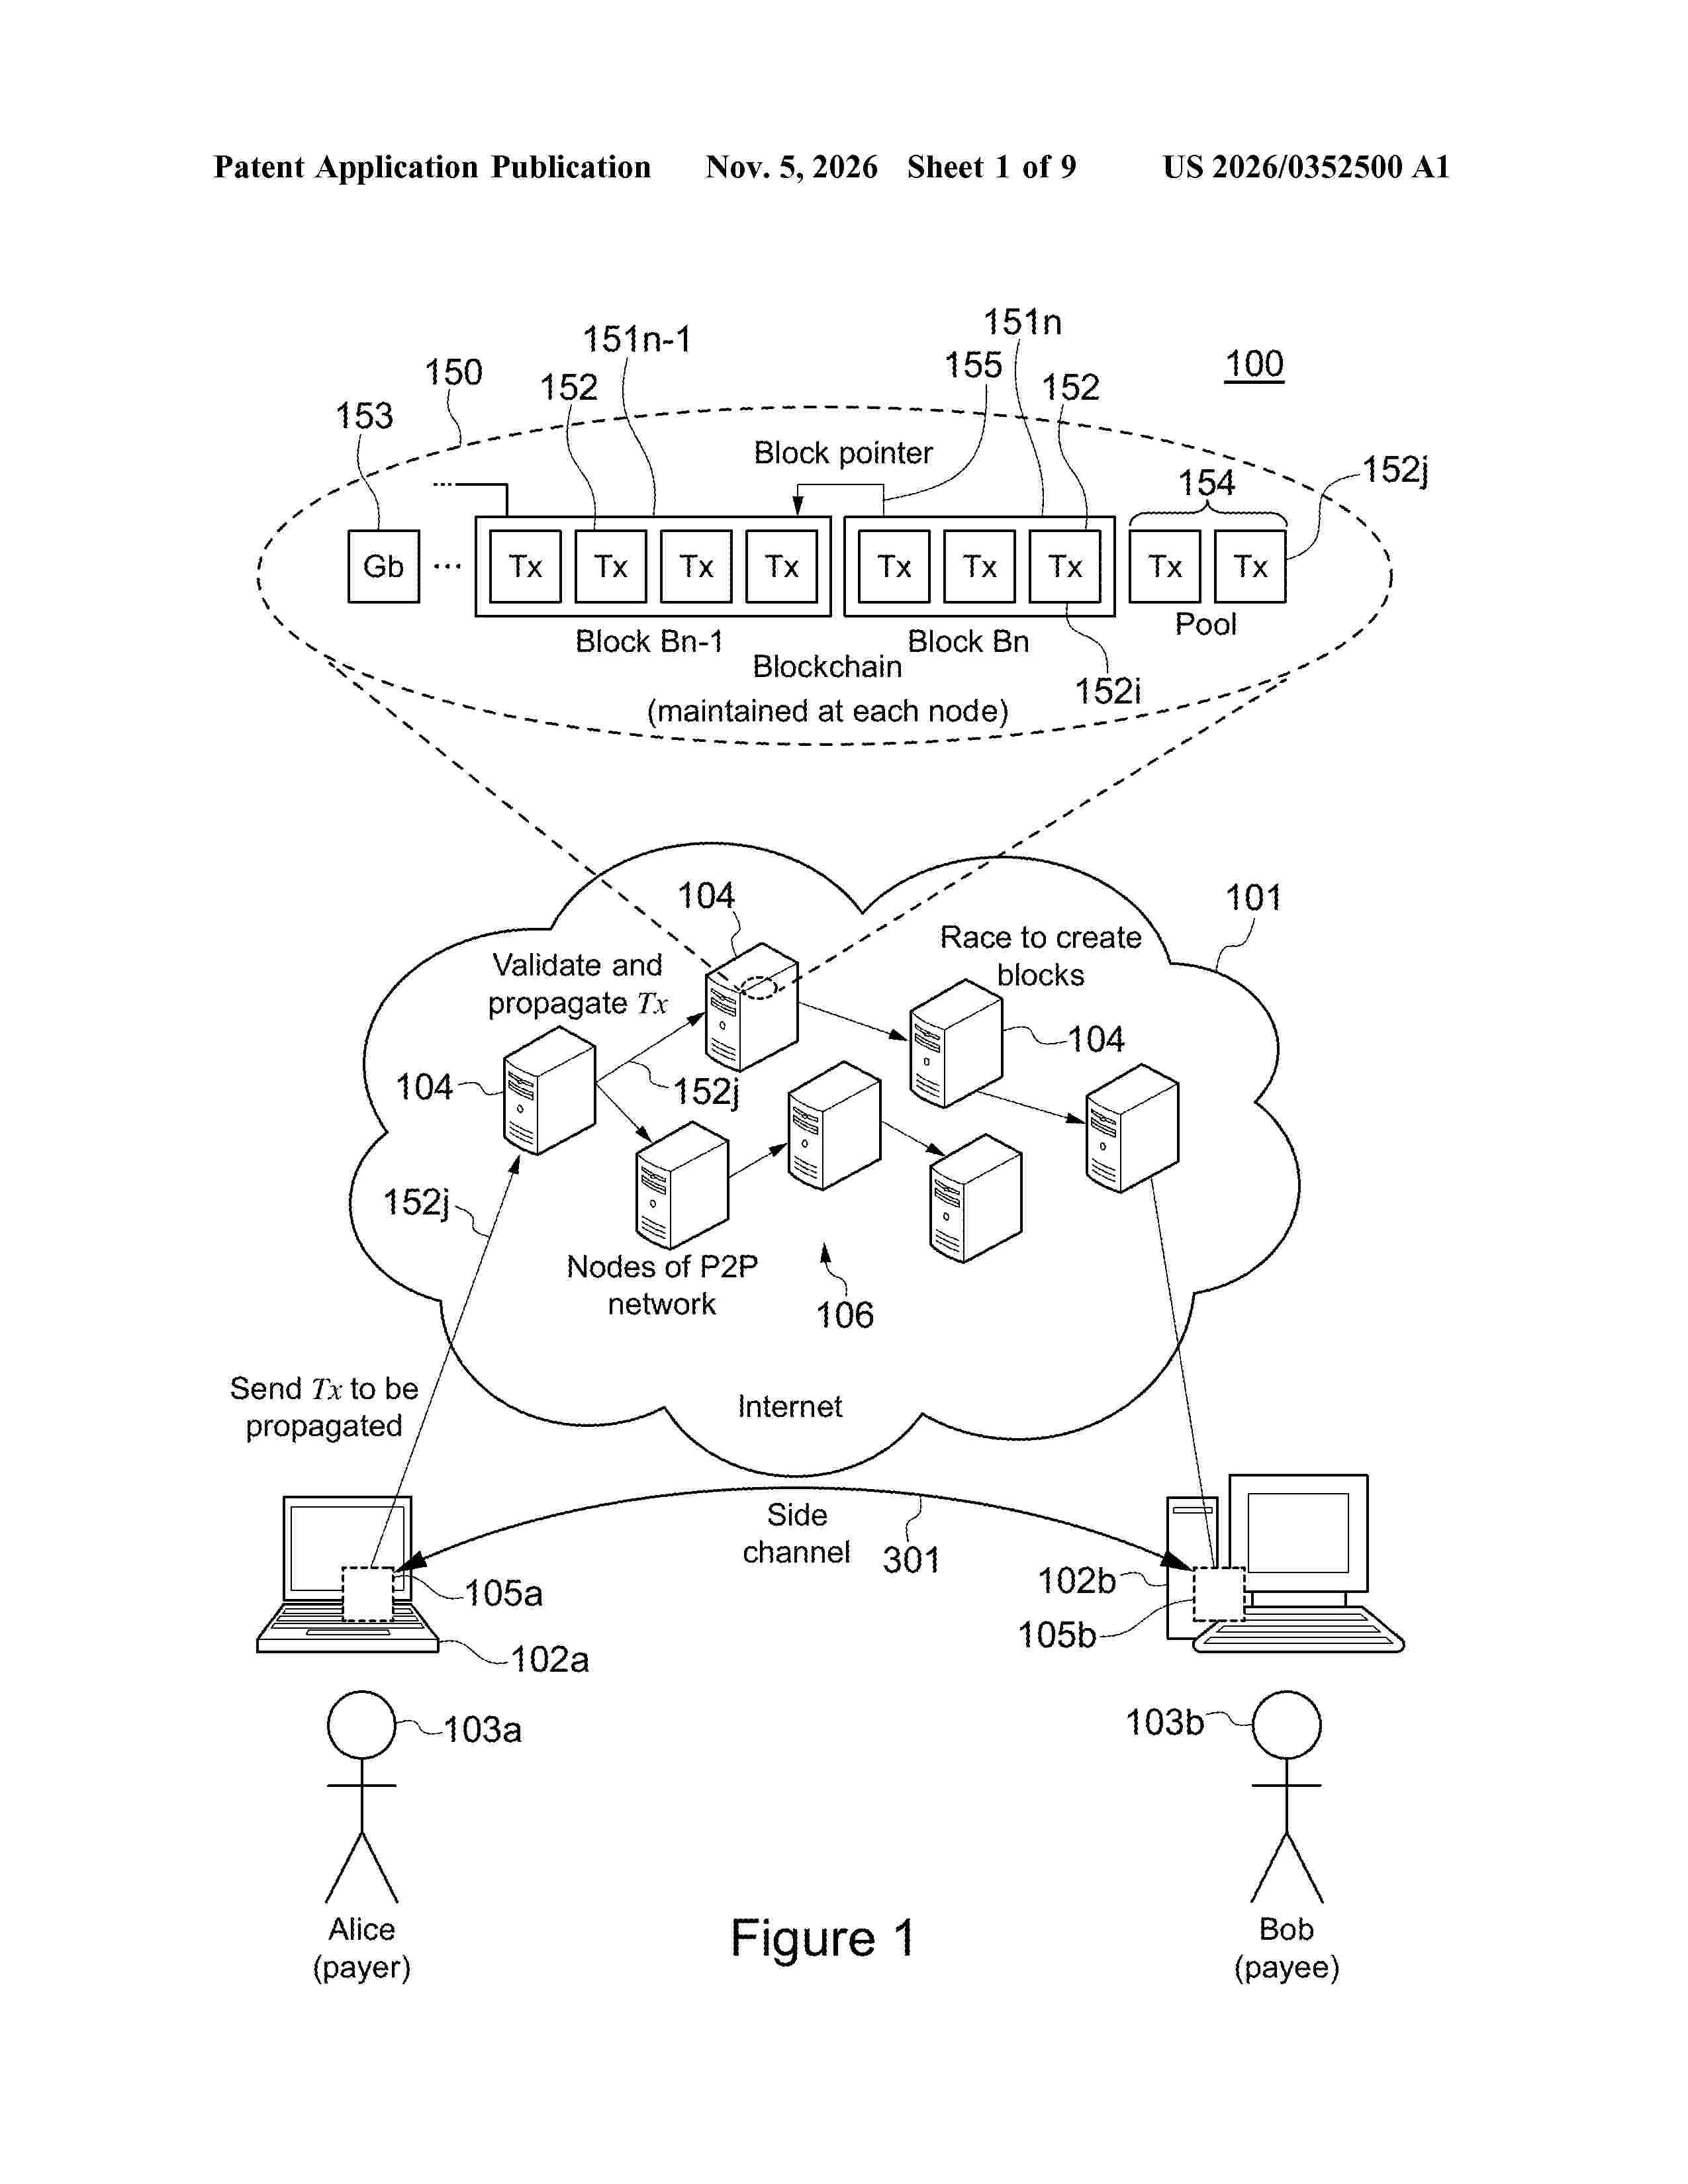
Resumen de: US20260352500A1
0000 Embodiments utilise Singular Value Decomposition (SVD) to provide improved techniques for generating, processing, controlling, transferring and/or implementing blockchain-based tokens and other assets. Such tokens may include, but are not limited to, non-fungible tokens (NFTs). In one possible embodiment, an SVD-based digital asset is created by applying SVD to one or more existing digital asset(s) e.g. image(s). In an alternative approach, the SVD-based digital asset can be created from an artificially constructed SVD rather than based on any existing digital asset(s). Embodiments are also provided for secure, encrypted transmission of digital assets and tokens between parties, and for improved storage and processing of such assets and tokens, in particular when storing/processing on a blockchain ledger.
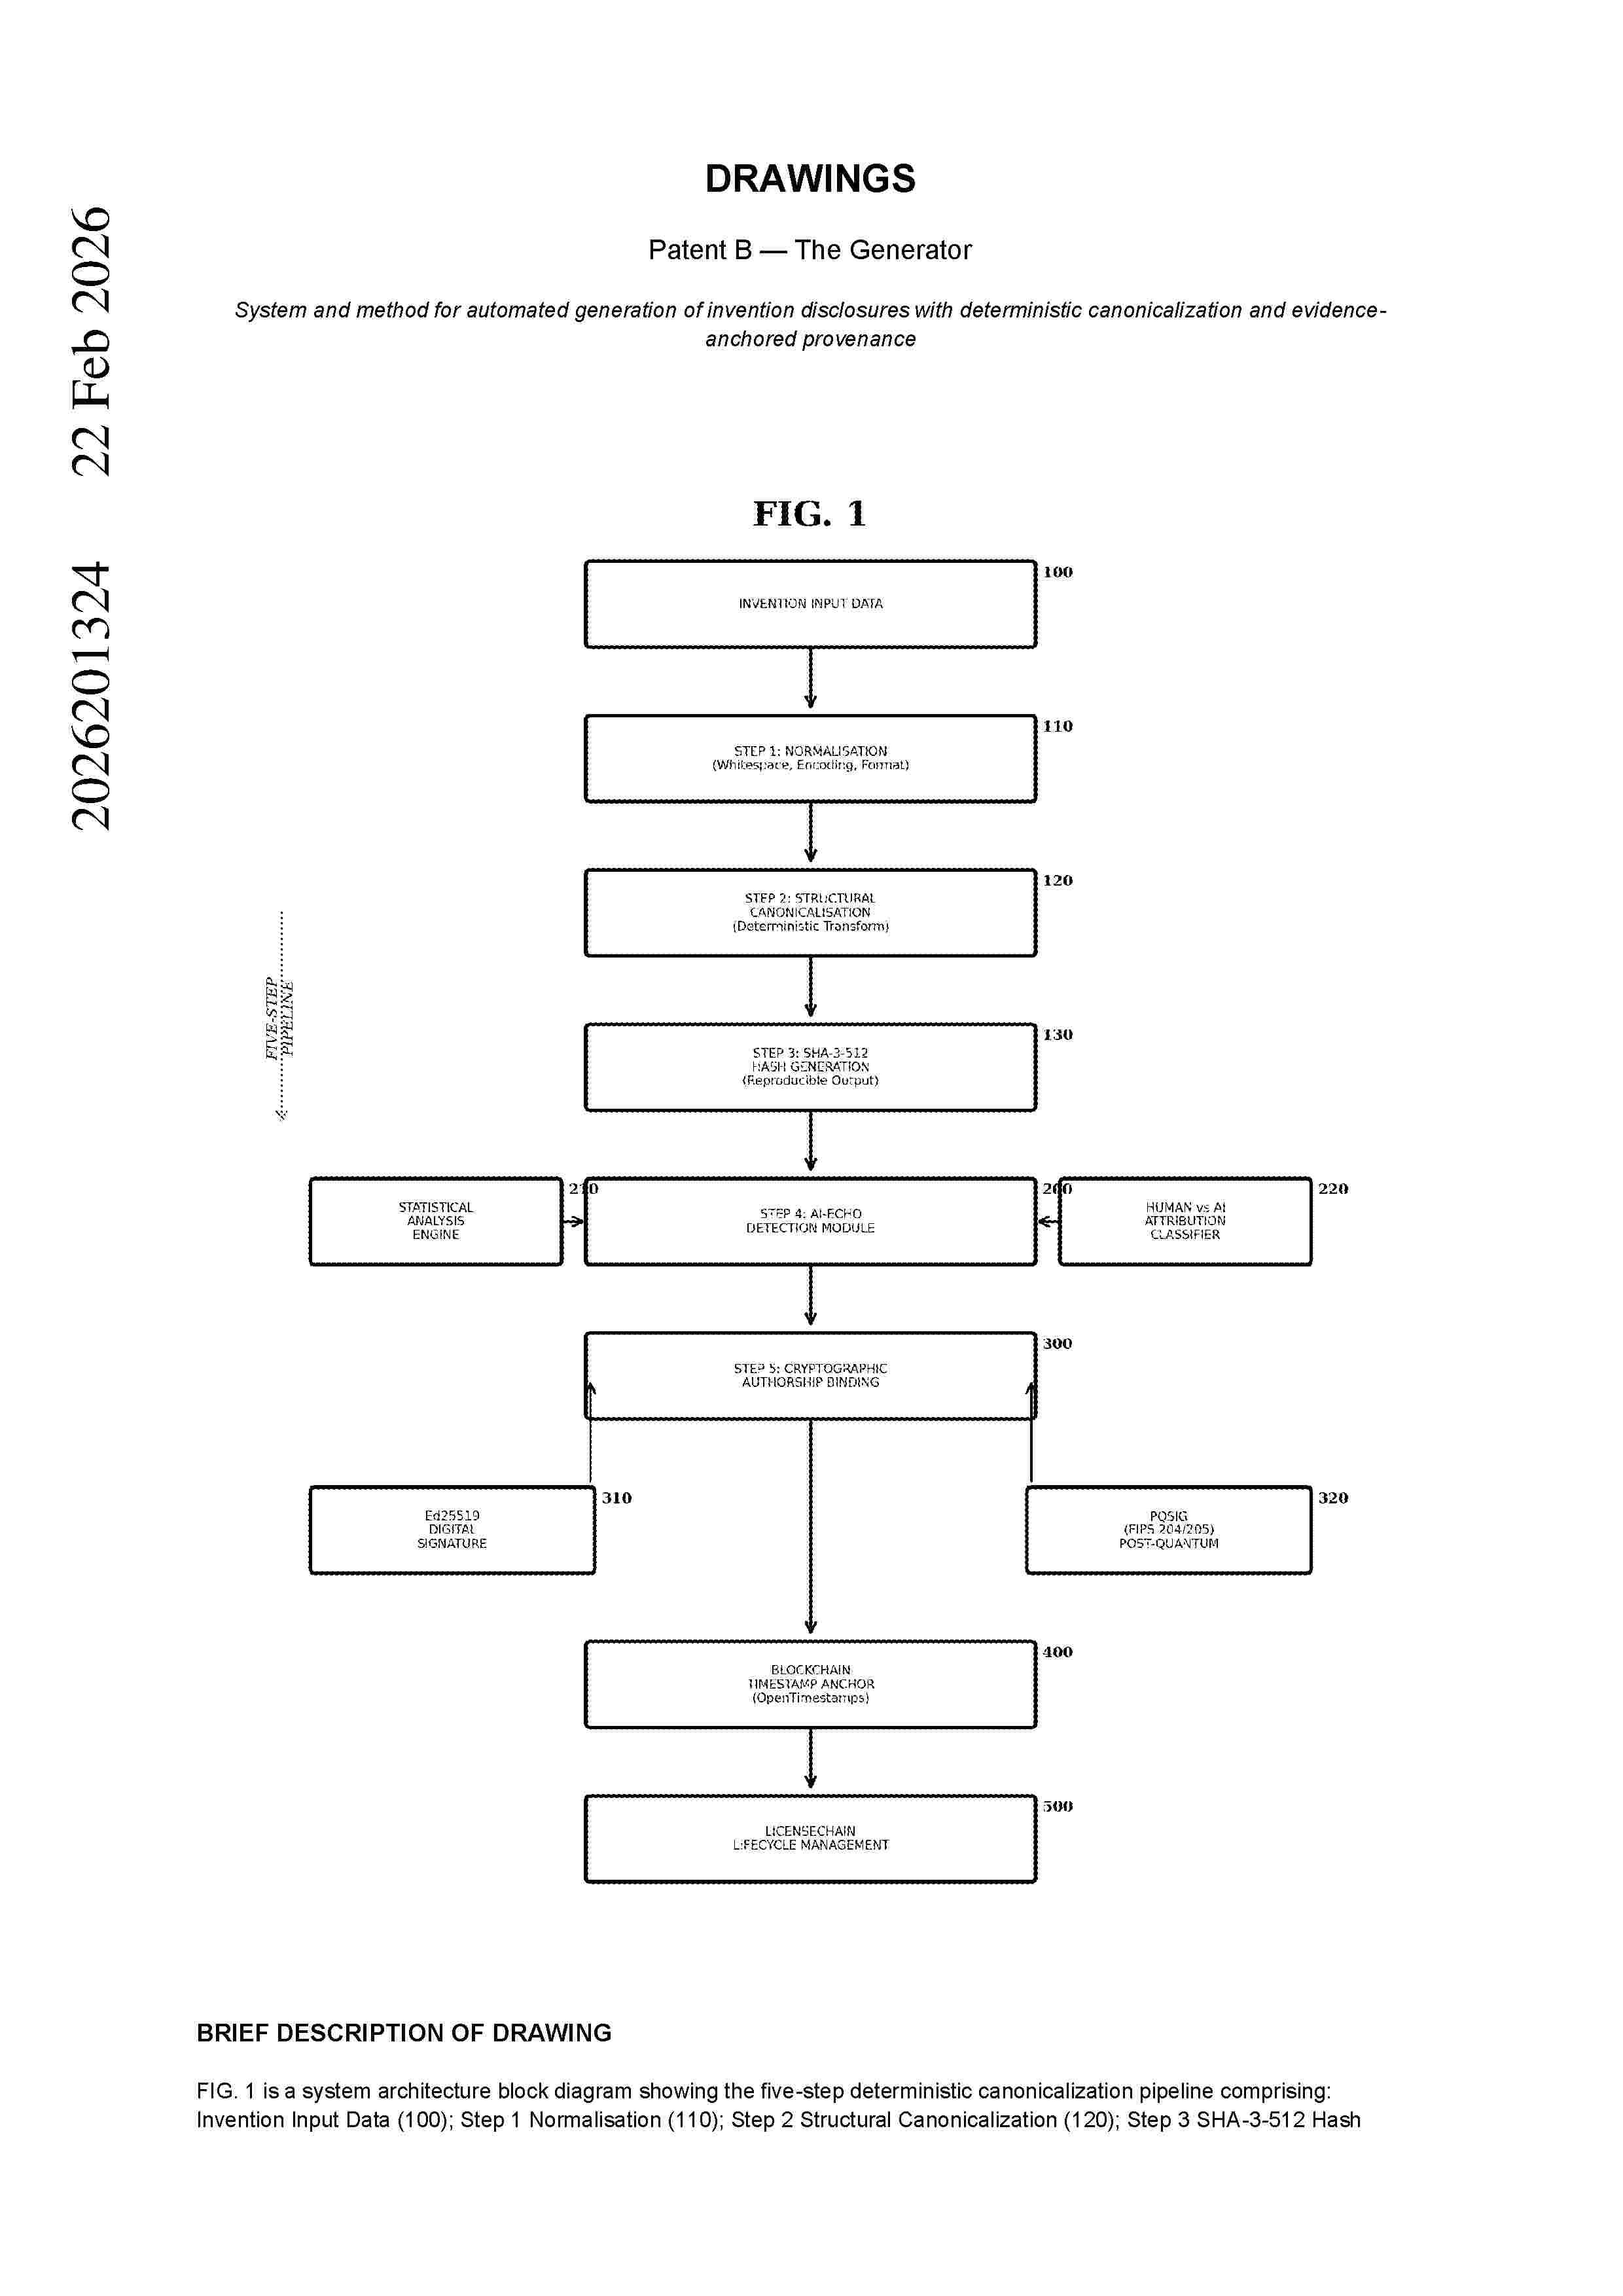
Resumen de: AU2026201324A1
A computer-implemented system and method for automated generation of invention disclosure documents with Deterministic Canonicalization and evidence-anchored provenance. The system receives structured invention input data comprising technical disclosures, claim elements, and supporting evidence, and applies a Deterministic Canonicalization transformation that removes generative variance — including whitespace irregularities, field ordering ambiguity, character encoding inconsistencies, and non-content metadata — to produce a legally binding, reproducible output hash. The canonicalized disclosure is bound to an authorship identity via SHA-3-512 hashing and digital signature using Ed25519 or a post-quantum scheme conforming to FIPS 204 (ML-DSA) or FIPS 205 (SLH-DSA). The system detects AI-generated content by analysing token distribution patterns and hallucination markers in submitted text. A licence enforcement module tracks derivative works through affinity analysis. All provenance events are recorded in a hash- chained evidence ledger anchored to a blockchain-based timestamping service. eb e b Patent B — The Generator System and method for automated generation of invention disclosures with deterministic canonicalization and evidence- anchored provenance BRIEF DESCRIPTION OF DRAWING FIG. 1 is a system architecture block diagram showing the five-step deterministic canonicalization pipeline comprising: Invention Input Data (100); Step 1 Normalisation (110); Step 2 Structu
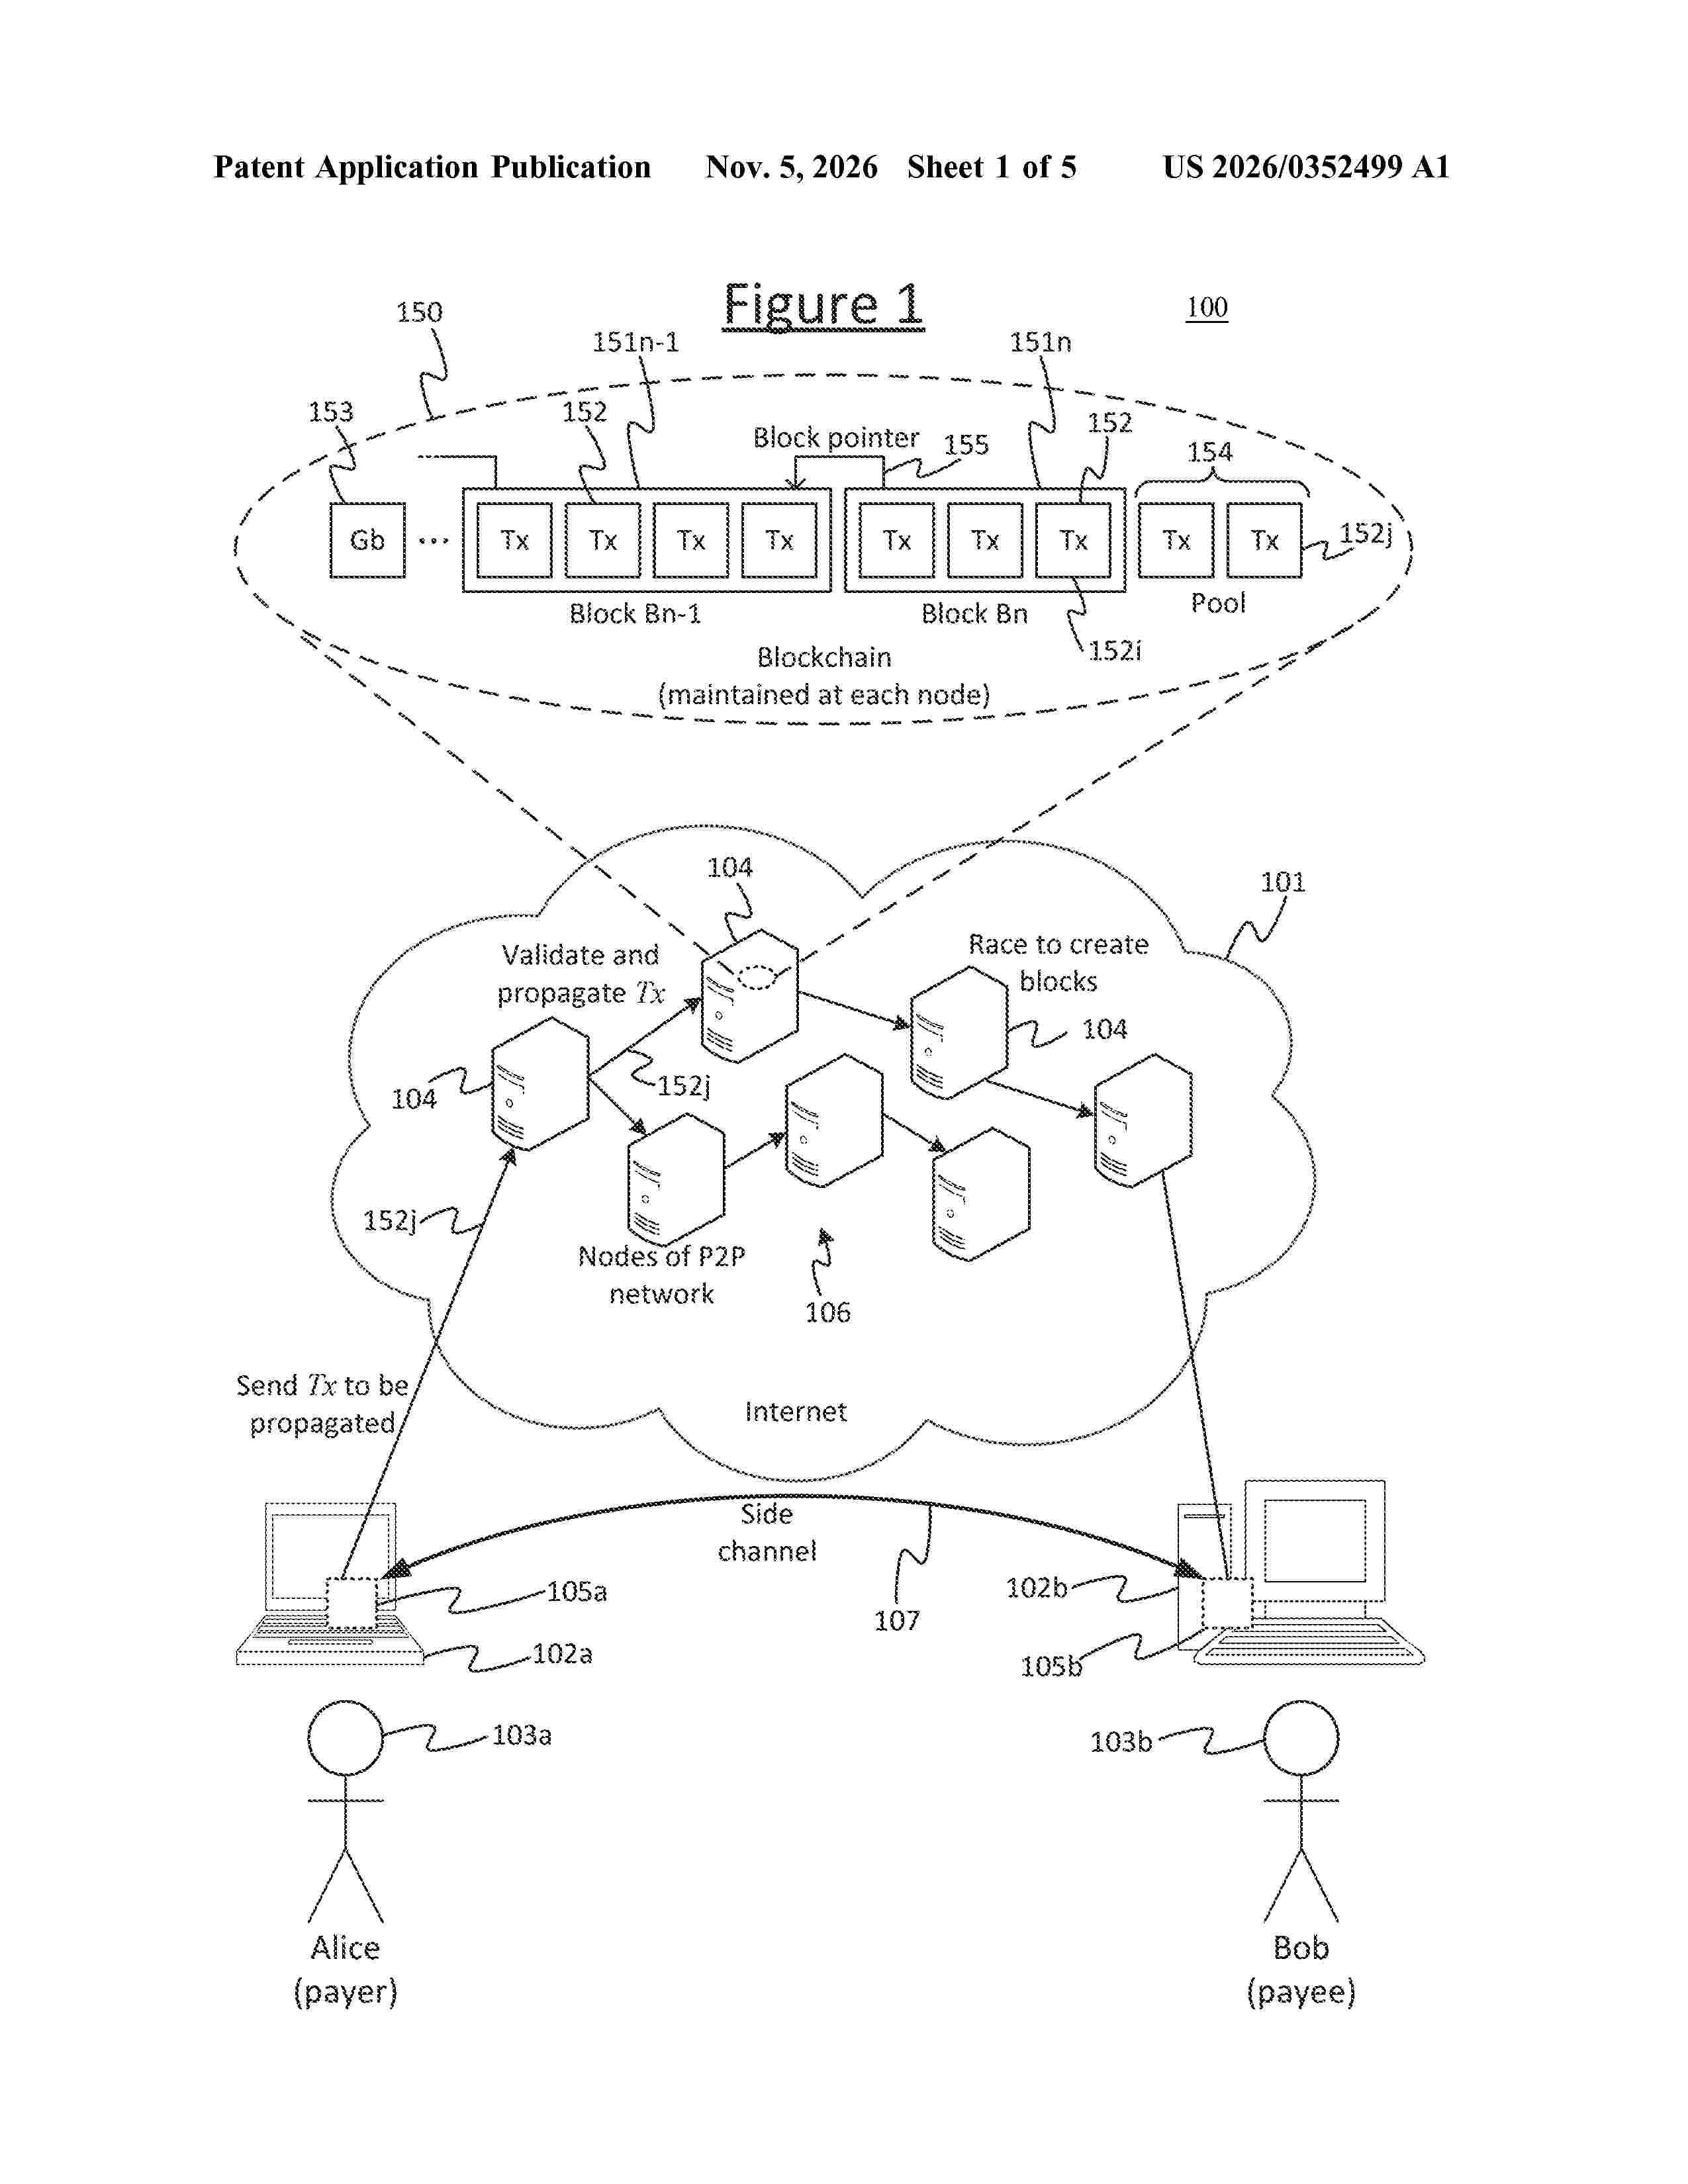
Resumen de: US20260352499A1
0000 A computer-implemented method of obtaining application-related data, wherein the method is performed by a first party and comprises: determining a first multicast network address associated with a first application; and obtaining, using the first multicast address, one or more respective blockchain transactions and/or one or more respective proof of inclusions, each respective proof of inclusion associated with a respective blockchain transaction, wherein each respective blockchain transaction comprises respective data related to the first application.
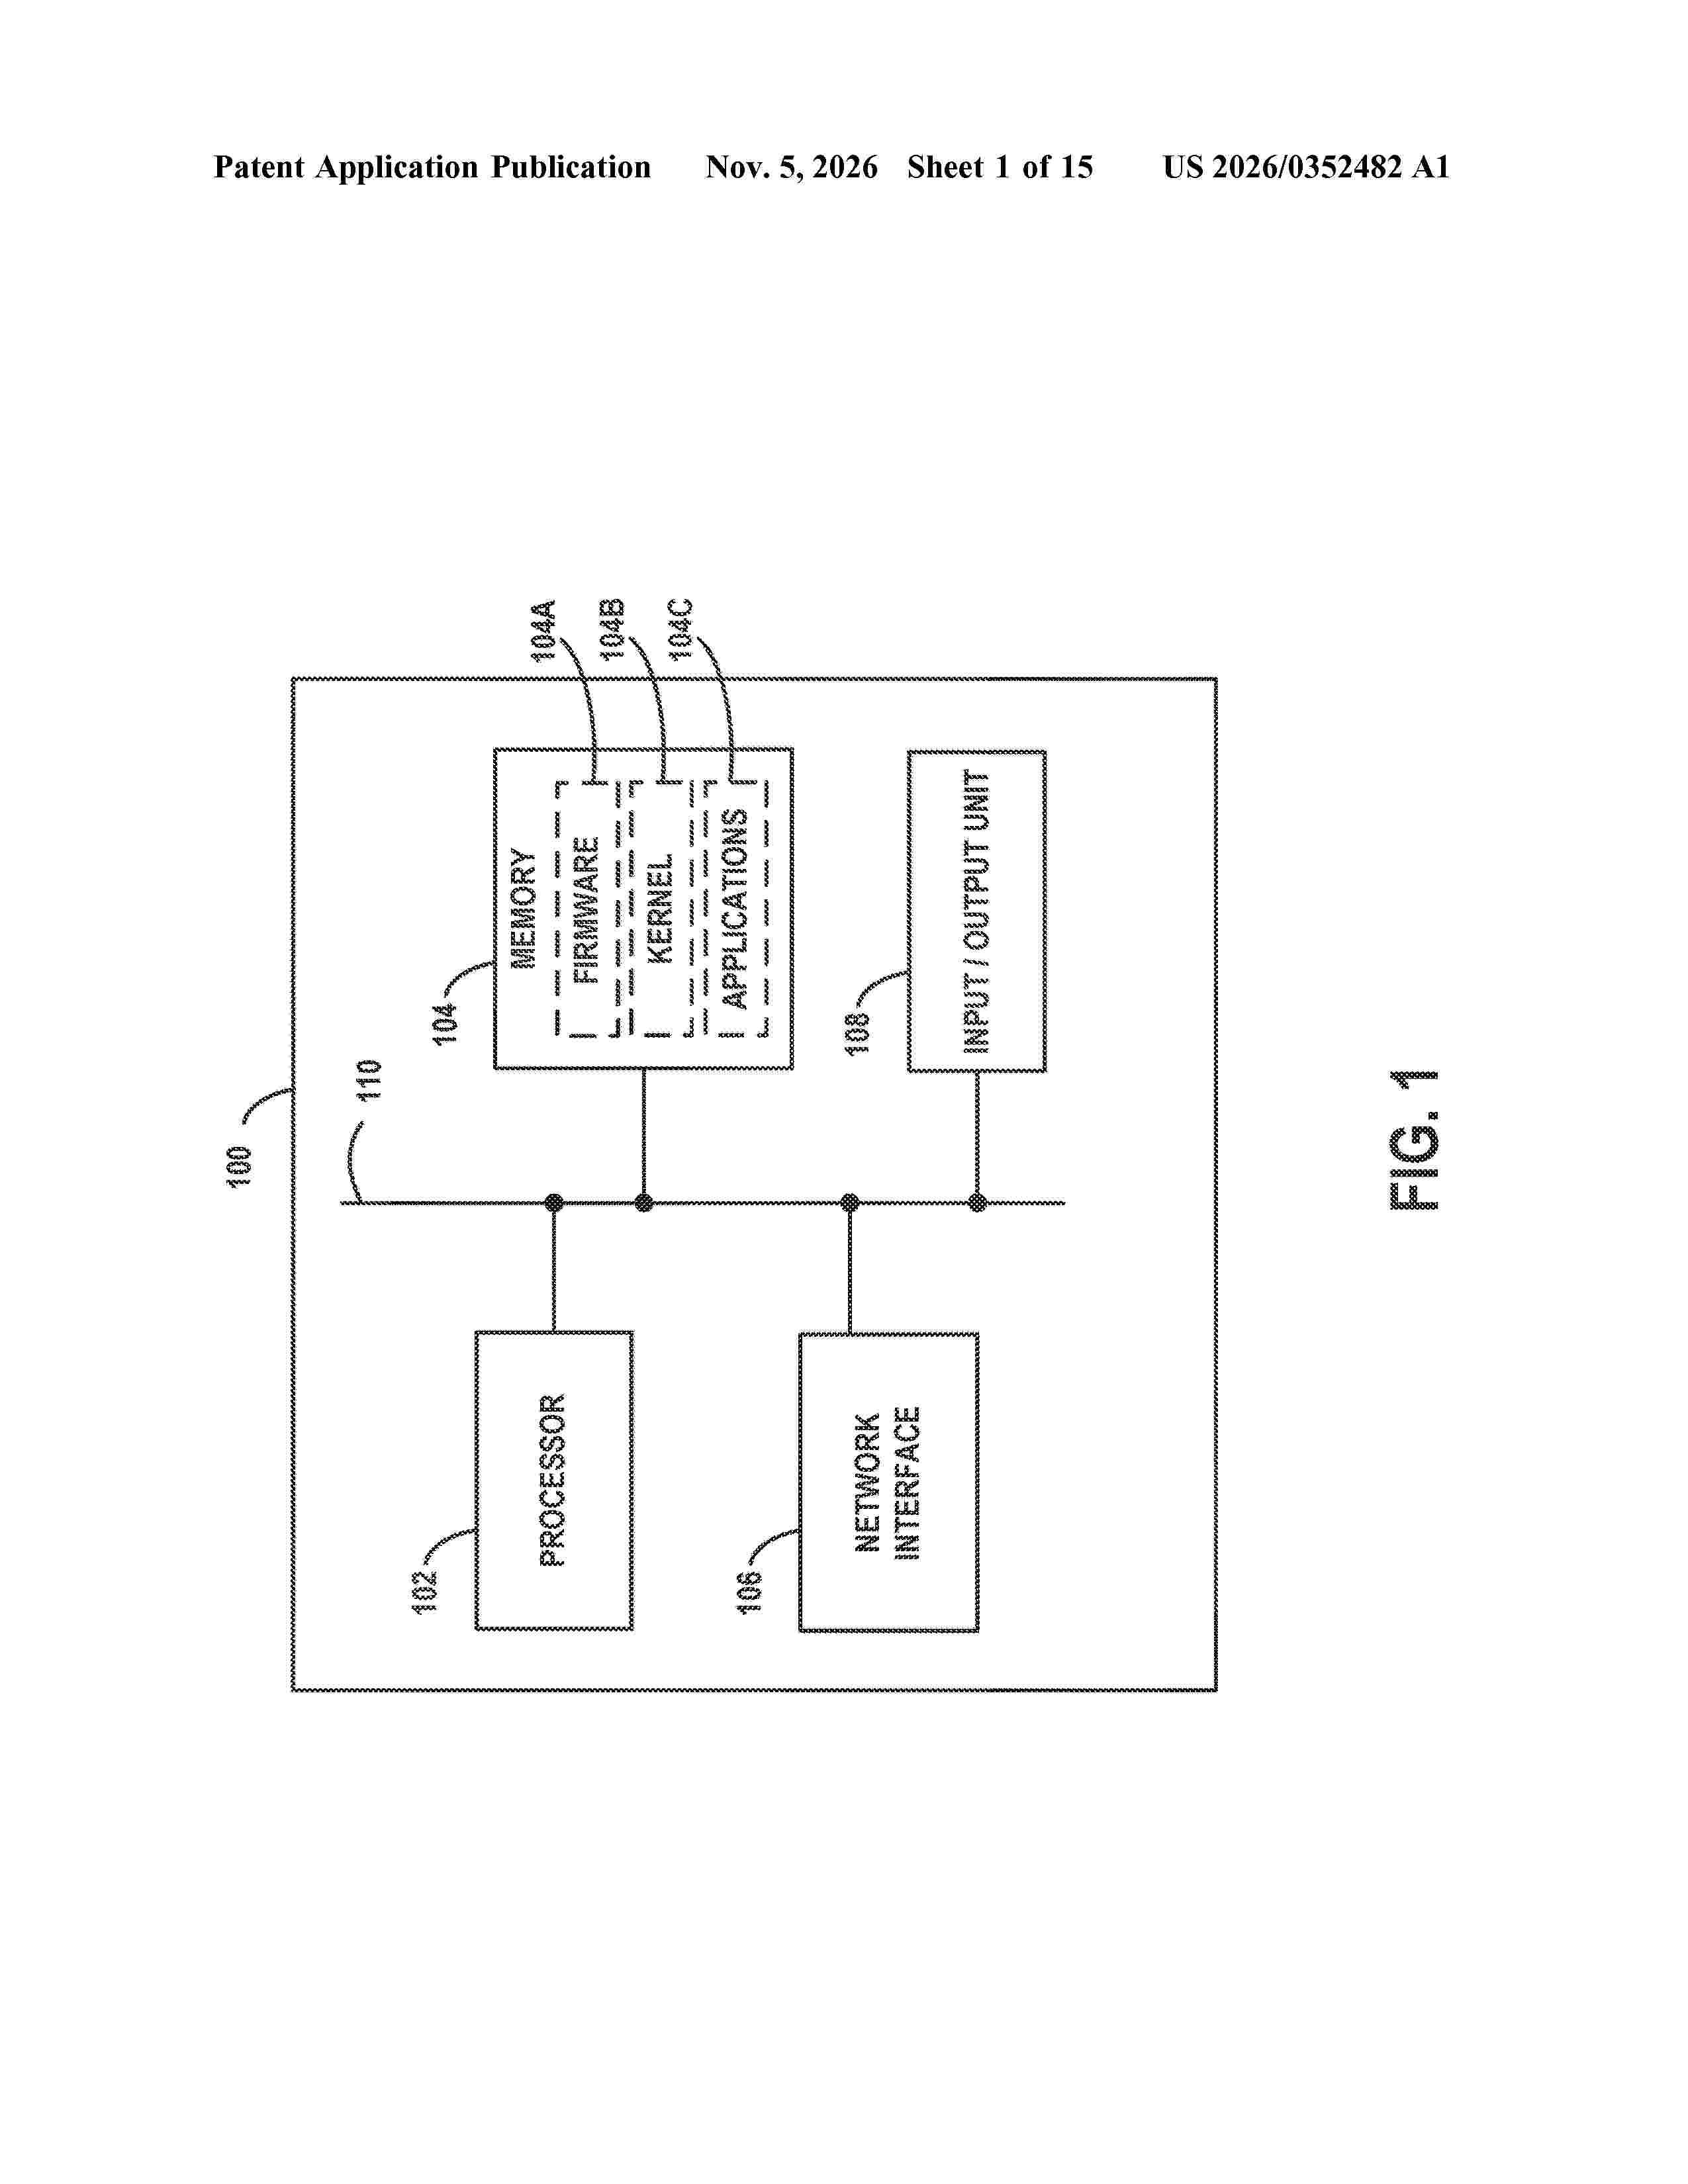
Nº publicación: US20260352482A1 05/11/2026
Solicitante:
KANOVITZ MICHAEL IRA [US]
LOEVY JON ISAAC [US]
Kanovitz Michael Ira
Loevy Jon Isaac
Resumen de: US20260352482A1
0000 Example implementations may include: obtaining a first identifier relating to a first entity, wherein the first identifier uniquely identifies the first entity within a backwardly-immutabie cryptographic sequence of data blocks: exchanging, between the first entity and a second, entity; a set of conditions, wherein a second identifier uniquely identifies the second entity within the data blocks; receiving, from the first entity and the second entity, acceptances of tiie set of conditions; generating a self-executing unit of program logic that contains the first identifier, the second identifier, a representation of the set of conditions, and a third identifier that uniquely identifies a third entity having authority to suspend, modify, or override execution of the program logic; adding, as a new data block, the self-executing unit of program logic on the data blocks; and notifying one or more of the first entity or second entity of the self-executing unit of program logic.
 BOPI
 Sede Electrónica